Cephalus
- 193
- Global rank
- 157
- Month rank
- 192
- Week rank
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
- Ransomware
- Type
- Unknown
- Origin
- 1 August, 2025
- First seen
- 30 September, 2026
- Last seen
How to analyze Cephalus with ANY.RUN
IOCs
IP addresses
- 150.171.109.99
- 34.107.243.93
- 52.123.243.201
- 199.232.210.172
- 51.75.242.210
- 2.23.246.9
- 2.16.204.151
- 150.171.28.11
- 34.149.226.178
- 2.16.204.147
- 23.11.40.157
- 149.137.141.9
- 128.24.231.65
- 142.251.152.119
- 48.209.133.15
- 151.101.129.91
- 48.192.1.65
- 45.112.123.126
- 95.100.102.101
- 57.153.246.3
Hashes
- 81b2bd4ea98c8db66554fbc8d7637a1a69a130f331feb732b75caab4c4868fd5
- 20de375707692099b3132084695377ce5fec0aec05813dedcce094b8eda44386
- 6a437098dcbb8a0354ae28a5f7825685f471c13cecb83186cc950844df7c76c4
- 7bfbc8202b8cdbdcc597a0e789240f0dc0b0e94fa6597e576eaf436bc6223e18
- 44071e0fcffb9a9a32e8fa7010bb18dbc41afd0b176f81bf700b15b638a88a51
- 696e930706b5d391eb8778f73b0627ffc2be7f6c9a3e7659170d9d37fc4a97b5
- 40a0628e5673cd81d91142b1b7db3cd9e472efceb1b464dd90c0ca9f627623f2
- 25b8bdf1e2b463c97e8e668a235df4396e866d25291667d89762d936bd92e836
- 8c8f1c09d18fcc5c81a00e9b895a6672300bd343e3e63d850b2f15464cb70b52
- 2689f0f6efb979bc1f77d78aaf253b71af5aef9286ef80d394abe9f3180a4100
- 6bace0c1b92c585dd981408e1c2c5060496aa4eebd9f4075412ec8ac2b4a8f2d
- 08d04160a0ab6c875989edf9ab5ada05b0bbb5abc7035373c88bc90a2667d5e0
- 951f7030a5334d71b10a4a7018fa86a8518b08fa6fe82fa0b5a06412e55e33a1
- 3e6852a70f7ae9eea3c2857c7564a62c8d4e571664bdd3738a3066a21214ffe7
- b7f866ace922e9a8cd258543e4dd7dd2a24aa0af26494c32b0090ac27529772d
- d1189b6537a23dabc5aa3a4fcd72ebf2e49ac8f0f5c3c381c123460756f2989e
- 07418677217cbad52f4fc2a39bf18d8735c8a4d22ee700c5d51caa875f57b12a
- 1d25654d91d1be23c4621c69899c619fa6ec6e9014fdd4d4ab749567874a5a5c
- 5569935b29c792243adfbd15f128d2db17c79df01512dd96dd6e41509b70bc7d
- cda1037c166c85e5d92f4362e1505bb2bf0e8f58a9e421055e2829feebbbd11b
Domains
- msedge.b.tlu.dl.delivery.mp.microsoft.com
- settings-win.data.microsoft.com
- www.bing.com
- ads-img.mozilla.org
- api.edgeoffer.microsoft.com
- login.live.com
- www.microsoft.com
- crl.microsoft.com
- mozilla.map.fastly.net
- content-signature-2.cdn.mozilla.net
- s.gofile.io
- ecs.office.com
- trip.prf.hn
- example.org
- safebrowsing.googleapis.com
- api.gofile.io
- firefox.settings.services.mozilla.com
- push.services.mozilla.com
- tagesschau.de
- static.edge.microsoftapp.net
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:jogm5oyi19neiv6btykiu8wt4hebojkhveltvduv2pm&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=at
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://s3.us-east-005.backblazeb2.com/vx-underground-main/malware%20analysis/2025/2025-12-24%20-%20detecting%20and%20responding%20to%20cephalus%20ransomware%20with%20wazuh/samples/a34acd47127196ab867d572c2c6cf2fcccffa3a7a87e82d338a8efed898ca722.7z?x-amz-algorithm=aws4-hmac-sha256&x-amz-credential=005e2c099359ccf0000000004%2f20260930%2fus-east-1%2fs3%2faws4_request&x-amz-date=20260930t104019z&x-amz-expires=3600&x-amz-signedheaders=host&x-amz-signature=d126b745776256034249074bc4d9d89b460b507d1efeebf1daafa6b8abfbb252
- https://copilot.microsoft.com/c/api/user/eligibility
- https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
- https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d285%2526e%253d1
- https://update.googleapis.com/service/update2/json?cup2key=14:qy2tpvrn1gbftl0cqv1eykg4pvddxlwhcs9jkj8hwdw&cup2hreq=848d3391ca5ce9037a908b868ba43d5b2bac865e9ea970ab518e0fc117dfa3f6
- https://clients2.googleusercontent.com/crx/blobs/azpvhcqildrgqxyclcenwovmaua7lwu2mln7dephdl7eqkp9gczqmiehkjncu7a_eigr4ip8elijgyg1mgbqewwsojngu_j8zva9cfi_aj--ikwjbypwnpfv9nmzws17bigaxlka5c7tdptpcgaddf44n1nzr3cqv7qk/ghbmnnjooekpmoecnnnilnnbdlolhkhi_1_110_1_0.crx
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
- https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
- https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
- https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
- https://edge.microsoft.com/abusiveadblocking/api/v1/blocklist
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
Last seen at
Cephalus Ransomware: New Threat Abusing Legitimate Files
Key Takeaways
- Discovered in mid-2025, Cephalus is a novel ransomware strain targeting organizations across various sectors, including IT, healthcare and finance.
- Its attack methods combine the abuse of compromised Remote Desktop Protocol (RDP) credentials with DLL sideloading.
- Cephalus applies a targeted approach and tailors malware to their victims, making detection more complex.
- Upon infiltration of targeted networks, it deactivates security software and erases backups.
- Such a tailored approach and backup erasure make the recovery especially challenging.
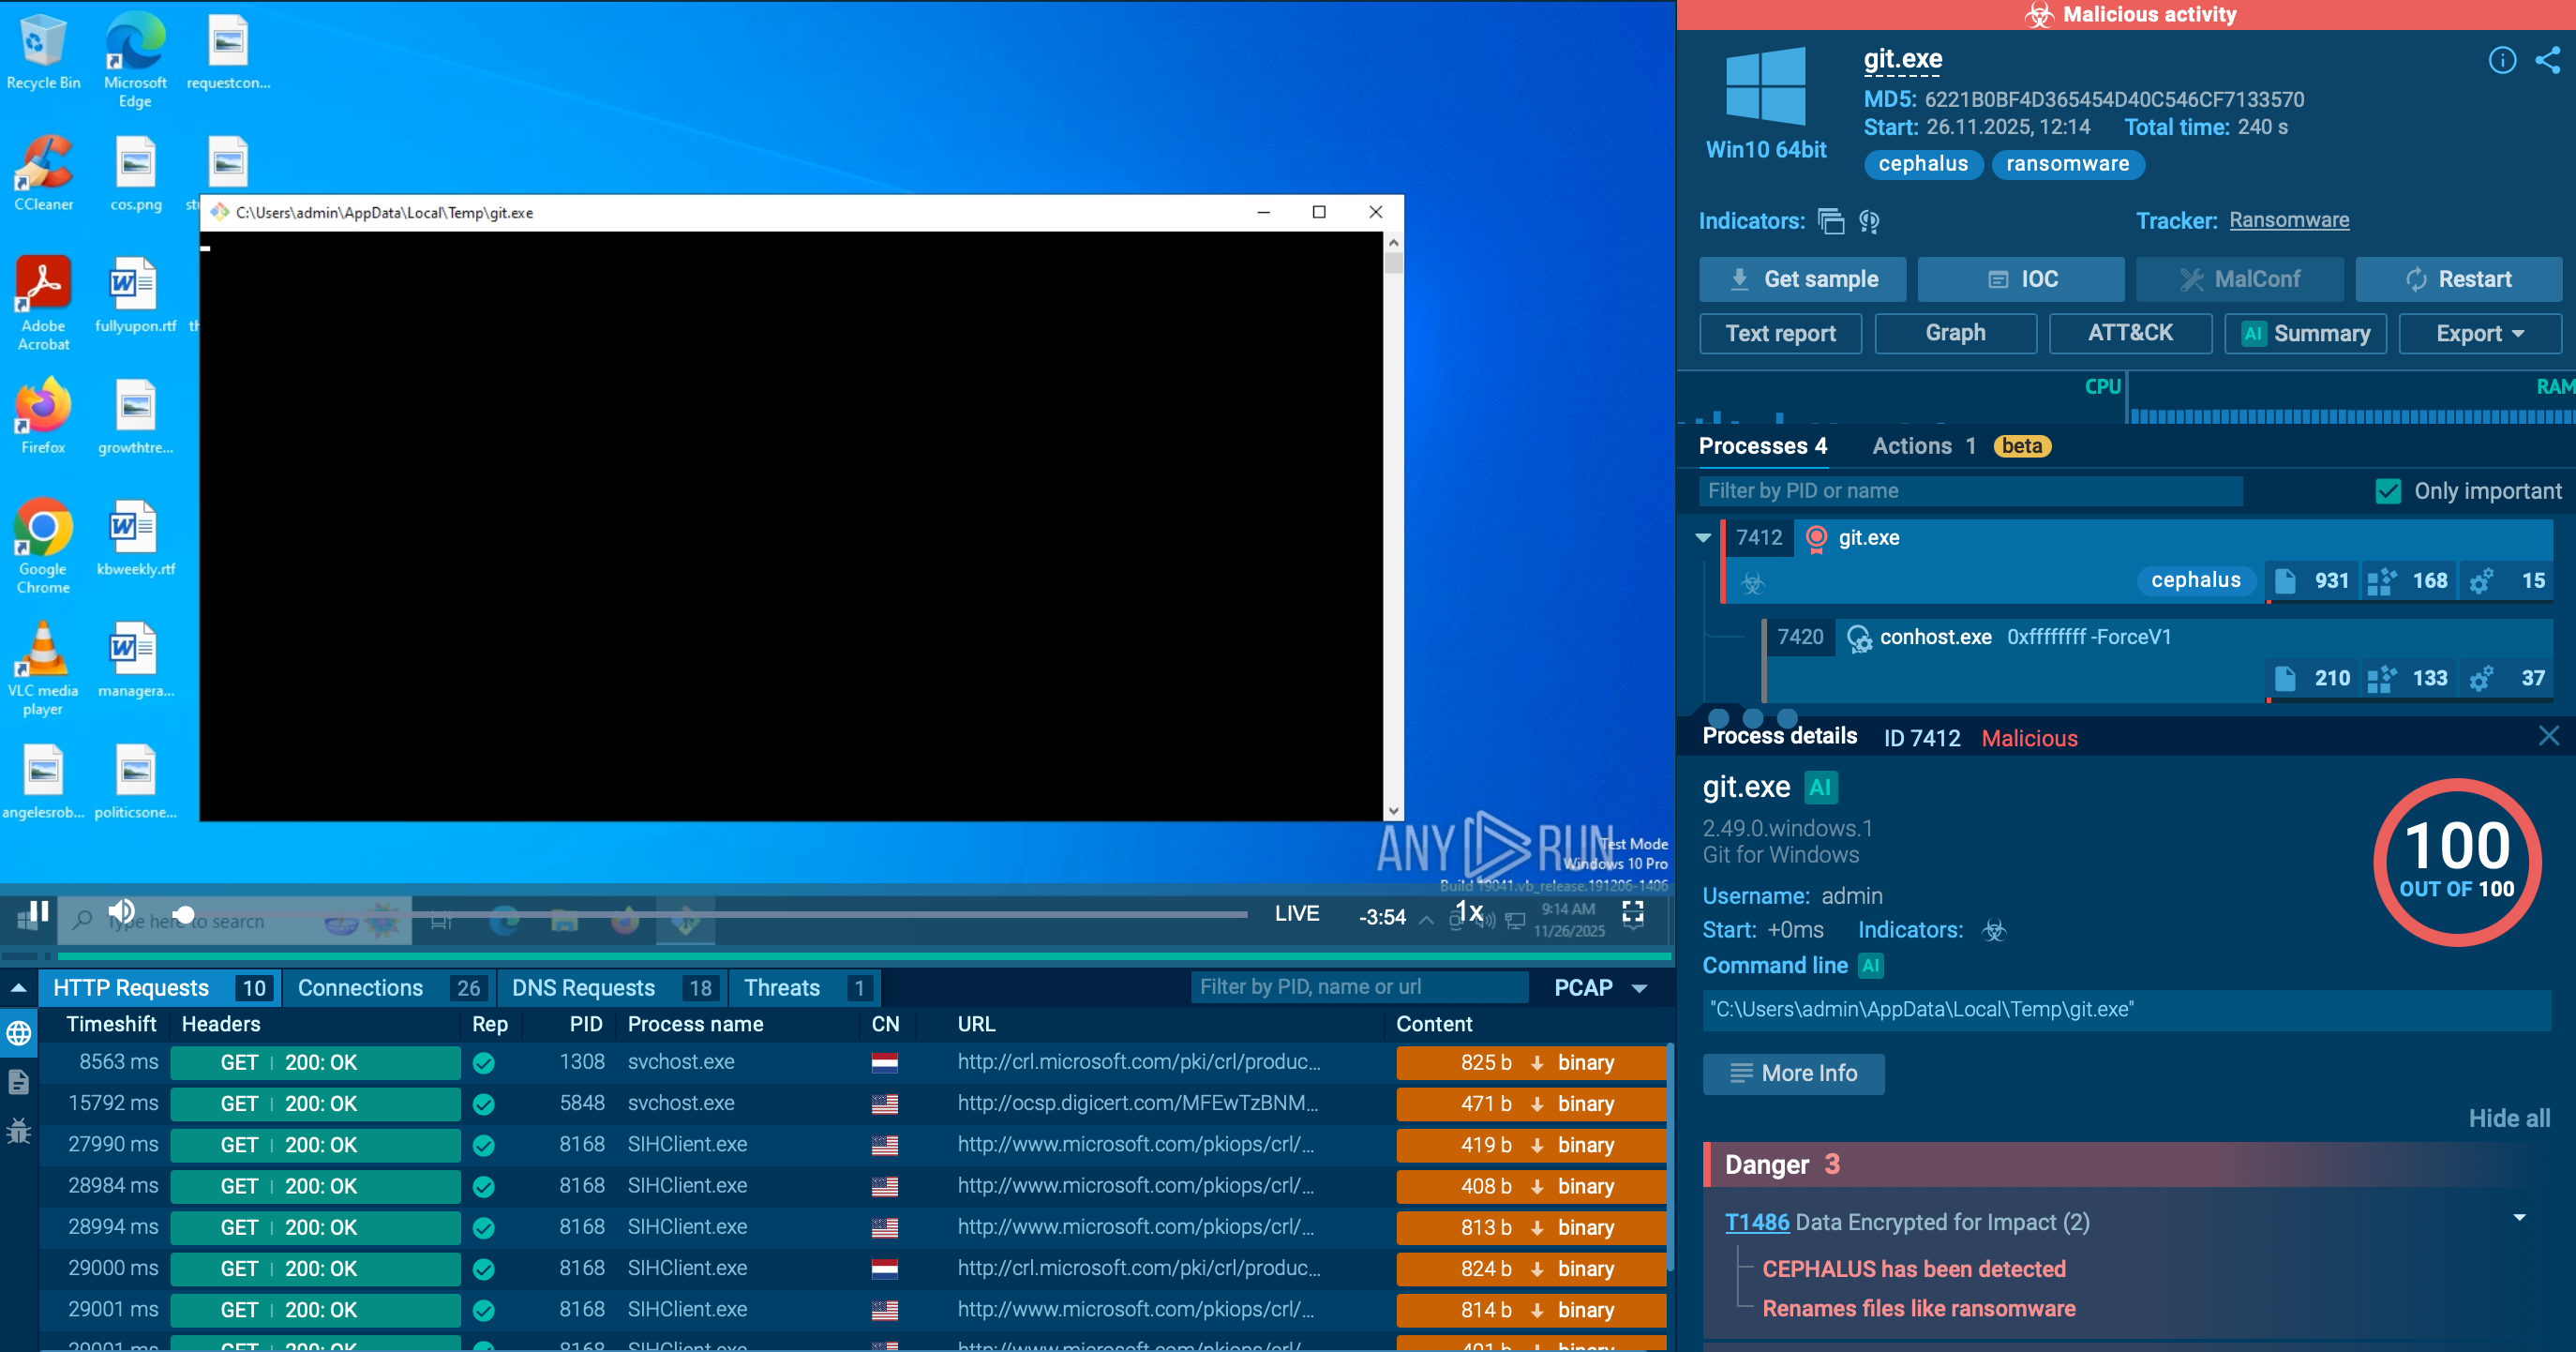
- Security teams can use ANY.RUN’s Interactive Sandbox to expose Cephalus Ransomware for deep insights into its behavior. View analysis of a Cephalus sample.
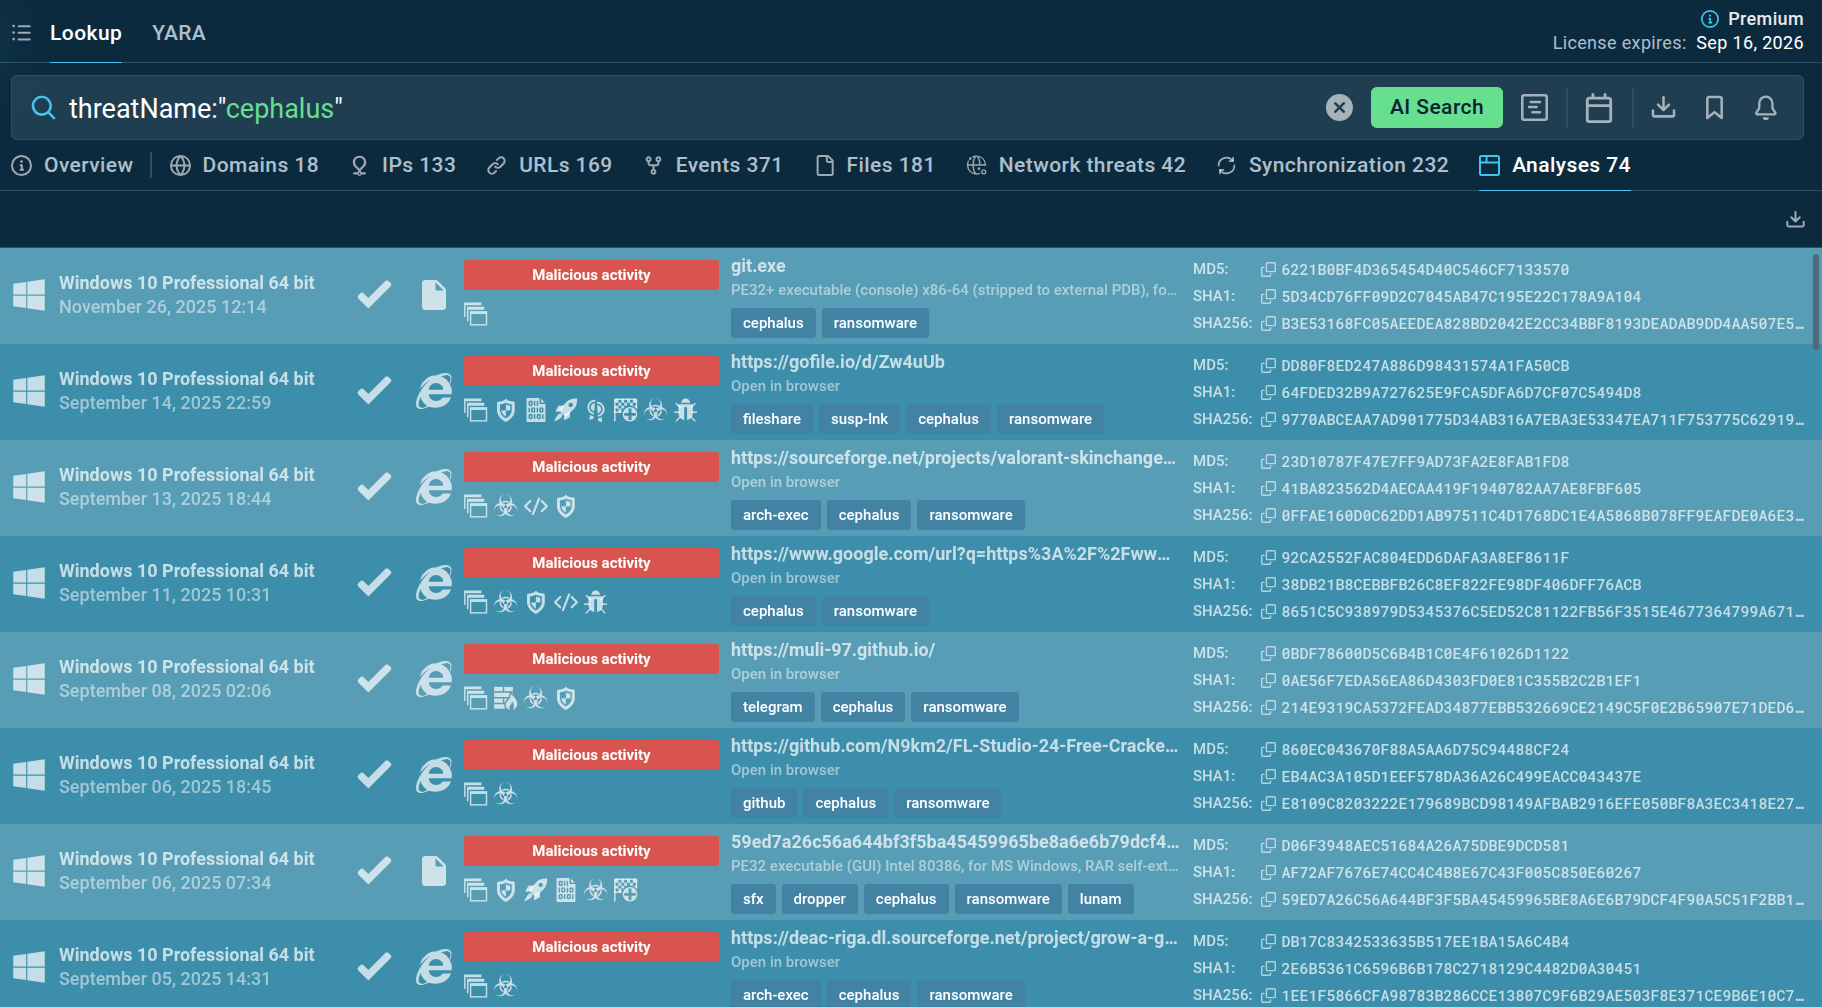
- Explore Cephalus in TI Lookup to identify and monitor its variants.
What Is Cephalus Malware?
Cephalus is a recently observed ransomware threat abusing RDP by stealing credentials, often in systems that lack multi-factor authentication (MFA). That’s how it gains initial access. Once inside, it uses DLL sideloading technique to slip past defenses. As it infiltrates the system, Cephalus encrypts data and prevents its recovery, demonstrating a ransom demand.
The threat's name comes from Greek mythology, referencing a character of the same name with a precise, unerring spear. This suggests an accurate and targeted approach to victims — a fitting analogy, as observed attacks involve tailored malware.
Two notable campaigns took place in August 2025. In both cases, legitimate SentinelOne instances were abused to load a malicious DLL and embed ransomware code.
It’s not entirely known at the moment whether it’s a ransomware-as-a-service or an independent group. Geographic and industrial scopes remain diverse. Among the prevalent targeted sectors are healthcare and finance businesses from the US.
Cephalus Malware Technical Details
The breakdown of how Cephalus typically infiltrates systems:
– Credential theft. Cephalus specifically targets infrastructures where RDP isn’t efficiently protected; this includes the lack of MFA. That’s how threat actors gain initial access.
– Data exfiltration via MEGA cloud storage platform. Before the payload is deployed, threat actors use legitimate RDP accounts to exfiltrate information. Since credentials are legit, this activity doesn’t look suspicious.
– Payload delivery via DLL sideloading. The threat actors abuse legitimate SentinelOne executable, load malicious DLL, and embed malicious code:
- Legitimate SentineOne binary is run from the Downloads folder to execute a malicious DLL (SentinelAgentCore.dll).
- The binary itself is legitimate (SentinelBrowserNativeHost.exe), which reduces the chance of detection.
- The DLL executes data.bin with a ransomware code.
– Evasion and anti-forensics. The ransomware is written in Go (Golang) and uses memory obfuscations.
– Security disabling. Commands like vssadmin destroy shadow copies, registry changes disable Windows Defender, and backup services like Microsoft SQL Server are terminated.
– Exfiltration and encryption. Data is uploaded to MEGA cloud storage and files are encrypted with .sss extension.
– Ransom note. Once the defenses and backup solutions are eliminated, the attackers deploy ransomware by sharing a .txt ransom note in numerous locations.
The note urges the user to begin the negotiation ASAP. In the opposite case, threat actors threaten to leak all data and contact the victim’s clients about their sensitive data being compromised.
Tactics like deletion of shadow copies and registry manipulations to disable security tools make recovery increasingly more complex. The result is stolen data and disrupted operations.
Most notable feature is the unique way to launch the ransomware: through legitimate SentinelOne executable file.
Cephalus Victimology
The scope of victims and their geography is wide. Cephalus targets a number of sectors — IT, healthcare, finance, law firms, etc. What attracts the threat actors is companies that handle sensitive data or intellectual properties, not a particular industry.
Not only large enterprises, but also mid-sized firms are on the list. This might indicate that Cephalus prioritizes smaller companies with weaker security defenses.
Geographically, most attacks are US-based, but there are victims outside the US too.
Cephalus Execution Process
Let's see how Cephalus operates in the ANY.RUN sandbox. Follow this link to see the entire analysis:
View analysis session with Cephalus ransomware
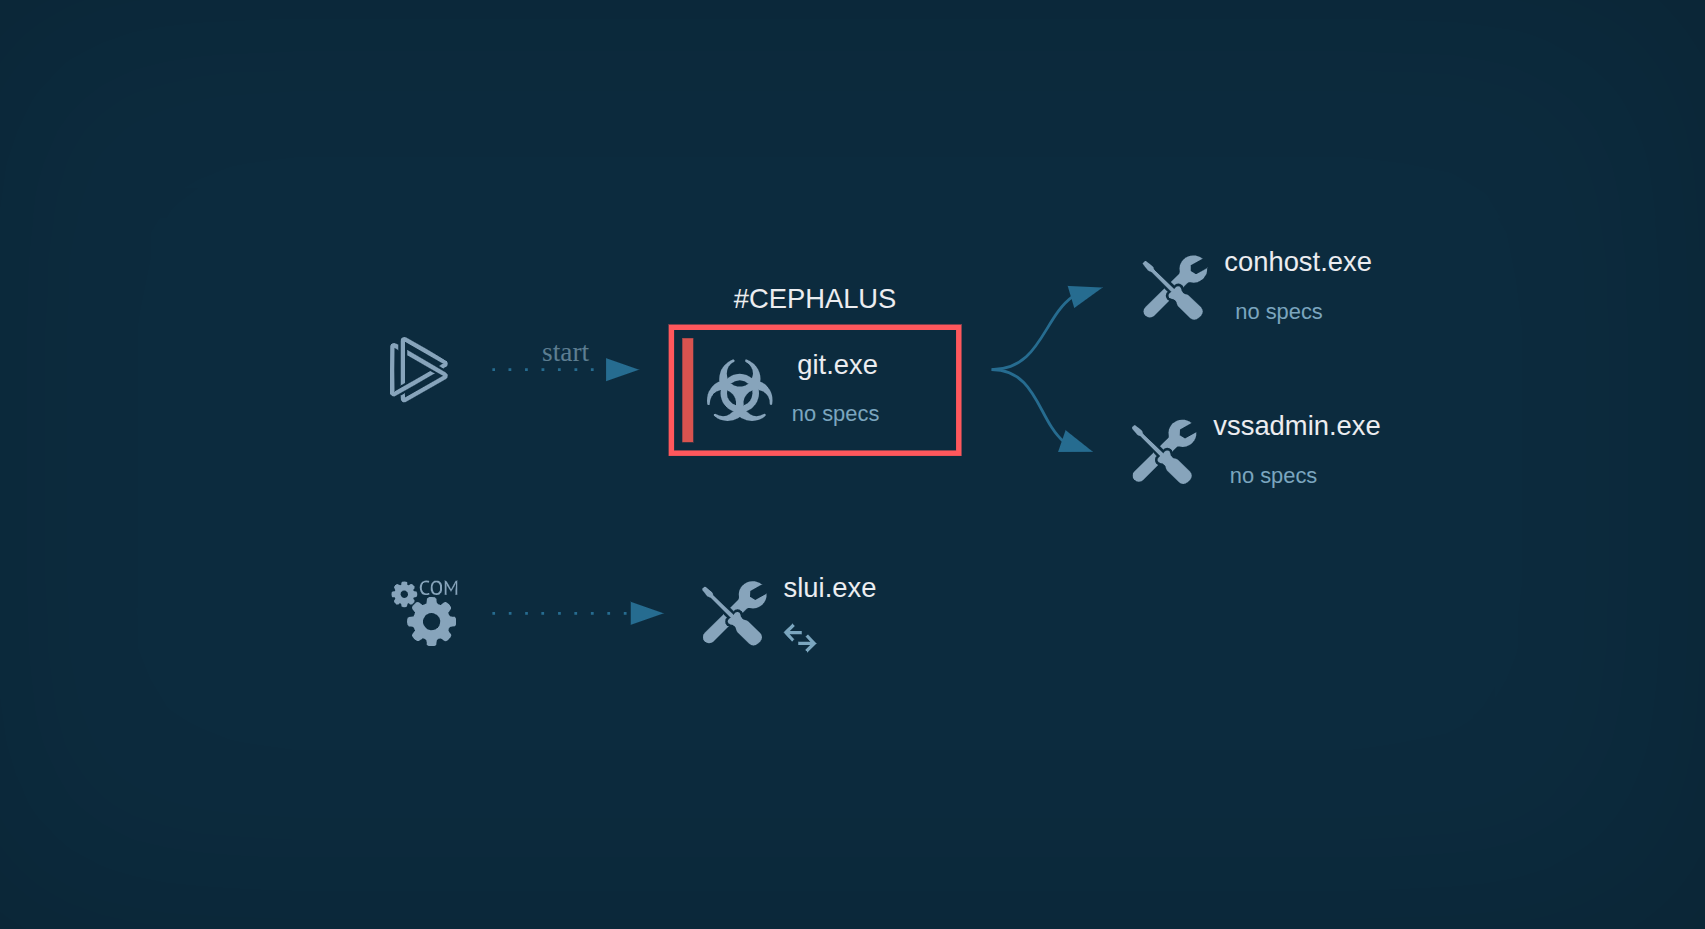
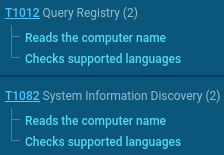
As we can see, upon execution, treat actors collect general info about the victim’s environment. This includes:
– Computer’s name
– Supported languages
– Registry requests
After that, it begins to encrypt user’s files and does so topically. Such an approach accelerates the process as compared to recursive launch across all user catalogs.
The victim is then shown a ransom note in their infiltrated system. You can see its fragment below:
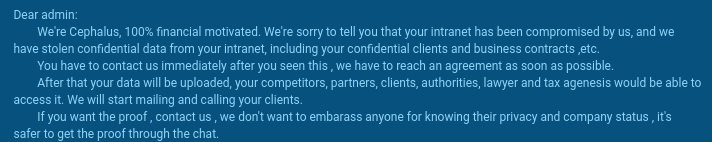
The note highlights the urgency of the incident and offers proof of data stealth. It says that confidential data will be leaked, and the victim’s clients will be contacted via calls or emails to inform them about their data being stolen. All this motivates the victim to start the negotiation urgently.
Cephalus also deletes shadow copies using the vssadmin command. This prevents the recovery of the system through VSS. As a result, the chances that the victim will be able to recover data on their own are minimized, once again highlighting the complexity of the situation.
Cephalus Malware Distribution Methods
According to research, Cephalus seems to be mostly distributed through stolen and compromised RDP credentials. They hit infrastructures with exposed RDP, for example, in cases where there is no multi-factor authentication (MFA).
Gathering Threat Intelligence on Cephalus Malware
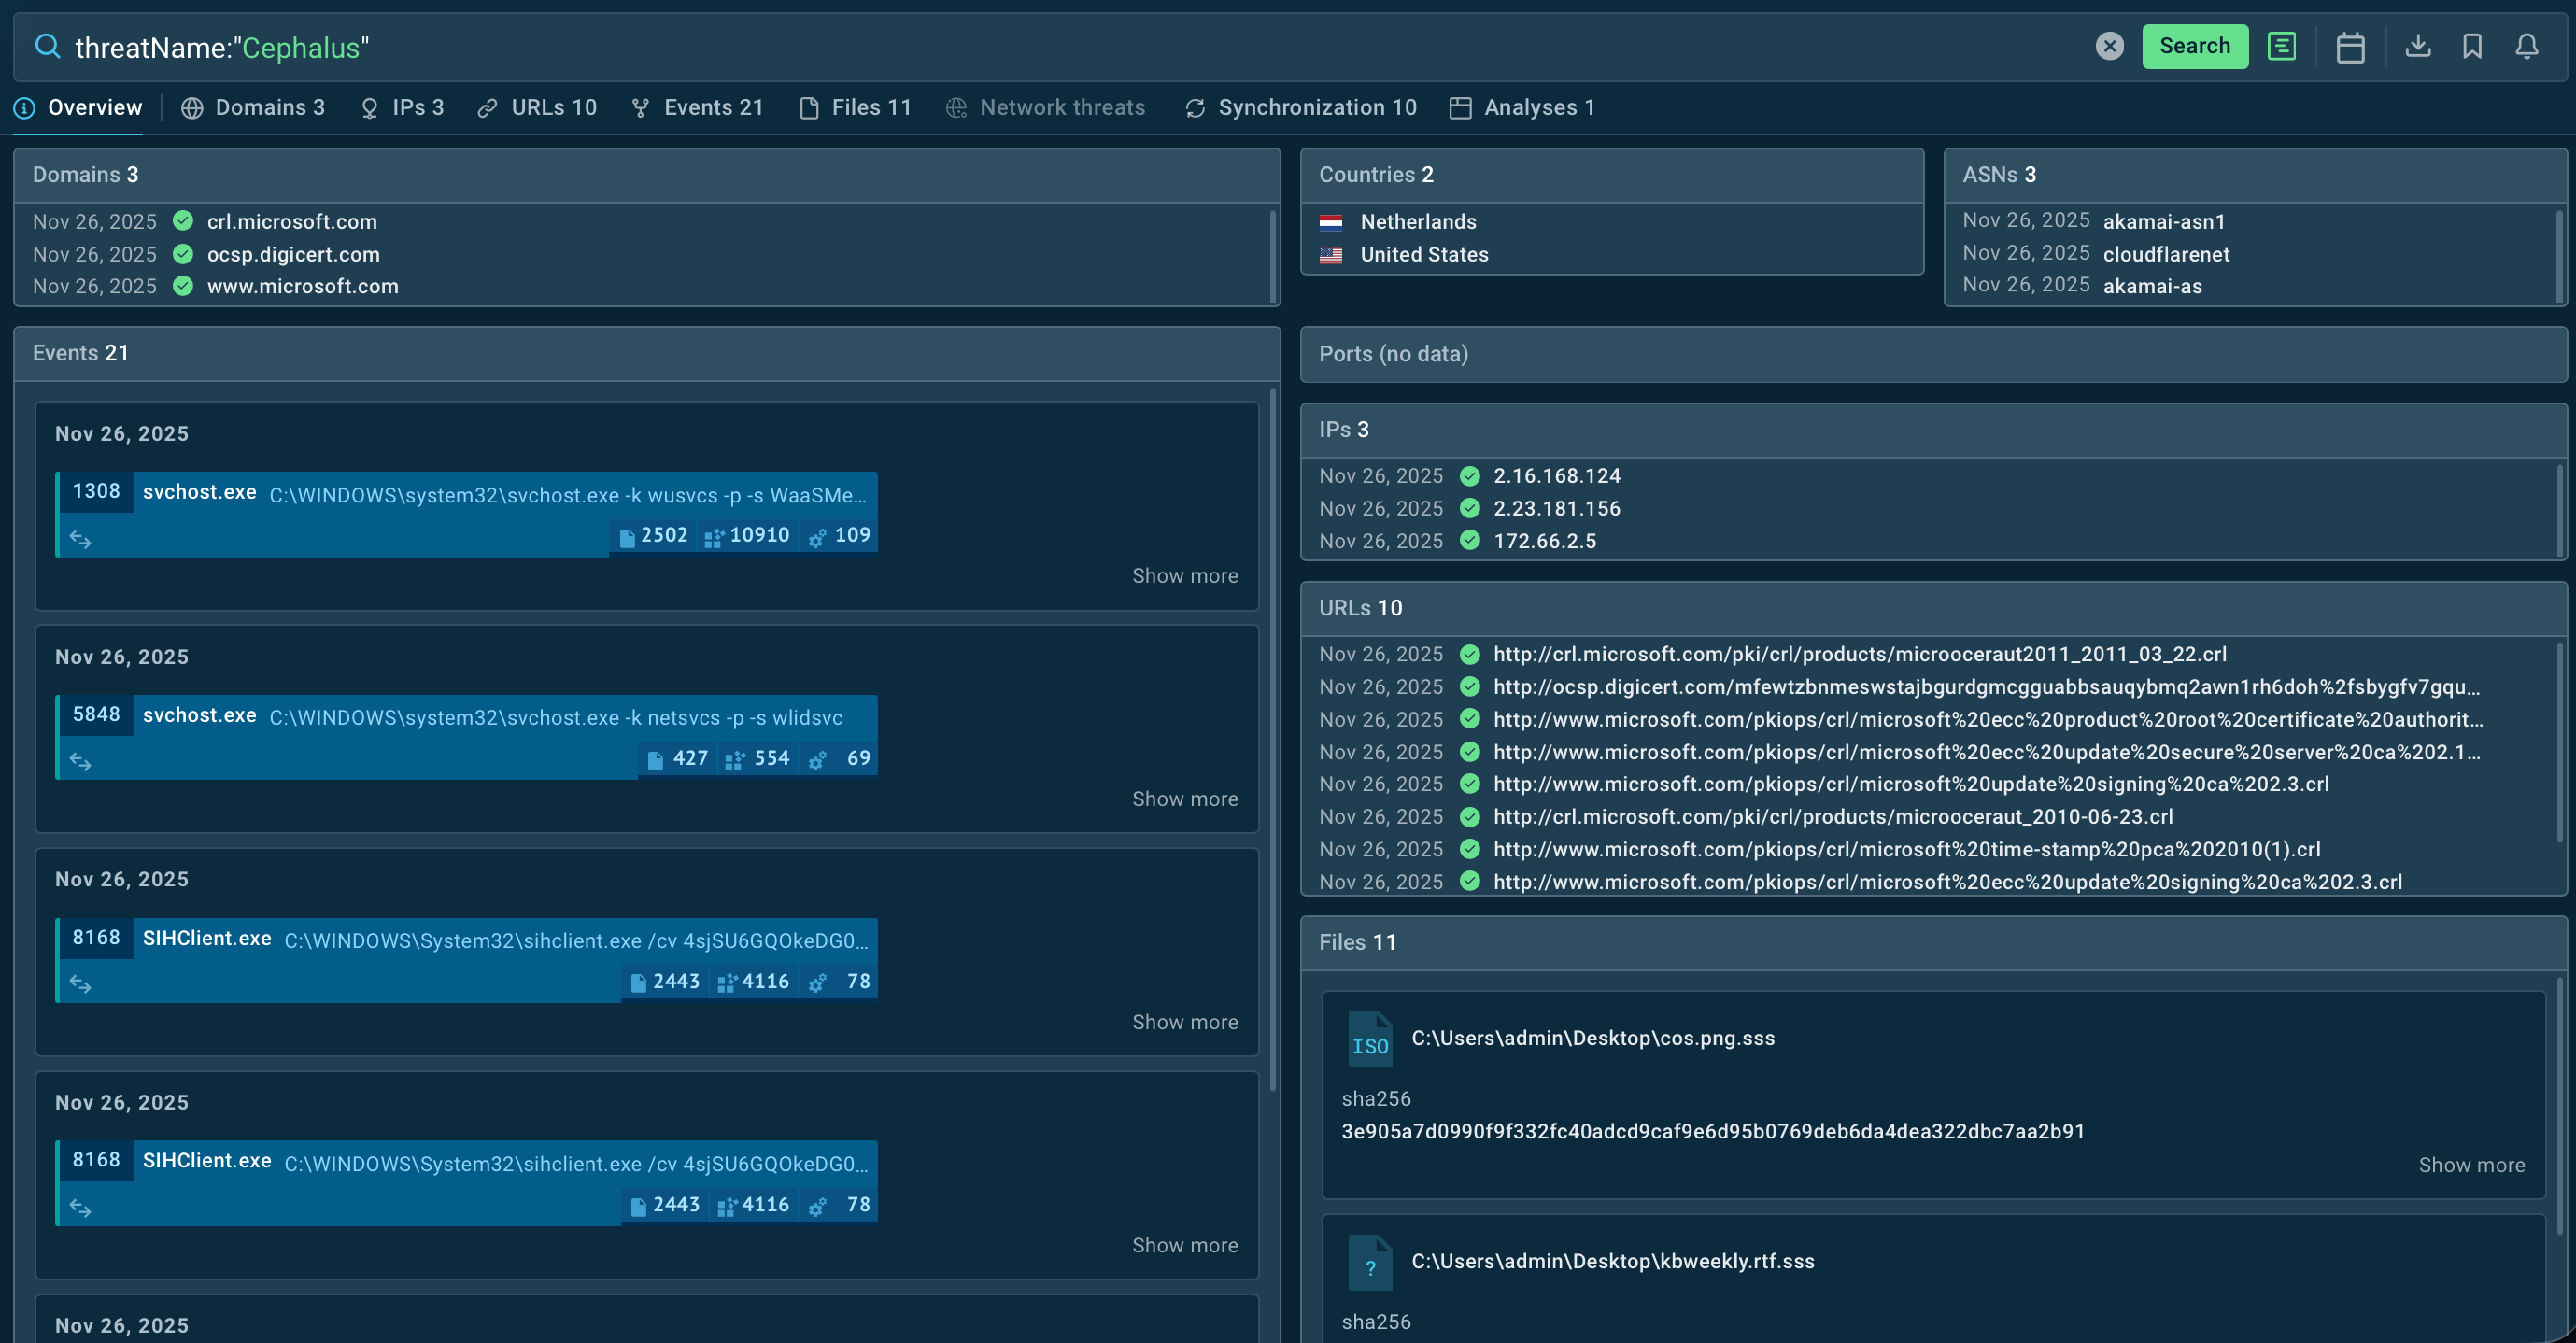
Threat Intelligence Lookup enables security teams to quickly search for information about suspicious files, URLs, domains, and IP addresses potentially associated with Cephalus.
By querying file hashes or URLs encountered in environments, analysts can immediately determine if they match known Cephalus samples, view detailed behavioral analysis, and understand the specific capabilities and infrastructure of particular variants.
This rapid intelligence access accelerates incident response and enables proactive blocking of threats before they impact systems.
Start exploring any threat by looking it up by the name, for instance:
Conclusion
Cephalus is a high-impact ransomware threat that abuses legitimate executables to bypass defenses. It terminates backups and copies, making recovery extremely different. The malware targets organizations with sensitive data and weak defenses.
To avoid compromise and start monitoring Cephalus, its new strains, and other threats, apply a proactive approach to security. Analyze suspicious files in sandboxing services like ANY.RUN’s Interactive Sandbox
To track emerging threats and enrich your indicators, try Threat Intelligence Lookup, a browsable collection of IOCs and IOBs gathered from live investigations done by 15,000+ SOC teams.
Sign up to start gathering actionable intel in TI Lookup. Get 50 trial requests
Other malware & phishing threats
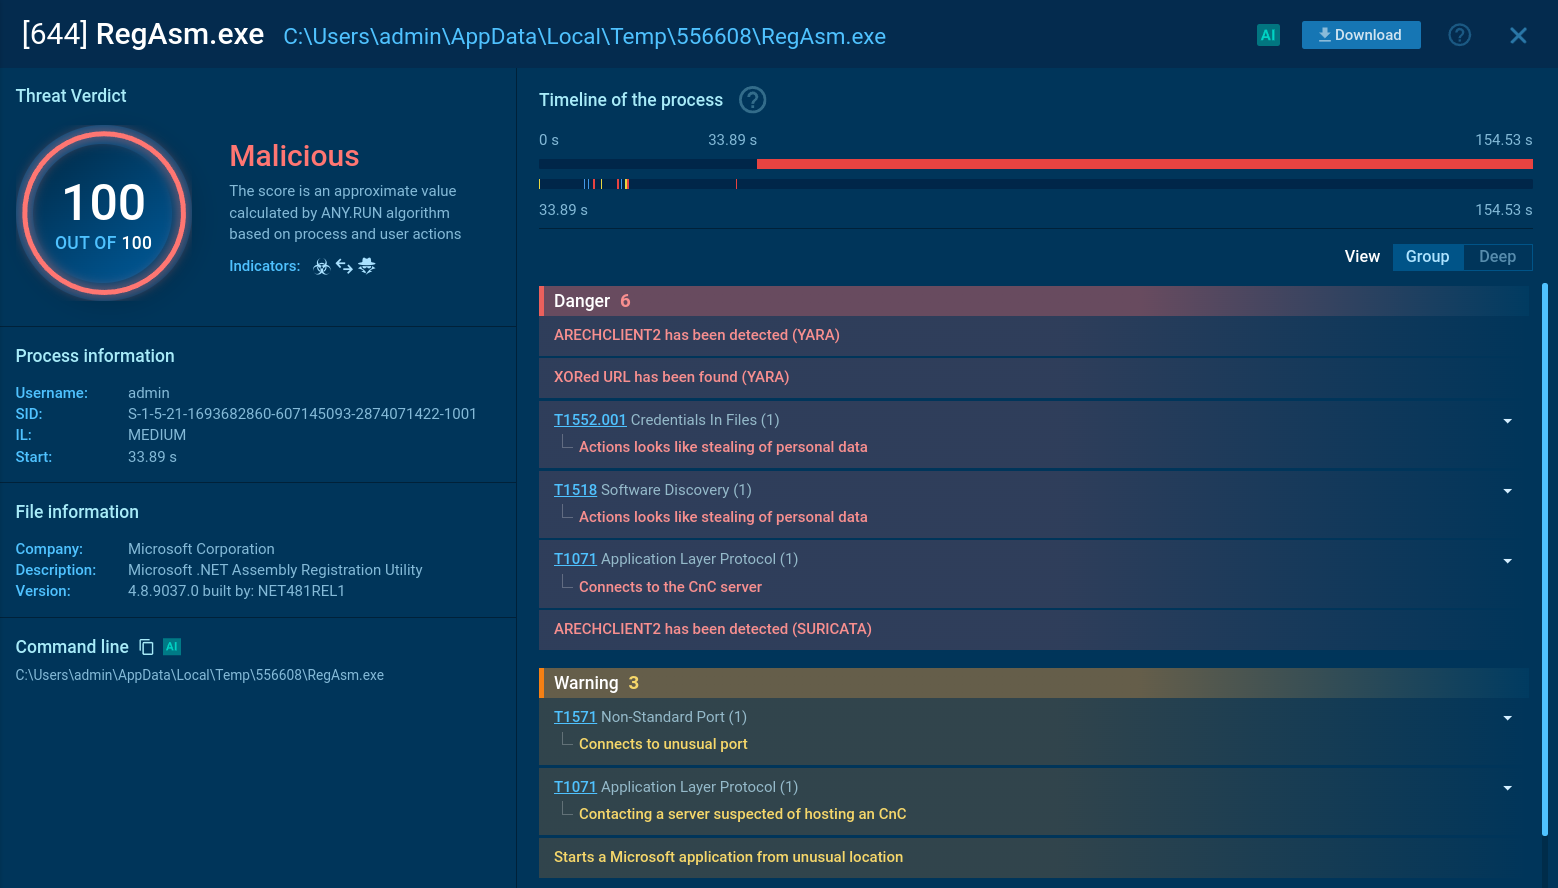 Arechclient2The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
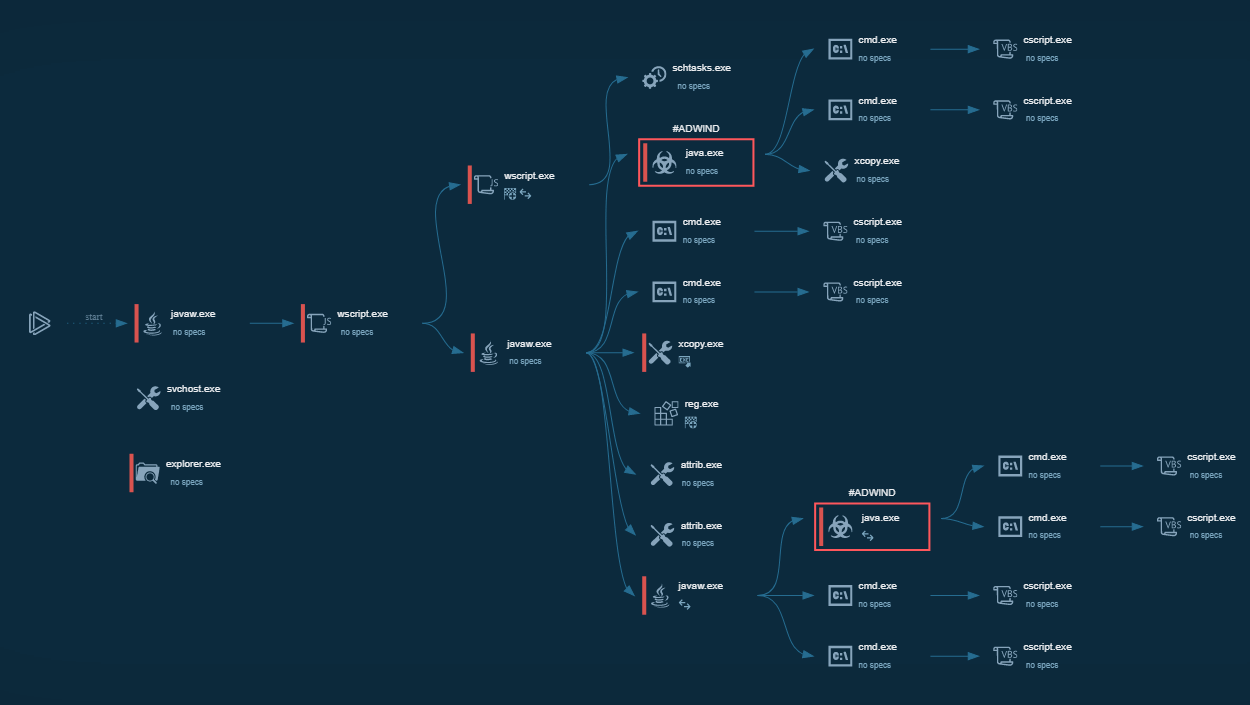 AdwindAdwind RAT, sometimes also called Unrecom, Sockrat, Frutas, jRat, and JSocket, is a Malware As A Service Remote Access Trojan that attackers can use to collect information from infected machines. It was one of the most popular RATs in the market in 2015.
 Akira RansomwareAkira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
 SVCStealerSVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
 Bluesky RansomwareBlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
 Ficker StealerFicker Stealer is a malware that steals passwords, files, credit card details, and other types of sensitive information on Windows systems. It is most often distributed via phishing emails and can perform keylogging, process injection, and browser tracking.