CSuite
- 44
- Global rank
- 19
- Month rank
- 25
- Week rank
CSuite is a financially motivated phishing and remote-access operation that uses counterfeit business document pages, credential-harvesting infrastructure, and legitimate remote-management tools to compromise organizational identities and devices.
- Phishingkit
- Type
- Unknown
- Origin
- 1 February, 2026
- First seen
- 19 October, 2026
- Last seen
How to analyze CSuite with ANY.RUN
IOCs
IP addresses
- 74.178.240.61
- 48.209.138.168
- 104.18.38.233
- 142.251.110.132
- 23.52.181.141
- 150.171.28.11
- 150.171.27.11
- 150.171.109.99
- 40.126.32.134
- 141.193.213.20
- 128.24.231.64
- 64.247.179.143
- 23.11.40.157
- 172.67.68.67
- 142.251.14.106
- 65.9.130.99
- 142.251.154.119
- 35.190.80.1
- 104.18.22.222
- 150.171.109.101
Hashes
- 7523c62abdb7628c5a9dad8f97d8d8c5c040ede36535e531a8a3748b6cae7e00
- 2921a11f25dadaa24aa79a548e4e81508c2e5e56af2d833d65e2bcce448ce2f5
- c3594eaa7b5e4e27aa020d94a29f4696ec5a0d816eca8ffe515f4f262dfaff4e
- 2e2afc1921504b5ea756d3f67f96716567c040985b20a65e4509f212f4325366
- ff1c1d21a4451d83dbee8a946fcc92ecb7b13fe41db33a9ada21b808b29870c8
- 72b57748e2fe326a4dd7387a3afb89c5e7856a0a5de15c7c70c3e0cf4f6deca0
- 31641e81a596de050fb5892f54bcc64235744c761618b91ded409b2f4eabb4b5
- 0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
- 9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
- 2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
- 64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
- 7852fce59c67ddf1d6b8b997eaa1adfac004a9f3a91c37295de9223674011fba
- 2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
- ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
- af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
- 728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
- 22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
- cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
- 14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
- 7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
Domains
- finestmauirentals.com
- uk.kindlewoodco.com
- microsoft.ai
- www.bing.com
- a.nel.cloudflare.com
- t3.gstatic.com
- msedge.b.tlu.dl.delivery.mp.microsoft.com
- slscr.update.microsoft.com
- nexusrules.officeapps.live.com
- fe3cr.delivery.mp.microsoft.com
- t2.gstatic.com
- update.googleapis.com
- www.softwareworld.co
- api.edgeoffer.microsoft.com
- edge.microsoft.com
- edge-cloud-resource-static.azureedge.net
- activation-v2.sls.microsoft.com
- copilot.microsoft.com
- crl.microsoft.com
- settings-win.data.microsoft.com
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:vr0jgoitasg2lgmmdwn_1g61mis0dsrxqcjvruuf8o4&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://copilot.microsoft.com/c/api/user/eligibility
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://aefd.nelreports.net/api/report?cat=bingserp
- https://uk.kindlewoodco.com/adobe_installer.html
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1792448370&lafgdate=0
- https://www.softwareworld.co/assets/software/logo/adobe-acrobat-reader.jpg
- https://www.google.com/s2/favicons?domain=adobe.com&sz=32
- https://www.google.com/s2/favicons?domain=google.com&sz=32
- https://www.google.com/s2/favicons?domain=microsoft.com&sz=32
- https://www.google.com/s2/favicons?domain=firefox.com&sz=32
Last seen at
Key Takeaways
- Multi-Stage Phishing Operation: CSuite uses convincing business-themed lures involving services such as Adobe, DocuSign, Zoom, Dropbox, and Microsoft 365 to initiate attacks against organizational users.
- Dual Compromise Paths: The operation can target both user identities and employee endpoints, combining credential and session theft with the deployment of legitimate remote-management software.
- Microsoft 365 Account Theft: Stolen credentials and active authentication sessions can give attackers access to corporate mailboxes and other business resources.
- Abuse of Legitimate Tools: Remote-management and endpoint-management products, including ScreenConnect, Action1, Atera, Syncro, and PDQ Connect, can be misused to establish unauthorized remote access.
- Business Fraud Risk: Compromised mailboxes may enable invoice manipulation, payment redirection, impersonation, and additional phishing attempts.
- Geographic Reach: Reporting on CSuite activity has identified organizations in the United States and Europe, alongside activity in other countries.
- Detection Opportunities: Suspicious document-sharing invitations, counterfeit login pages, unusual authentication events, unexpected remote-management installations, and unexplained outbound connections can provide useful investigation leads.
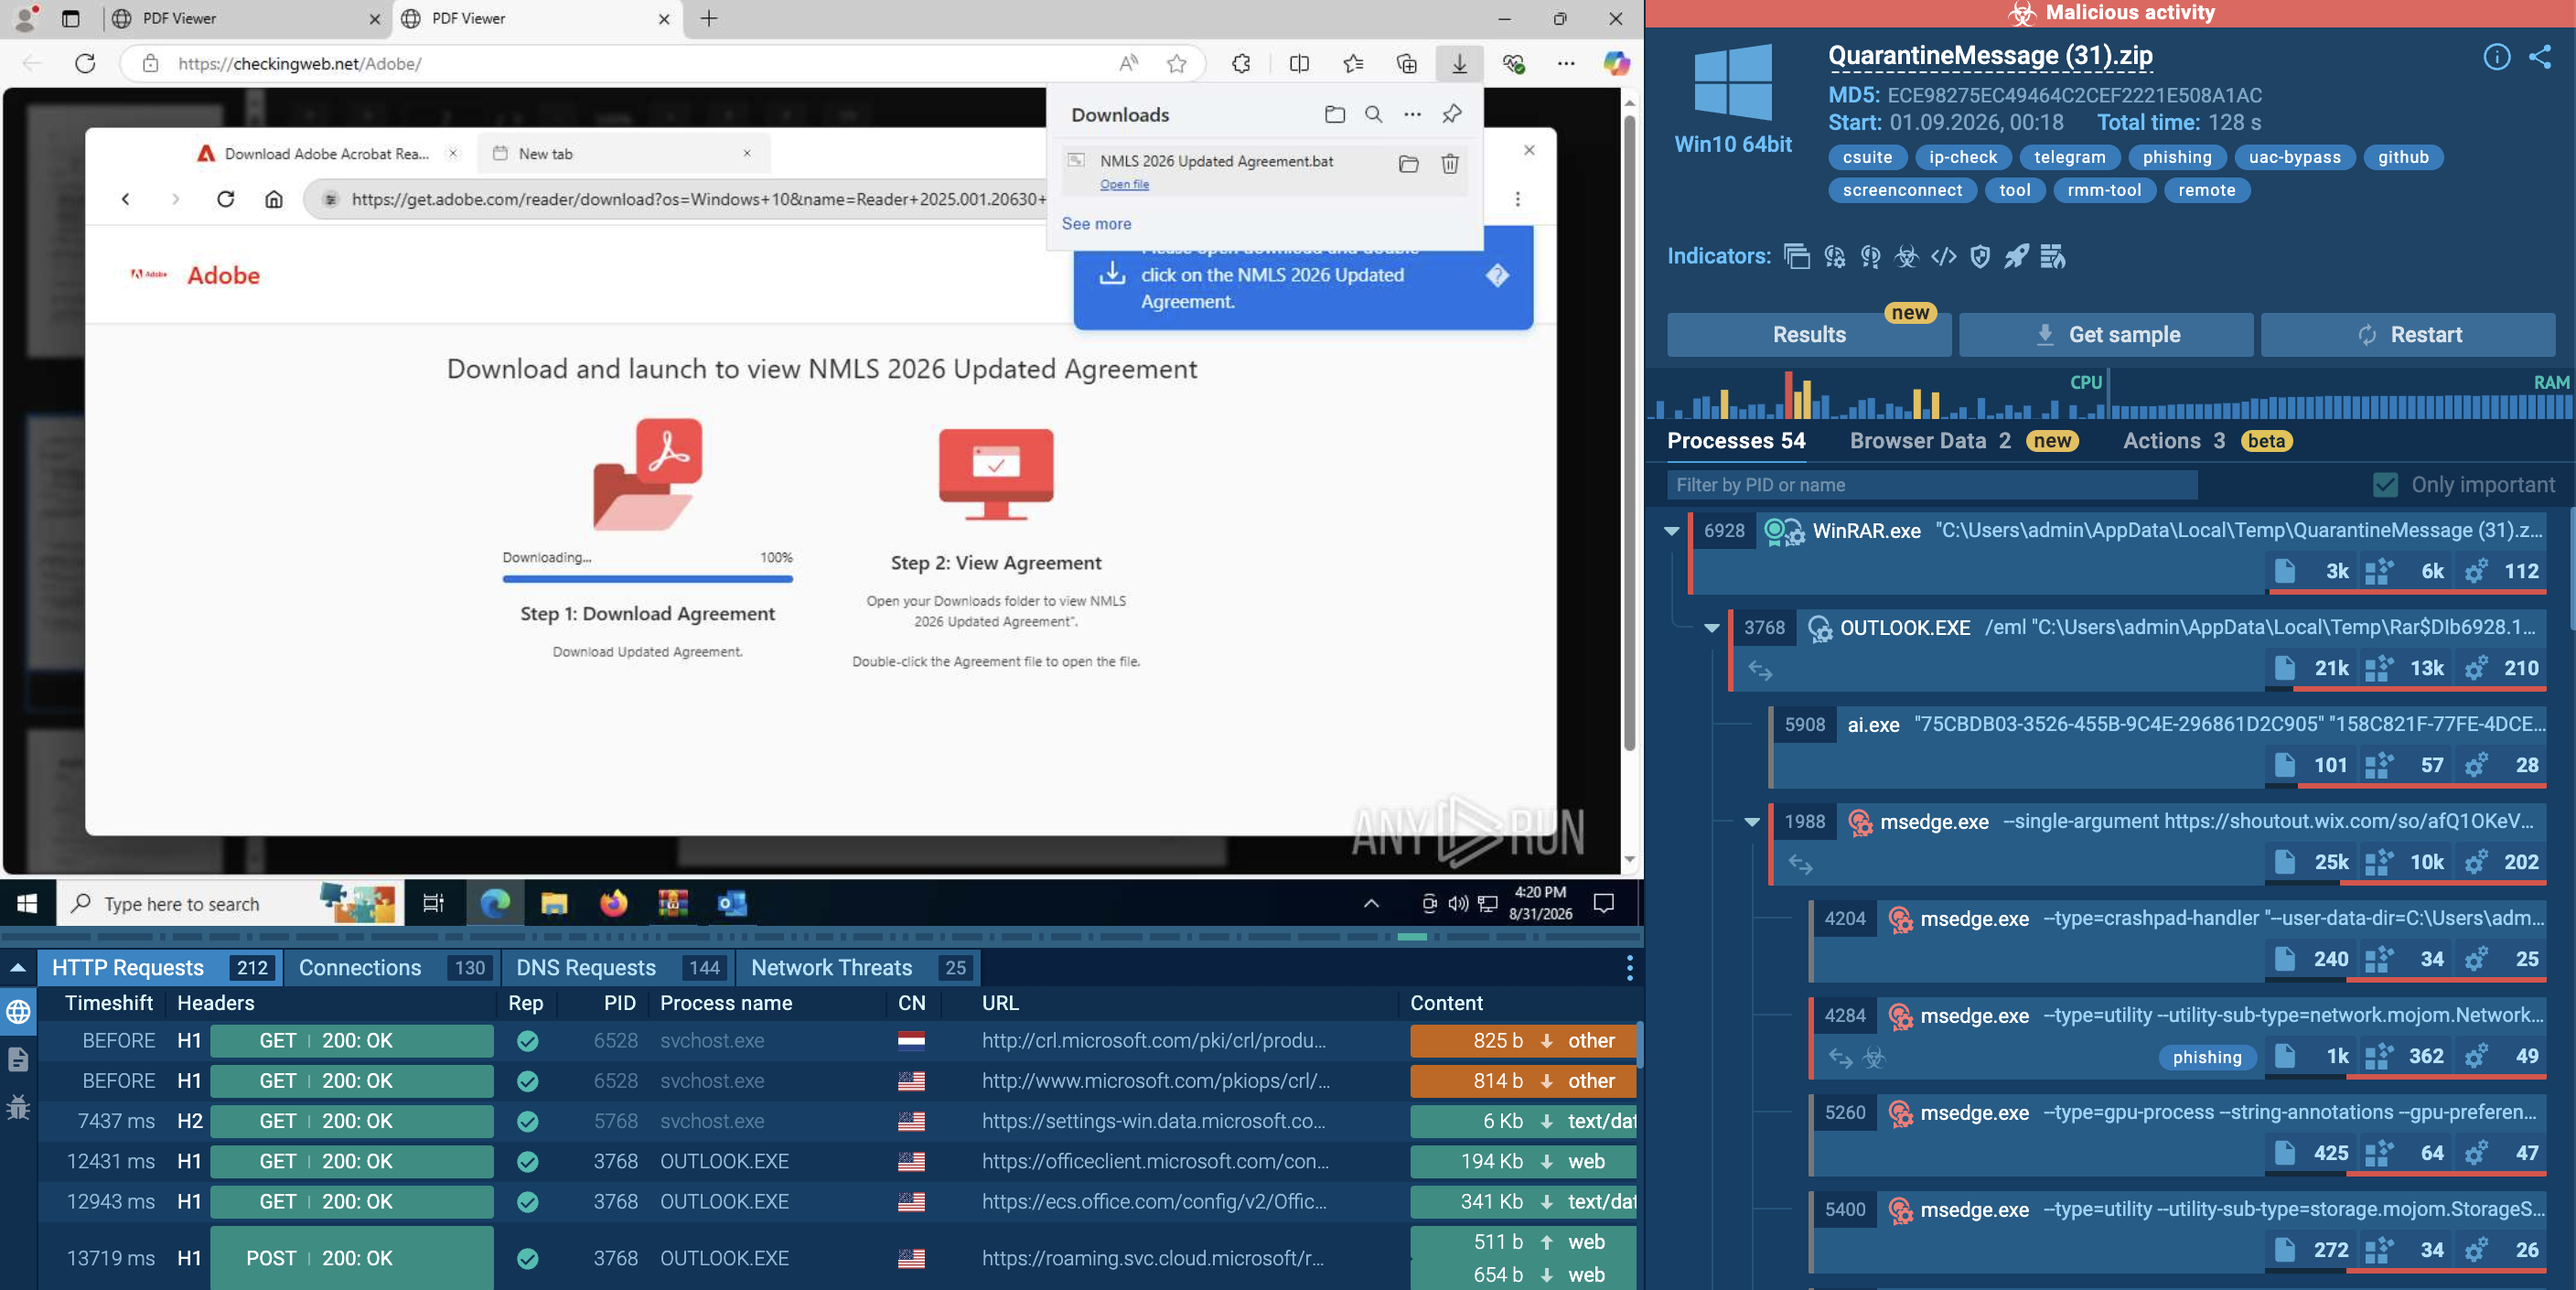
- ANY.RUN’s Interactive Sandbox analysis helps investigate CSuite’s attack behavior, including phishing redirects, credential and session theft, suspicious script execution, and the deployment of remote-management tools used to compromise organizational accounts and endpoints.
What is CSuite?
CSuite is a phishing and remote-access operation associated with a management panel known as CSuite v1.1. Its activity combines techniques for stealing account credentials and authentication sessions with methods for gaining control of organizational endpoints.
Rather than relying on a single malware family, CSuite can use several components throughout an intrusion. These include counterfeit document-viewing pages, credential-harvesting infrastructure, lightweight scripts, installers, and legitimate remote-management applications.
The operation's approach creates two complementary opportunities for attackers. One is to compromise a user's identity and gain access to business accounts. The other is to install software that provides remote access to an employee's device.
These capabilities can expose organizations to both account-level and endpoint-level compromise. A successful phishing attempt may therefore lead to more than stolen credentials: it can also create a persistent foothold on a workstation or enable further abuse of trusted business communications.
CSuite activity has been associated with financially motivated objectives, particularly credential theft and business email compromise. Its use of familiar services and legitimate software can also make malicious activity harder to distinguish from ordinary business operations.
How CSuite Can Affect Businesses and Organizations
A CSuite-related incident can create several types of risk:
- Corporate account compromise: Stolen credentials or active authentication sessions can expose Microsoft 365 accounts, email conversations, and business information.
- Unauthorized endpoint access: Abused remote-management software can provide attackers with continuing access to compromised devices.
- Business email compromise: Access to genuine correspondence can help attackers impersonate employees, manipulate invoices, or redirect payments.
- Internal phishing and impersonation: A compromised mailbox may be used to send convincing messages to colleagues, customers, or business partners.
- Persistence and recovery challenges: Organizations may need to remove unauthorized management agents, revoke compromised sessions, and verify that access has been fully terminated.
- Operational disruption: Investigating identity and endpoint compromise simultaneously can increase incident-response workloads and recovery costs.
- Broader security exposure: Access to both accounts and devices can expand the potential scope of an incident across connected business workflows.
The overall impact depends on which attack path succeeds, the privileges associated with the compromised account or device, and the actions performed after access is established.
Victimology: Which Organizations May Be at Risk?
CSuite activity has been associated with organizations across several sectors, including:
- Technology companies
- Manufacturing businesses
- Government and public administration
- Consulting firms
- Educational institutions
- Mortgage-related businesses
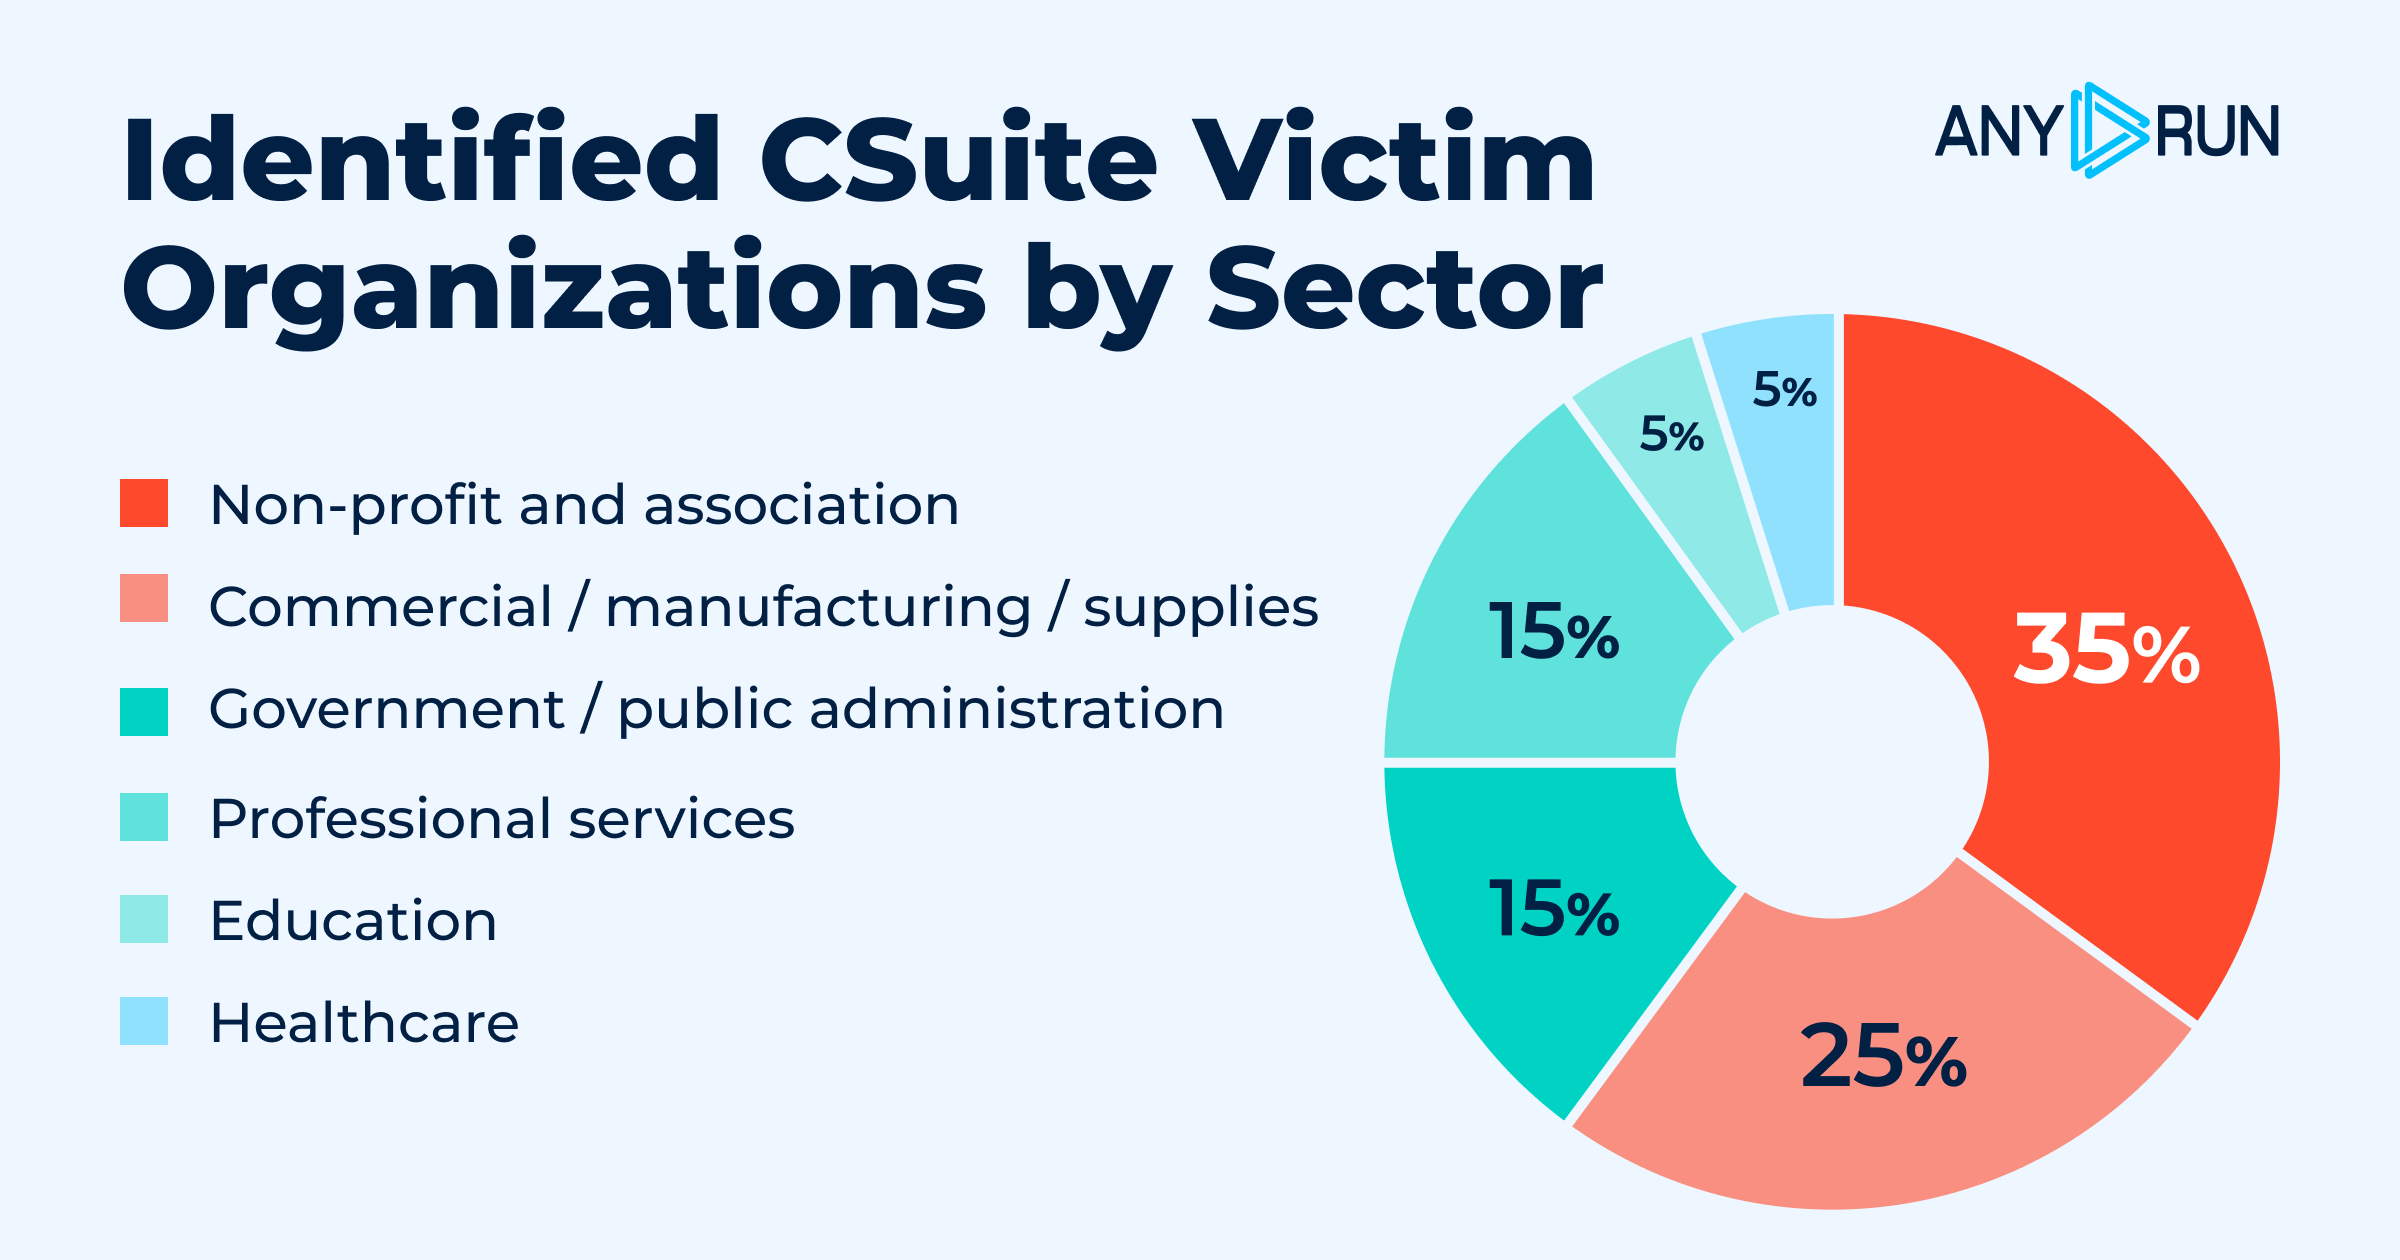
Organizations that depend heavily on Microsoft 365, digital document workflows, and remote administration may face particular exposure because these services are integral to their daily operations.
The operation is not limited to a single geographic region. Reporting has identified a strong US focus, with additional activity affecting organizations and users in Europe and other parts of the world.
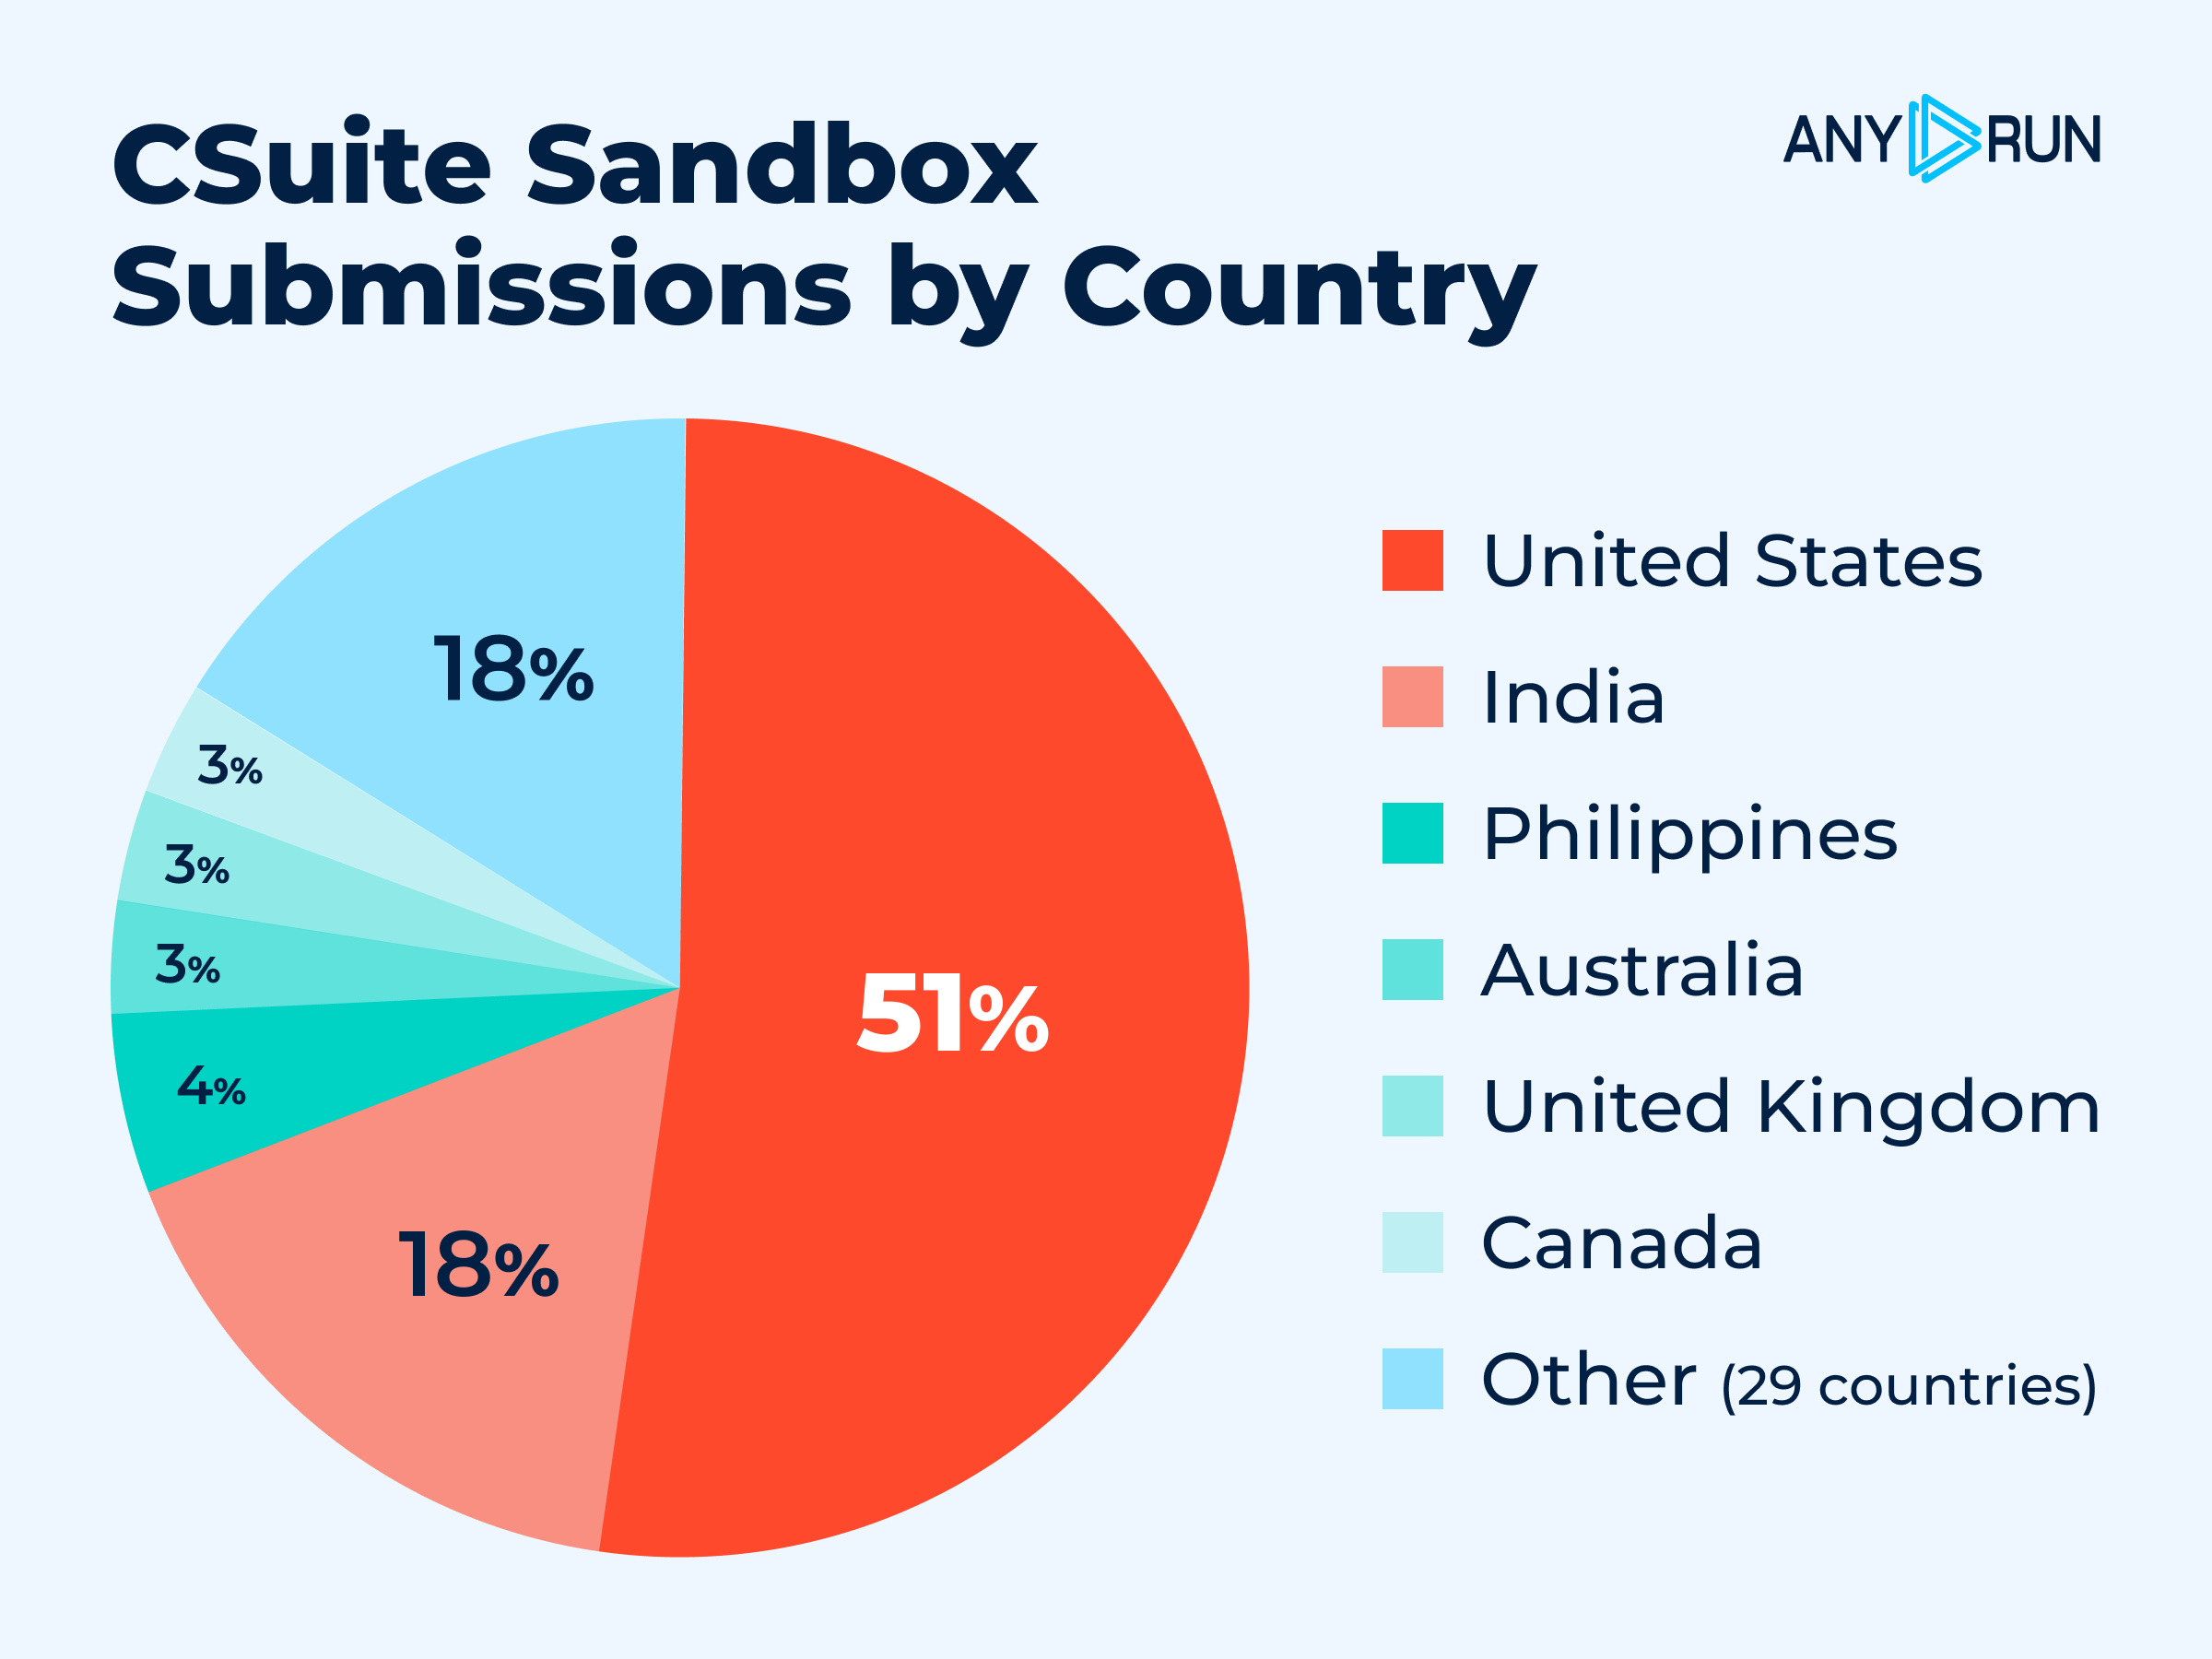
However, the presence of a particular industry or country in observed activity does not mean that organizations elsewhere are immune. Exposure depends on factors such as phishing susceptibility, identity security controls, endpoint monitoring, and the management of remote-access software.
How Does CSuite Function?
Observing a CSuite sample inside ANY.RUN’s Interactive Sandbox shows that CSuite operates through a multi-stage attack process that can branch into endpoint compromise or identity theft.
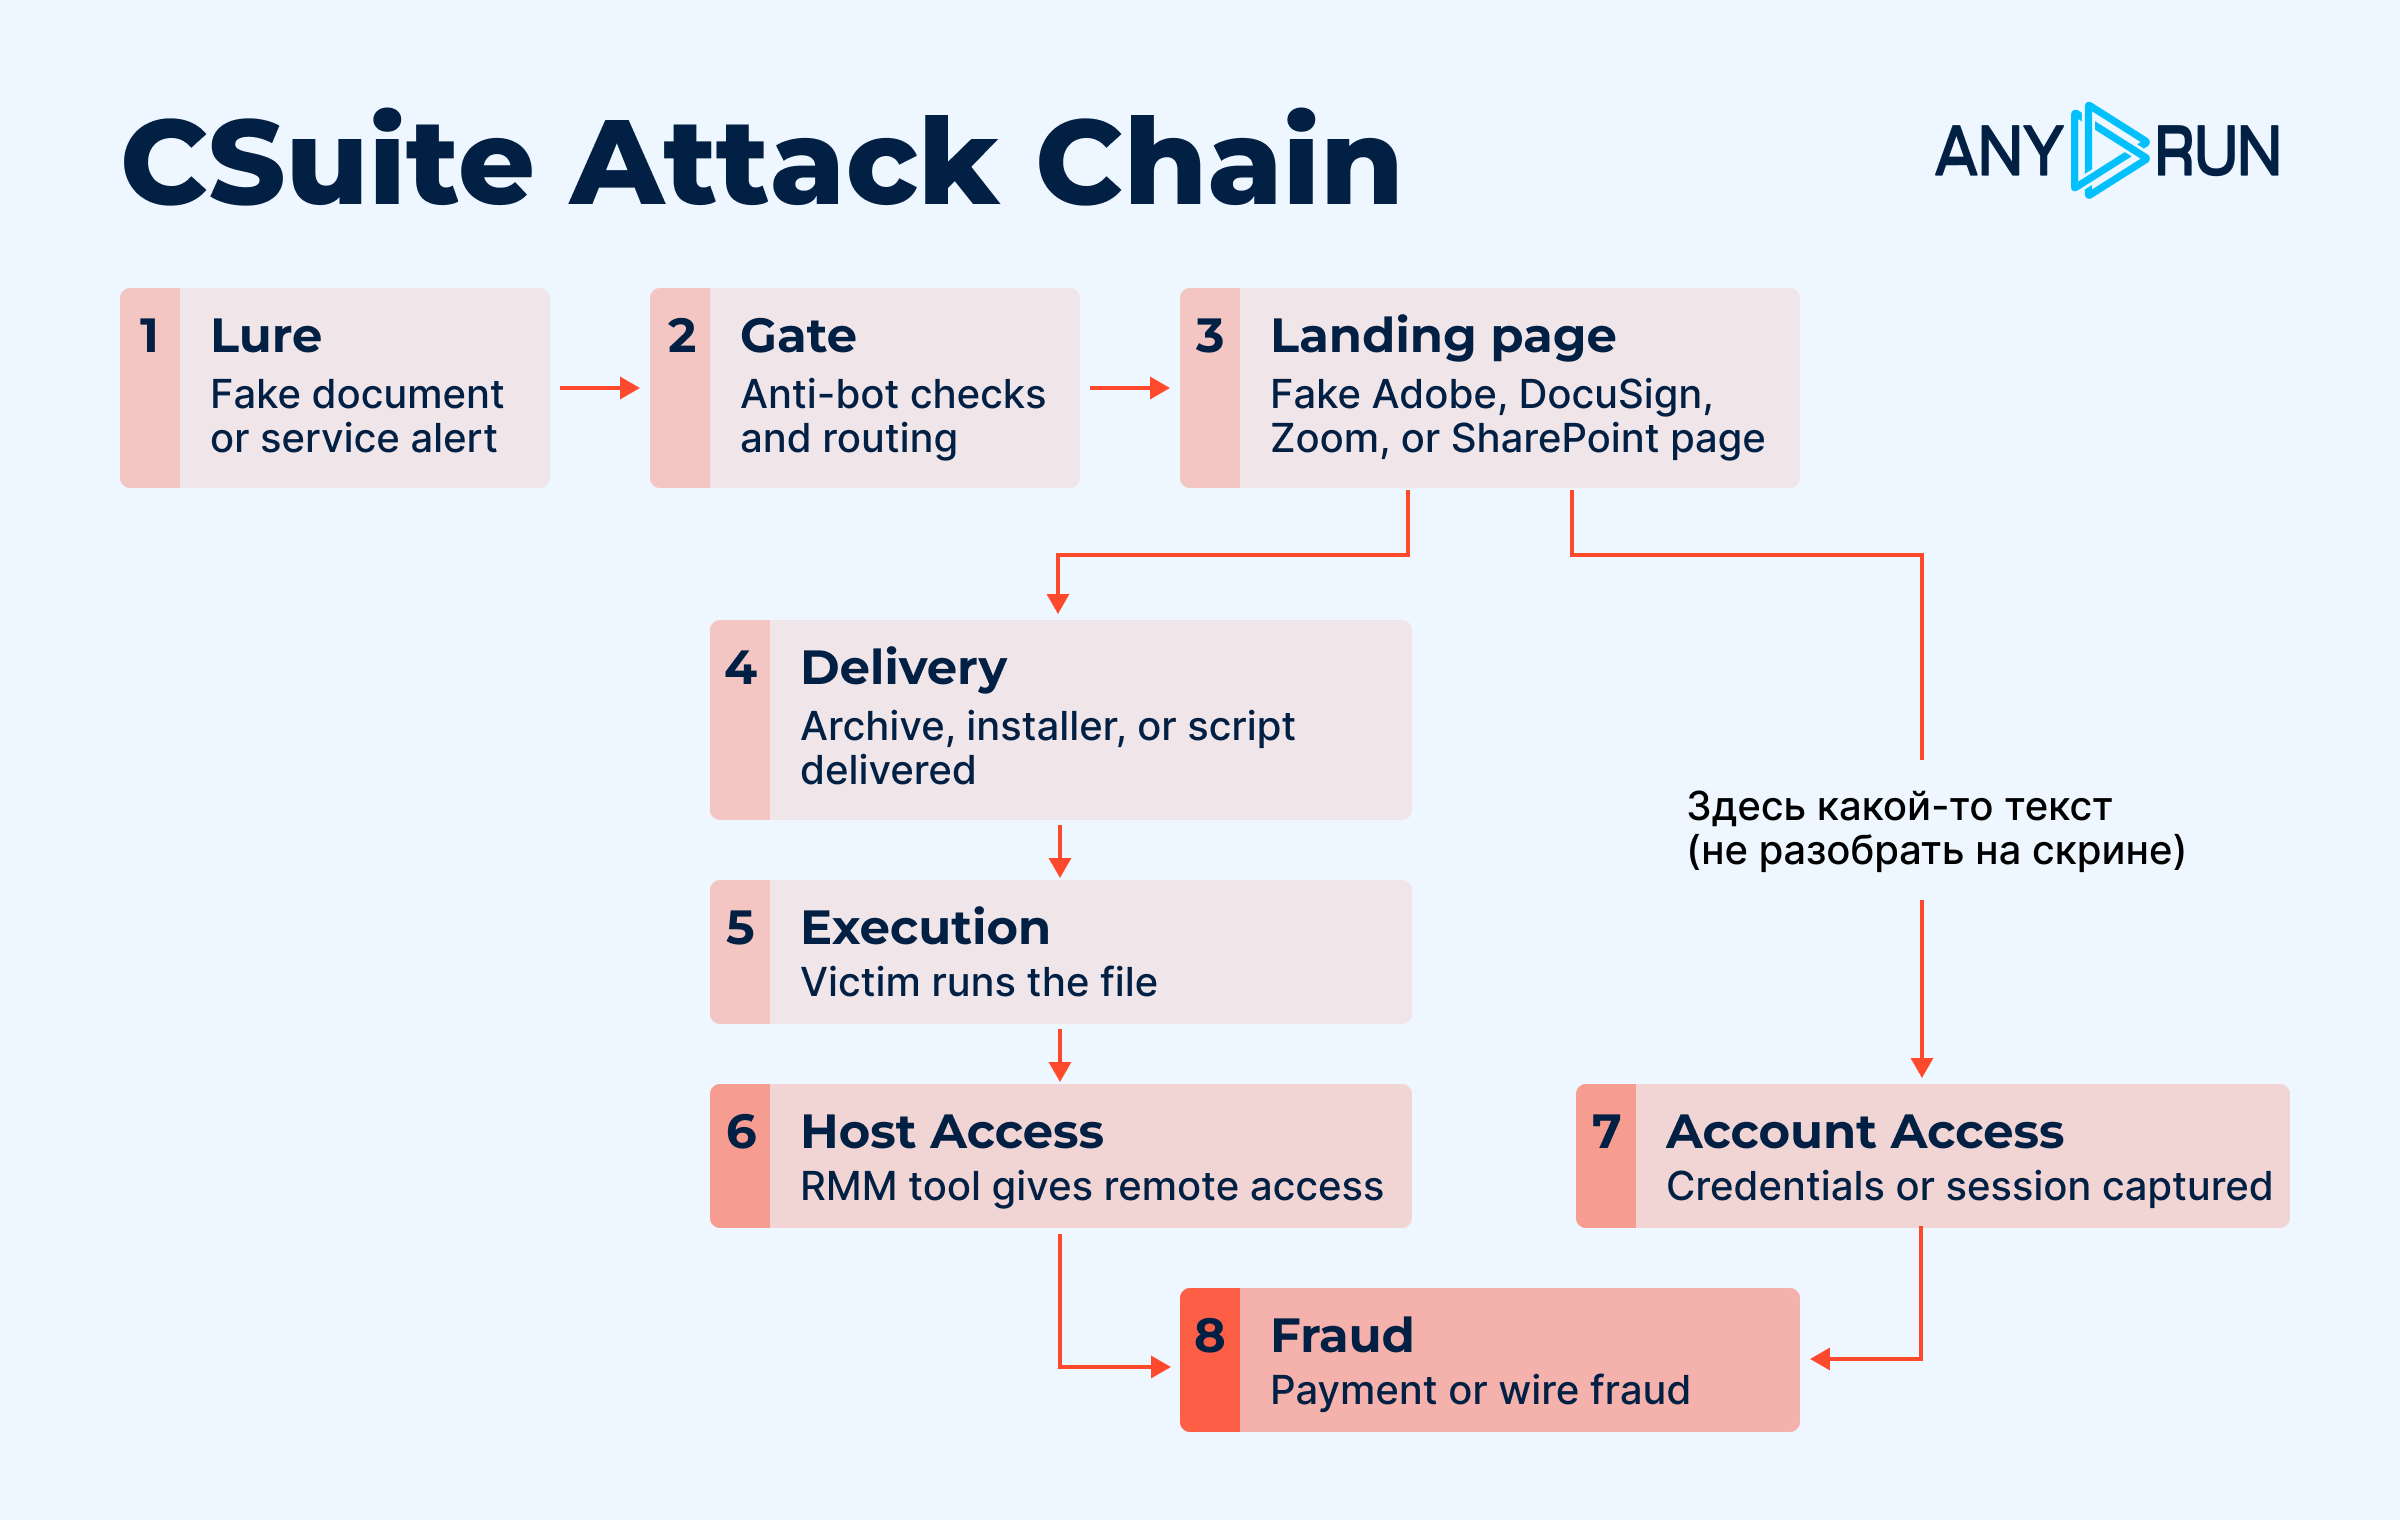
Stage 1: Business-Themed Phishing
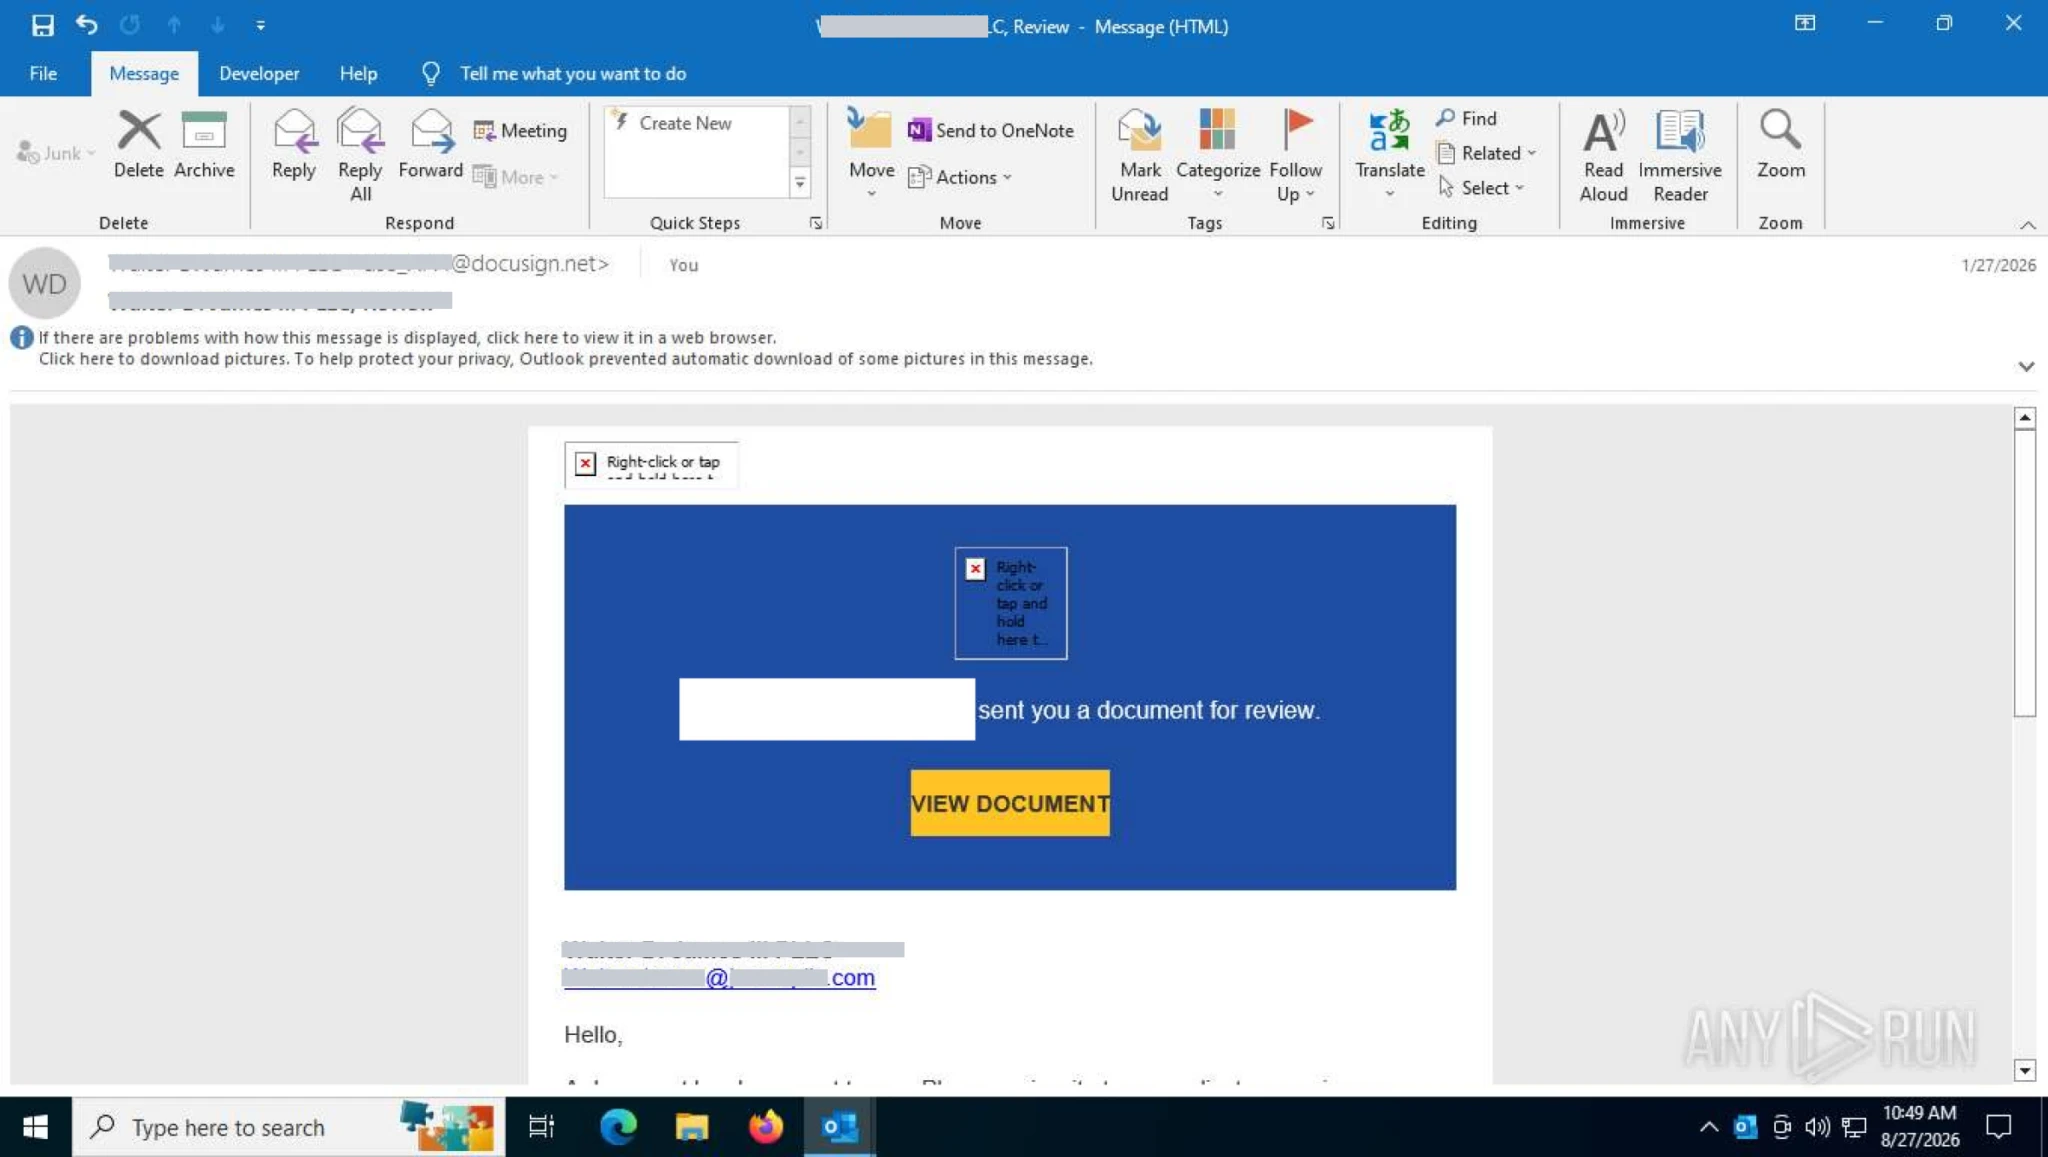
The attack can begin with a message asking the recipient to review a document, sign an agreement, or complete a business-related task.
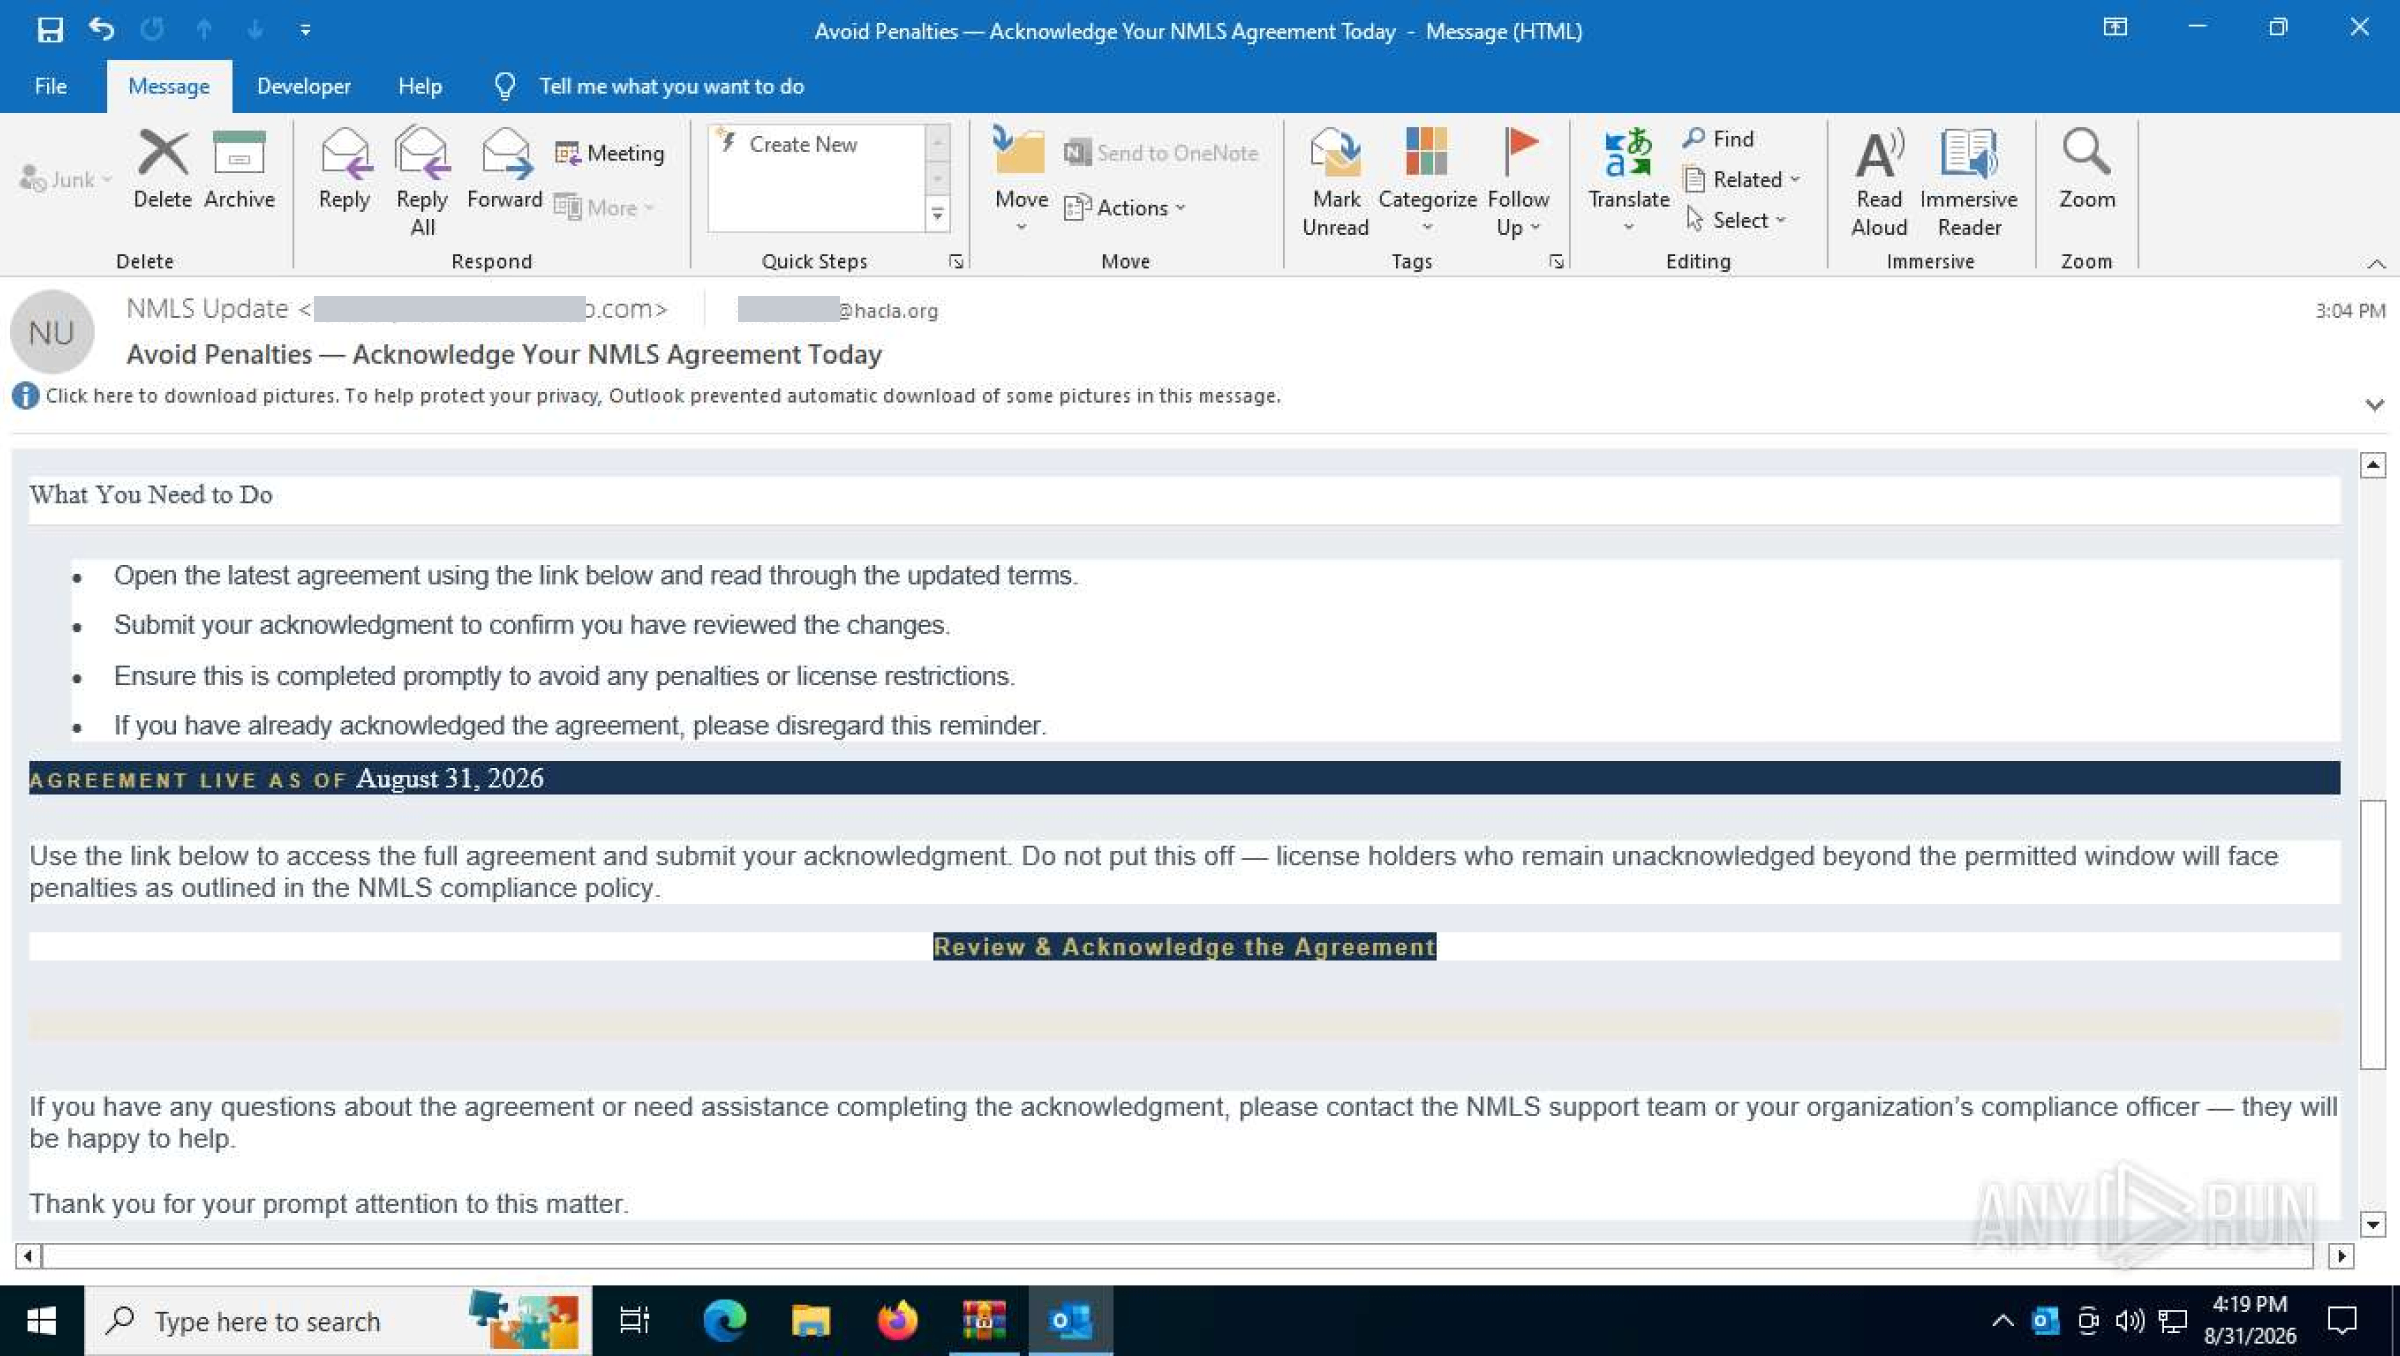
Campaign themes have included Adobe Document Cloud invitations, DocuSign envelopes, Zoom, Dropbox, and other familiar business services. The messages may use legitimate-looking notifications and time-sensitive requests to encourage recipients to follow a link.
In some observed cases, invitations were sent from mailboxes already controlled by the operation. Other messages came through dedicated sending infrastructure.
Stage 2: Traffic Filtering and Redirection
After a victim visits a link, the initial host can act as a redirector. It may perform anti-automation checks and inspect information supplied by the visitor before selecting the next destination.
The resulting path can depend on the account provider. Visitors may be directed toward Microsoft-specific or Google-specific authentication pages, while others are routed to a more generic credential-harvesting destination.
This routing allows the operation to present different experiences to different visitors rather than sending every user through an identical flow.
Stage 3: Counterfeit Document and Authentication Pages
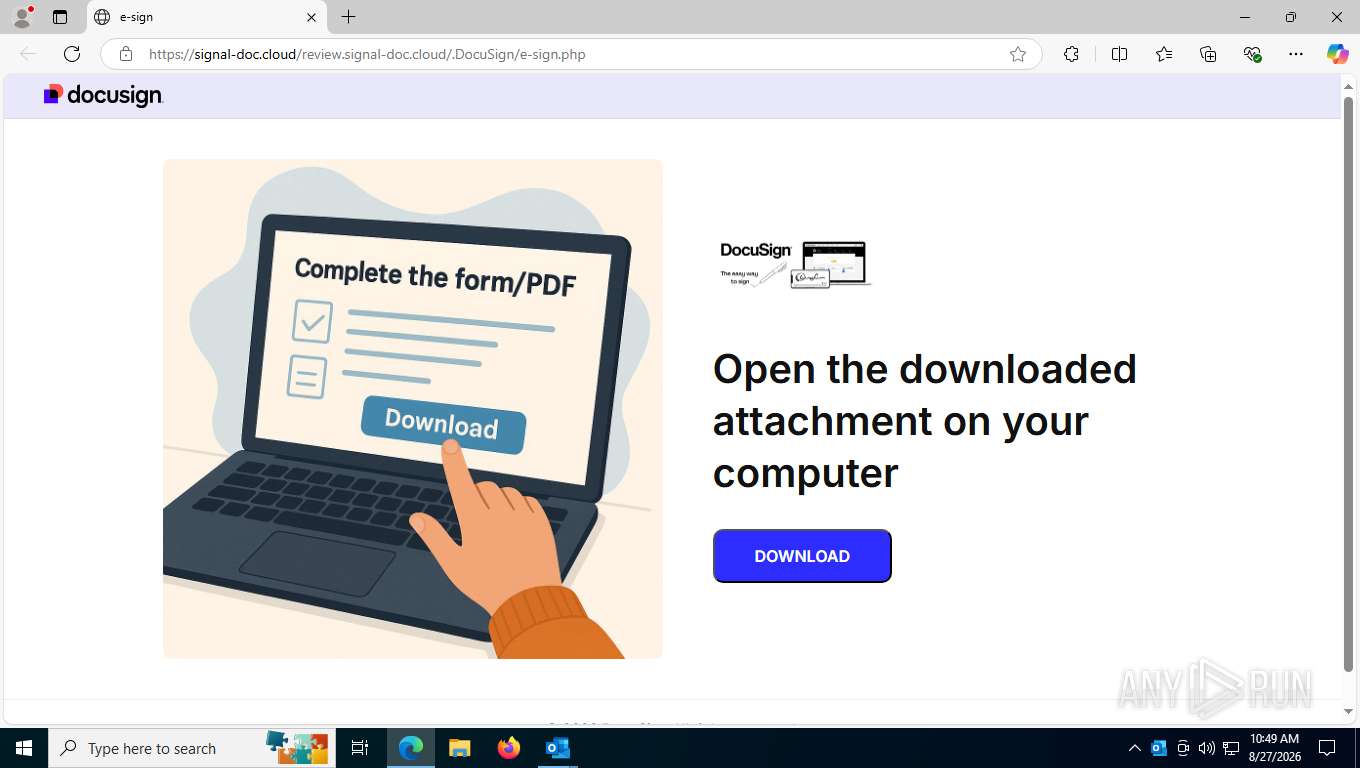
The victim may encounter a fake document viewer designed to resemble Adobe Reader, DocuSign, Zoom, or another trusted service.
These pages can display a document that appears to be waiting to load or requires an update or download before it can be viewed. Their purpose is to make the requested action seem like a normal part of a business workflow.
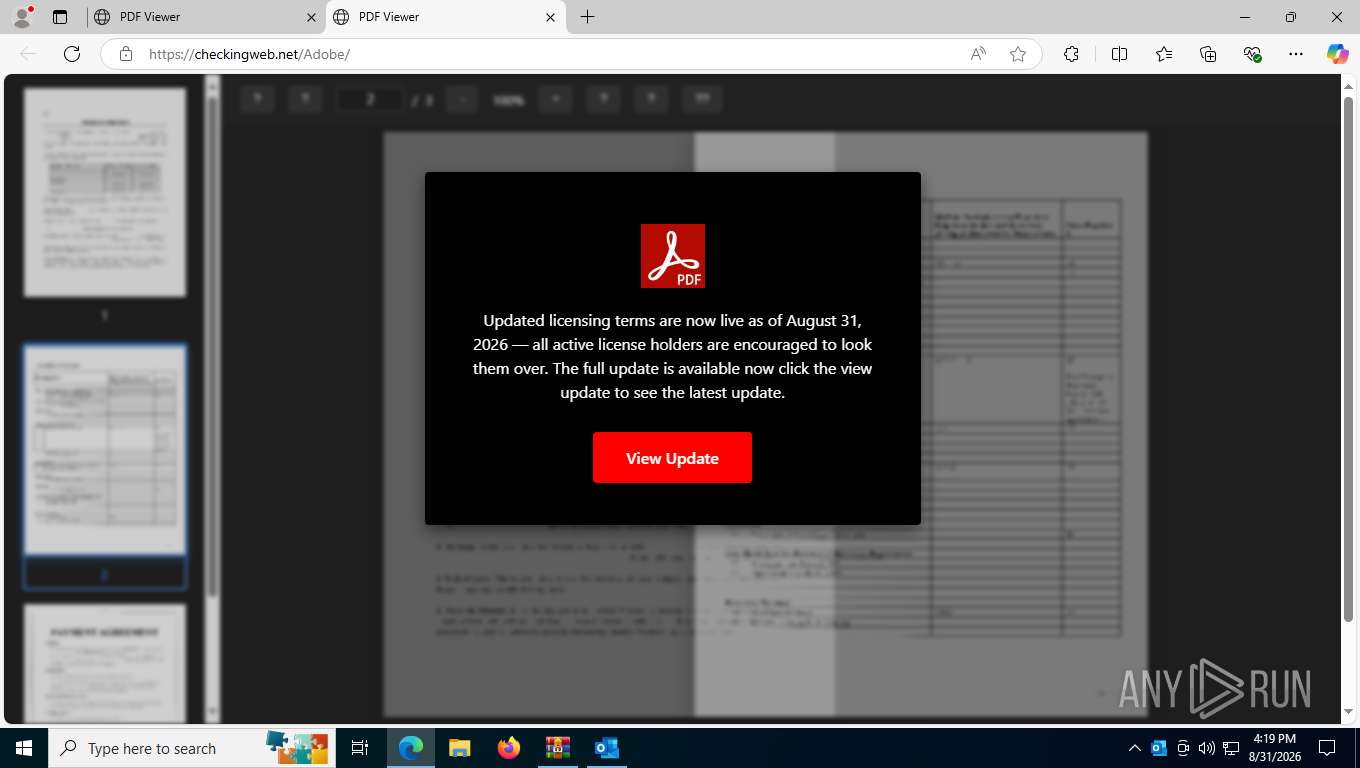
Observed pages have also collected visitor information and sent notifications to the operators. This can provide details about a visitor's network location, browser, operating system, and device environment.
Stage 4: Payload Delivery and Execution
On the remote-access branch, the page directs the victim to download a file presented as a document viewer, update, or related business utility.
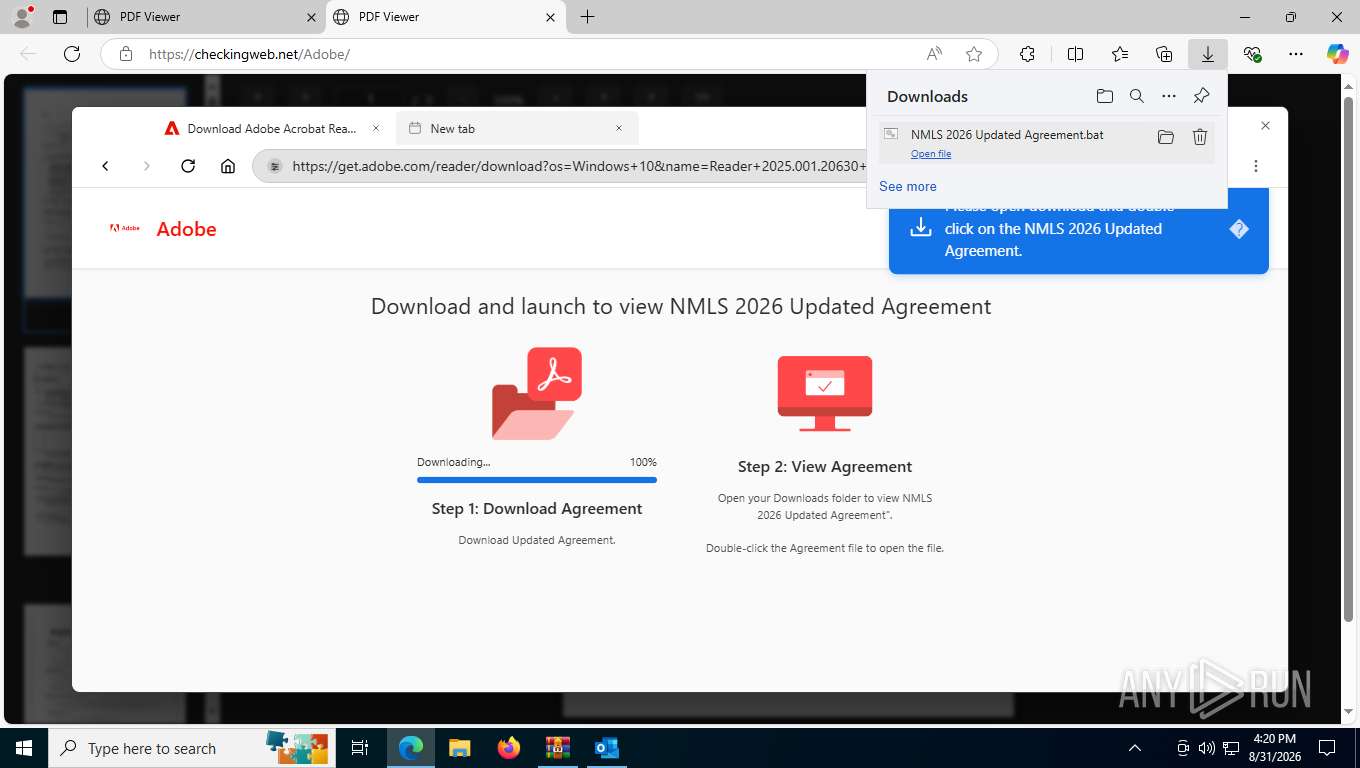
The delivered content may be an archive, installer, batch script, or Visual Basic Script. Some lightweight scripts act as droppers, retrieving an installer when executed.
In the Windows activity documented by ANY.RUN, a script could request elevated privileges and invoke the Windows Installer utility to install a remote-management client.
The key transition occurs when a seemingly routine document-viewing action leads to the execution of software that provides unauthorized access to the endpoint.
Stage 5: Remote-Management Software Deployment
Instead of relying exclusively on a custom remote-access trojan, CSuite can abuse legitimate remote-management and endpoint-management applications.
Observed tools include ScreenConnect, Action1, Atera, Syncro, and PDQ Connect. When installed or configured under an attacker's control, such software can provide remote access or management capabilities on the compromised device.
Some observed configurations also involved endpoint-management agents enrolling devices into tenants controlled by the operator.
Because these products have legitimate administrative uses, their presence alone does not establish malicious activity. Investigators must consider whether the installation, tenant association, account, and subsequent behavior are authorized.
Stage 6: Credential and Session Theft
The alternative attack path focuses on the victim's identity rather than deploying a remote-management agent.
CSuite can use phishing pages and device-code authentication flows to obtain credentials or access to an active Microsoft 365 session. The resulting access can allow an operator to interact with a compromised mailbox without necessarily repeating the original authentication process.
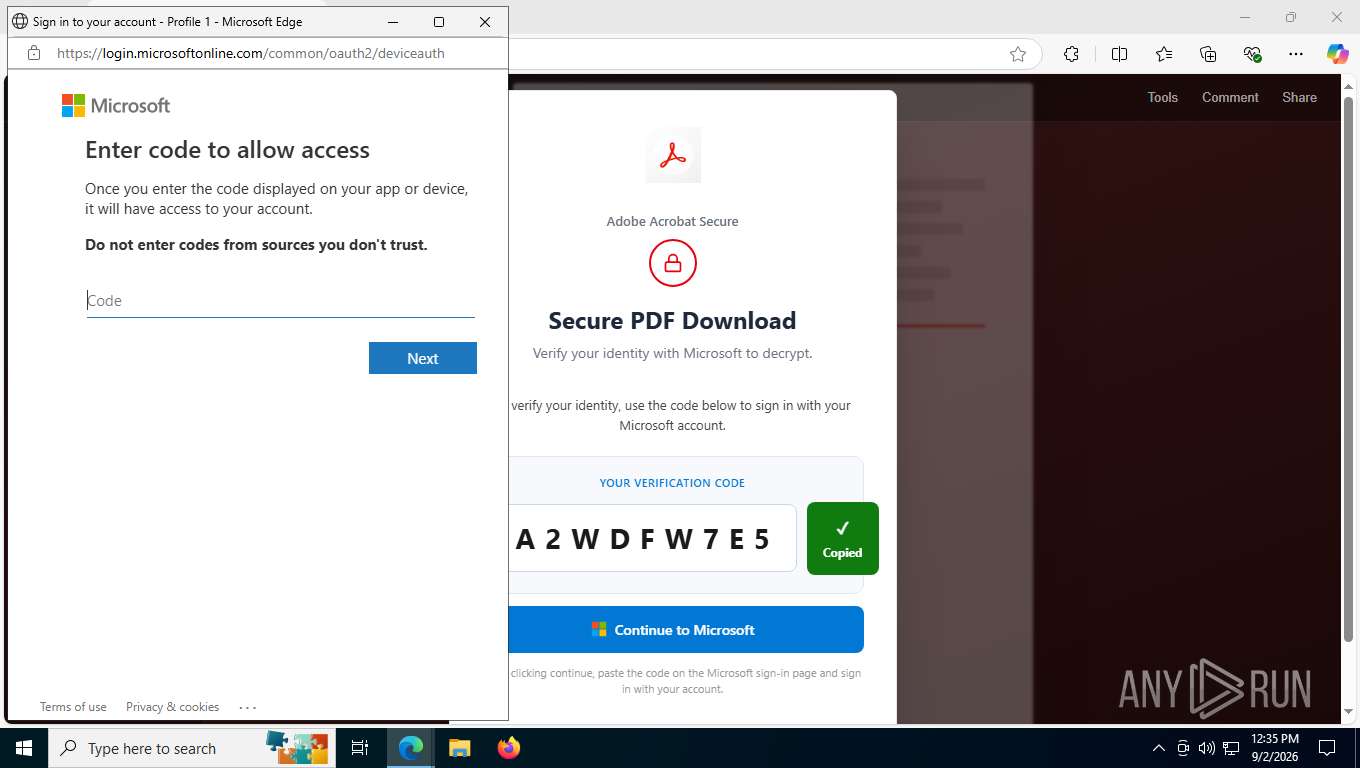
A stolen session can complicate response because changing a password alone may not immediately invalidate every existing session or token. Organizations need to investigate active sessions and revoke access through the relevant identity-management controls.
Stage 7: Continued Access and Follow-On Activity
Once an account or endpoint has been compromised, the operation can create opportunities for further activity.
Endpoint access may allow an attacker to reconnect through the deployed management software. Account access may provide visibility into business conversations, enable impersonation, or support attempts to manipulate financial transactions.
The two paths can create overlapping risks when both an employee's identity and device are compromised.
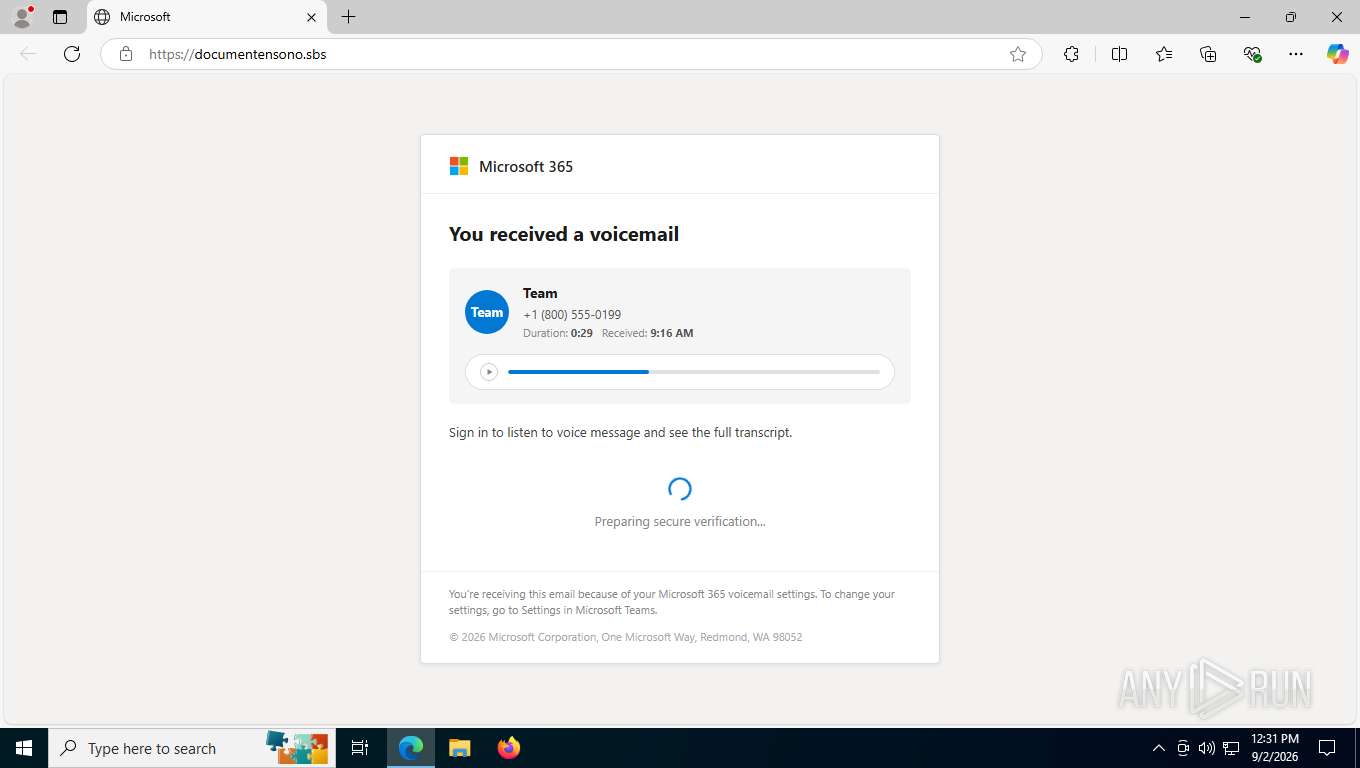
ANY.RUN's analysis also describes connections between the operation's phishing infrastructure, management panel, operator accounts, and data-collection endpoints. These relationships can help investigators connect seemingly separate incidents to a broader campaign.
Understanding CSuite's Observable Behavior
Several recurring behaviors can help security teams recognize activity associated with CSuite:
- Business-themed lures: Messages that imitate document-sharing, electronic-signature, conferencing, or Microsoft 365 workflows.
- Counterfeit document viewers: Web pages that imitate trusted services and prompt users to download or install additional software.
- Suspicious script execution: Unexpected batch or VBS files, PowerShell activity, or installer execution following a browser download.
- Unapproved management agents: Remote-management applications installed outside established IT deployment procedures.
- Unusual tenant enrollment: Devices enrolling in remote-management or endpoint-management environments not owned or approved by the organization.
- Authentication anomalies: Unexpected device-code authentication activity, suspicious sign-ins, or evidence of compromised Microsoft 365 sessions.
- Mailbox misuse: Unusual email access, suspicious forwarding changes, unexpected messages, or activity associated with payment redirection.
- Related infrastructure: Recurring URLs, domains, page resources, or network connections that link apparently separate phishing events.
No single indicator should be treated as definitive proof of CSuite activity. The most useful assessment combines endpoint, network, browser, and identity evidence to establish how the incident unfolded.
How Threat Intelligence Can Support CSuite Investigations
CSuite uses multiple services and tools, which means an isolated domain or file may reveal only a small part of an incident.
ANY.RUN’s Threat Intelligence can help analysts connect suspicious artifacts with related infrastructure, historical activity, and additional samples. This is especially useful when investigating campaigns that reuse page components or change delivery infrastructure over time.
Threat Intelligence Lookup can be used to help security teams strengthen their investigations by correlating:
- Suspicious URLs and domains
- Downloaded files and their associated processes
- Remote-management software and installation events
- Authentication logs and Microsoft 365 session activity
- Network connections made during execution
- Related phishing pages and recurring web resources
- Other endpoints showing similar behaviors
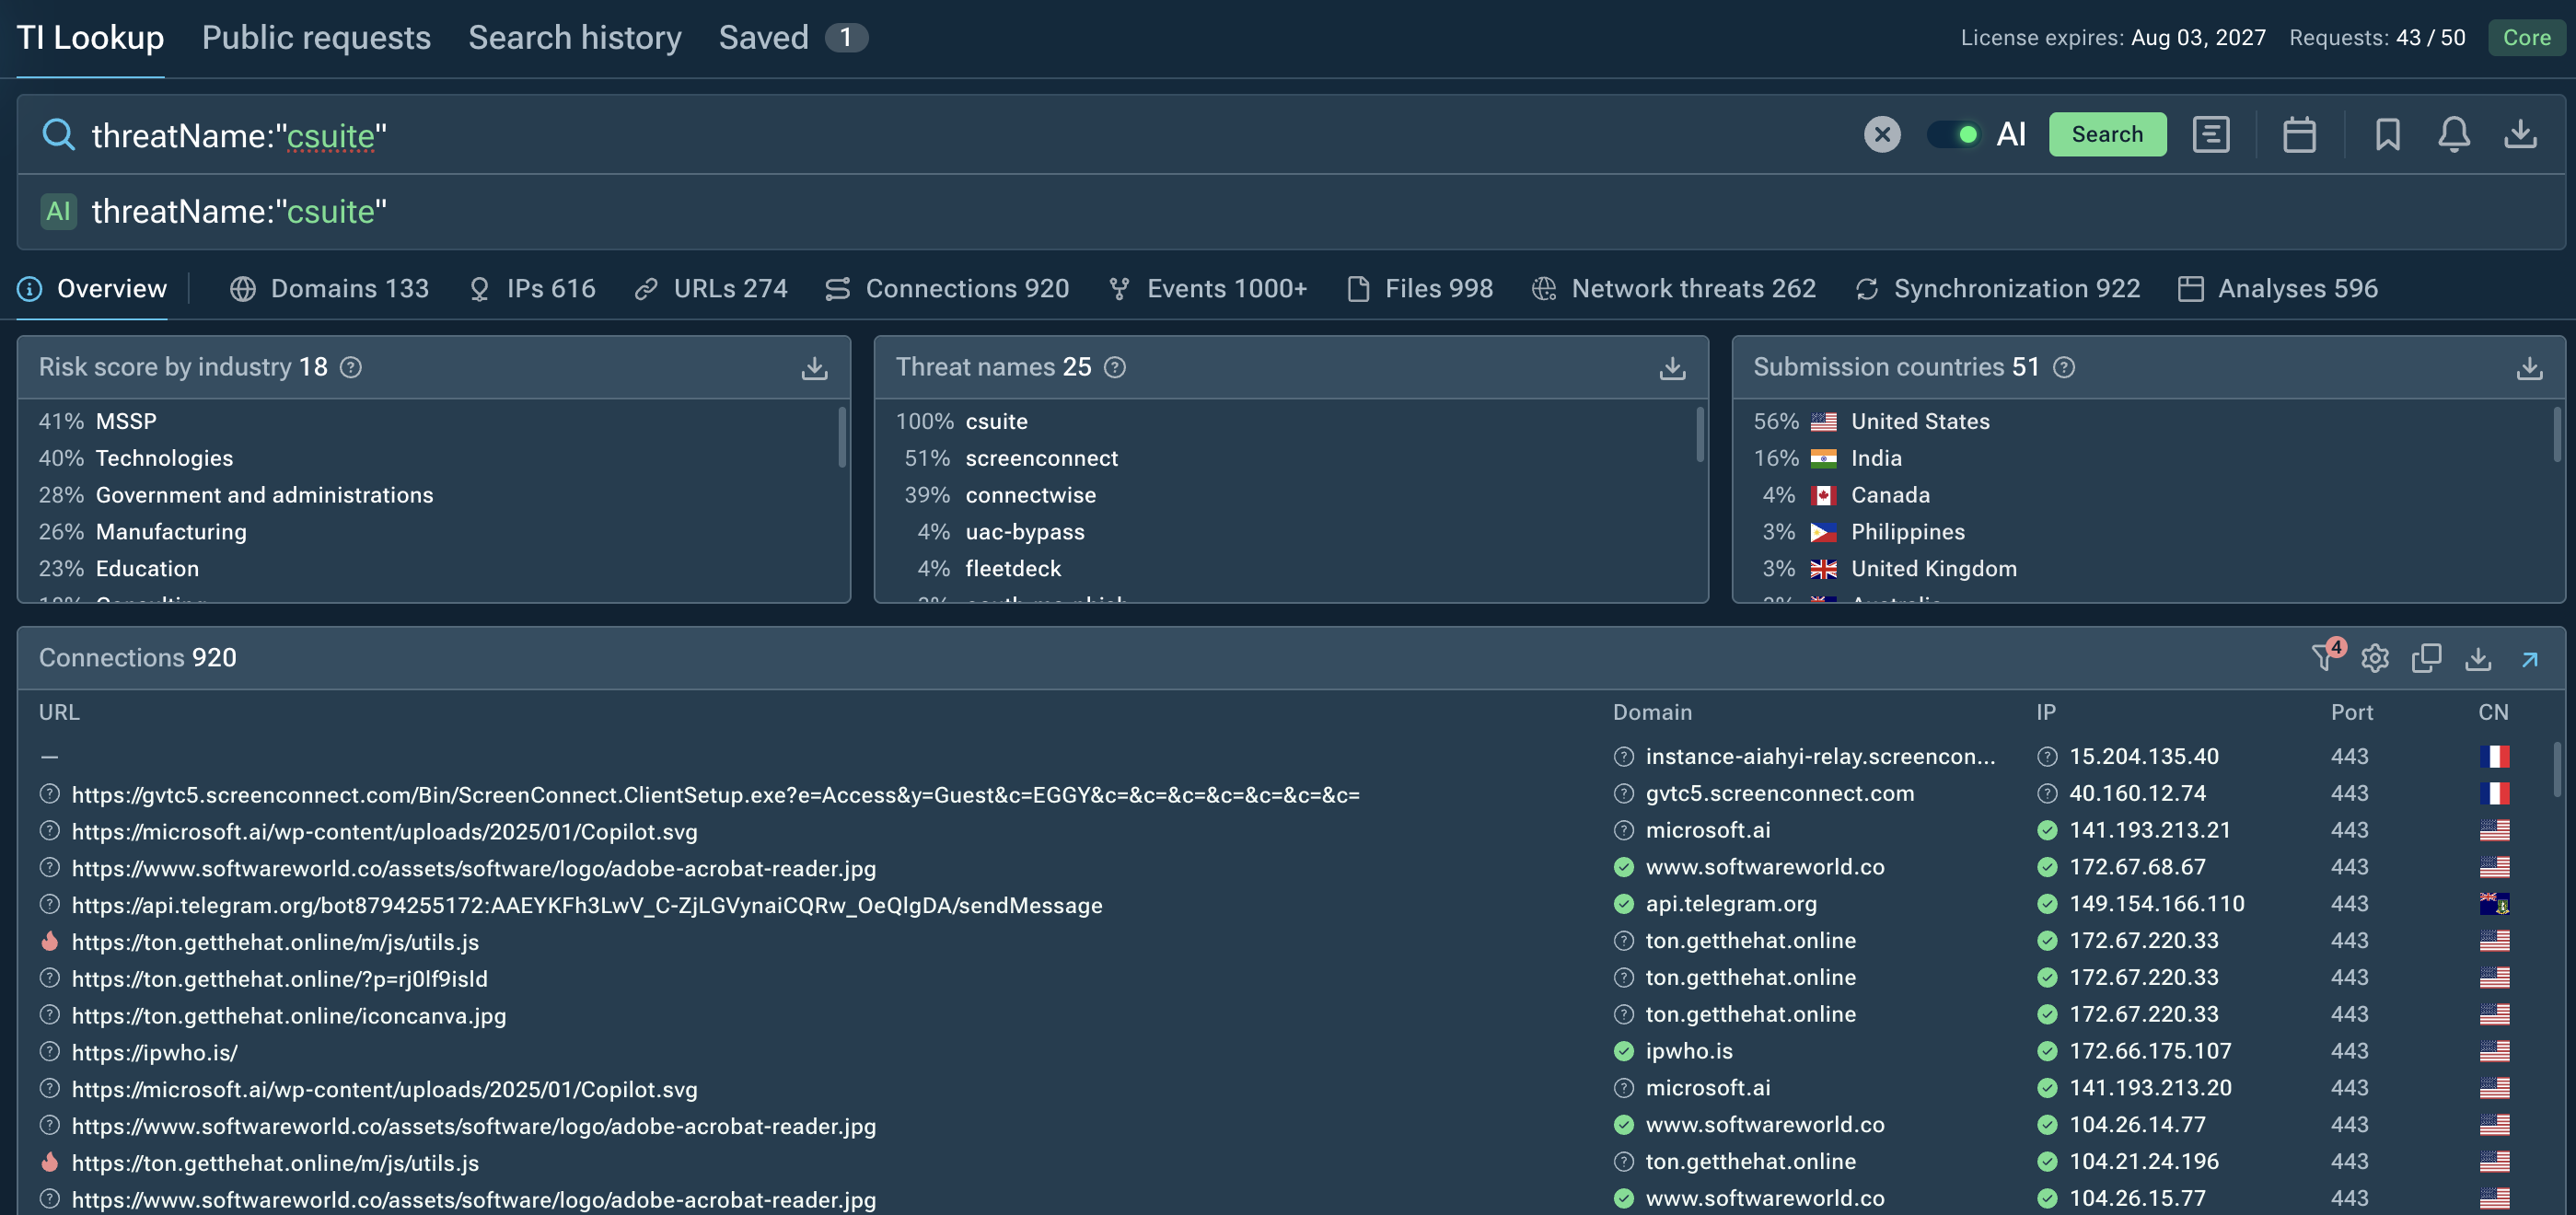
ANY.RUN’s Interactive Sandbox analysis can help reveal redirects, scripts, payload delivery, process execution, and network communication in an isolated environment. Threat intelligence can then provide broader context for determining whether the observed behavior is part of a larger campaign.
The goal is to move beyond identifying a suspicious file and reconstruct the sequence of events that led to account or endpoint compromise.
CSuite Detection Indicators
Defenders investigating potential CSuite activity should pay attention to the following signals.
Web and Phishing Indicators
- Unexpected document-sharing invitations and electronic-signature requests
- Login or document-viewing pages hosted on unfamiliar domains
- Redirect chains leading from business-themed messages to suspicious downloads
- Pages imitating trusted software providers while requesting an installer or update
- Repeated web-resource paths associated with suspicious document-viewing pages
Endpoint Indicators
- Batch or VBS scripts launched shortly after a browser download
- Unexpected PowerShell execution or installer activity
- New remote-management applications outside approved deployment workflows
- Unrecognized management tenants or remote-access configurations
- Suspicious privilege-elevation prompts associated with downloaded files
Identity and Email Indicators
- Unusual Microsoft 365 sign-ins or device-code authentication events
- Unexpected session activity or access from unfamiliar environments
- Suspicious mailbox rules, forwarding changes, or access patterns
- Messages sent from compromised accounts that imitate normal business communications
- Activity suggesting invoice manipulation or payment redirection
Network Indicators
- Outbound connections associated with unauthorized remote-management clients
- Communications with infrastructure linked to suspicious phishing pages
- Unexpected connections following the execution of downloaded scripts or installers
- Network activity that correlates with suspicious authentication or endpoint events
Behavioral detections and correlations across multiple data sources are generally more resilient than relying exclusively on individual filenames or domains, which can change between campaigns.
CSuite Incident Response: Recommended Actions
If CSuite-related activity is suspected, organizations should investigate both identity compromise and potential unauthorized endpoint access.
Recommended actions include:
- Contain affected endpoints: Isolate suspected devices where appropriate, following established incident-response procedures.
- Secure compromised identities: Reset affected credentials, revoke active sessions and refresh tokens where supported, and investigate suspicious authentication activity.
- Remove unauthorized remote access: Identify and disable unapproved remote-management agents, accounts, configurations, and management-tenant enrollments.
- Preserve forensic evidence: Retain relevant email messages, browser records, endpoint telemetry, process data, downloaded files, and network logs before making changes that could destroy evidence.
- Investigate the execution chain: Determine how the initial message reached the victim, which pages were visited, what files were downloaded, and what processes were executed.
- Examine Microsoft 365 activity: Review sign-ins, mailbox access, forwarding rules, suspicious messages, and other account changes.
- Assess business email compromise: If a mailbox was accessed, examine conversations involving invoices, payments, supplier changes, and sensitive business requests.
- Search for related activity: Look for similar phishing messages, unauthorized management software, suspicious authentication events, and matching infrastructure across other endpoints.
- Validate eradication: Confirm that compromised sessions have been invalidated, unauthorized access paths removed, and affected systems restored to a trusted state.
- Strengthen preventive controls: Review phishing defenses, device-code authentication policies, application allowlisting, remote-management authorization, and endpoint monitoring.
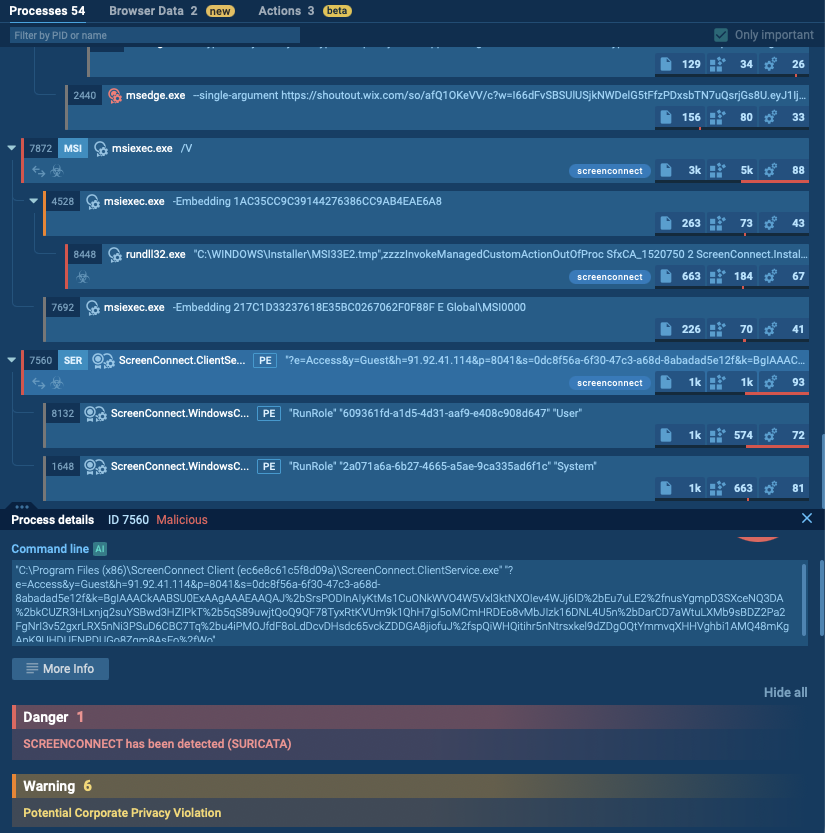
Because CSuite can affect both user identities and endpoints, resolving only one part of the incident may leave another access path available. Response teams should validate both sides before closing the investigation.
Conclusion
CSuite is a multi-stage phishing and remote-access operation that combines business-themed social engineering with credential theft, Microsoft 365 session compromise, and the misuse of legitimate management software.
Its approach creates two significant avenues for organizational compromise: access to corporate identities and access to employee devices. Familiar document-sharing workflows and legitimate administrative applications can make these attacks more difficult to distinguish from normal business activity.
For defenders, the most valuable detection opportunities lie in connecting the initial phishing message to subsequent browser activity, script execution, software installation, authentication events, and remote connections.
Combining identity monitoring, endpoint telemetry, network investigation, and threat intelligence can help organizations identify related activity earlier, contain compromised access, and reduce the likelihood of further business disruption.
Frequently Asked Questions: CSuite
1. What is CSuite?
CSuite is a phishing and remote-access operation that combines credential theft, Microsoft 365 session hijacking, and the abuse of legitimate remote-management tools to gain access to organizational accounts and devices.
2. How does CSuite infect or compromise a system?
CSuite can use business-themed phishing pages to persuade victims to download and execute scripts or installers that deploy remote-management software. An alternative path uses credential-harvesting and device-code authentication techniques to compromise user accounts and sessions.
3. Which organizations does CSuite target?
Observed activity has affected organizations across technology, manufacturing, government, consulting, education, and other sectors. Reporting has shown a strong US focus, with activity also identified in Europe and other regions.
4. Which remote-access tools are associated with CSuite?
Reported tools include ScreenConnect, Action1, Atera, Syncro, and PDQ Connect. These are legitimate products whose use becomes suspicious when they are installed, configured, or administered without organizational authorization.
5. Does CSuite target Microsoft 365 accounts?
Yes. CSuite has been associated with credential theft, device-code phishing, and the theft of active Microsoft 365 sessions. Compromised accounts can expose mailboxes and enable further impersonation or business email compromise.
6. What makes CSuite difficult to detect?
CSuite can imitate trusted business services and abuse legitimate software. This means suspicious activity may resemble ordinary document access, software installation, remote administration, or authentication unless analysts correlate the surrounding events.
7. What indicators can help identify CSuite activity?
Useful indicators include counterfeit document pages, suspicious download-and-execution chains, unexpected remote-management installations, unusual Microsoft 365 authentication activity, and related network or web infrastructure. These signals should be evaluated together rather than in isolation.
8. How should organizations respond to a suspected CSuite incident?
Organizations should contain affected endpoints, secure compromised accounts, revoke active sessions, investigate unauthorized management software, preserve evidence, and search for related activity across the environment. They should also examine potentially compromised mailboxes for fraud and impersonation.
9. How can interactive sandboxing and threat intelligence help investigate CSuite?
Interactive sandboxing allows analysts to investigate CSuite’s attack chain, including phishing redirects, suspicious script execution, remote-management tool deployment, and network communications.
Threat intelligence can then help connect observed indicators with related phishing URLs, domains, suspicious files, remote-access infrastructure, and other activity associated with CSuite.
10. How can organizations reduce the risk of CSuite attacks?
Organizations should strengthen phishing defenses, apply strong identity controls, review device-code authentication policies, monitor for unauthorized remote-management tools, and correlate endpoint and identity events. Employees should also be cautious when document-viewing pages request unexpected downloads, updates, or authentication actions.
Other malware & phishing threats
 DarkVisionDarkVision RAT is a low-cost, modular Remote Access Trojan that gives attackers remote control of infected Windows hosts. Initially observed around 2020 and sold in underground marketplaces, DarkVision has become notable for its full feature set (keylogging, screen capture, file theft, remote command execution and plugin support) and for being distributed via multi-stage loaders in recent campaigns.
 GootLoaderGootLoader is an initial-access-as-a-service malware that operates by delivering the GootKit banking trojan and other malicious payloads. It utilizes techniques such as fileless execution and process injection to avoid detection. The malware is often distributed through SEO poisoning and compromised websites, deceiving users into downloading infected files.
 Balada InjectorBalada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
 GuLoaderGuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
 Bumblebee LoaderBumblebee is a highly adaptable malware loader, often used by threat actors linked to the Conti and TrickBot cybercrime groups. Since its discovery in 2021, Bumblebee has been leveraged in phishing campaigns and email thread hijacking, primarily to distribute payloads like Cobalt Strike and ransomware. The malware employs obfuscation techniques, such as DLL injection and virtual environment detection, to avoid detection and sandbox analysis. Its command-and-control infrastructure and anti-analysis features allow it to persist on infected devices, where it enables further payload downloads and system compromise.