INC Ransomware
- 49
- Global rank
- 37
- Month rank
- 41
- Week rank
INC Ransomware is a ransomware-as-a-service (RaaS) spotted in mid-2023. It targets industries like retail, real estate, finance, healthcare, and education, primarily in the U.S. and UK. It encrypts and exfiltrates data demanding a ransom. It employs advanced evasion techniques, destroys backup, and abuses legitimate system tools at all the stages of the kill chain.
- Ransomware
- Type
- Unknown
- Origin
- 1 May, 2023
- First seen
- 20 October, 2026
- Last seen
How to analyze INC Ransomware with ANY.RUN
IOCs
IP addresses
- 74.179.77.204
- 20.190.159.128
- 23.11.40.157
- 135.233.95.135
- 131.253.33.203
- 172.211.123.250
- 48.209.133.15
- 150.171.109.101
- 48.192.1.65
- 2.16.204.138
- 23.59.18.102
- 48.192.1.64
- 48.209.138.189
- 23.52.181.212
- 135.232.92.97
- 135.232.92.137
- 2.23.246.101
- 23.3.89.96
- 20.190.160.5
- 204.79.197.203
Hashes
- a4e5b9e377a10dcf8f4a8be4ab389a947396f0232a4bf36b69473871b5488dce
- e54da05cdbba0f009cf2b242d3e624cb2f12b25baccab54d1bcd9cca0e7ea84c
- ca02f60942a43d8f8b973baa3231df1f8c26328750baa2ed8d4cf07335084ebb
- c4b6be73cc43c32971545c5ab3db0bbbdc1b528359fd4b7bc7d4d29e1851cbd6
- f674c7fe7933fc90f5a9704cb0c9315bd158f2c831b1af2c4189c9c548872898
- 4960bf2152341e815dc05e2ea100a01e6735a348e5eccc1a178881dcfc9e4360
- be78f3ac1115302f264a27da93e83b6651e69106dbb7277e05d91ccc8b1f53a2
- 6e43456f9ec31f48eed04f010c55f9fb9fea0fbd10d3f2e203c9b58269dc8dcf
- a222f683cac203e14a25ec1e10abbea020f69238334b8bdb224b587e2ac41f69
- cdecc9dbaff33518caddf9bac0b3a67f96b5df1fe83638398d3795bbcb2dade6
- a3fd2b56240d59b5eba36a2b9193e087d2db25e1e7e8abfdebd0827a9633636b
- 4bae0c79255b424aad2331c86f951cc55302e634f5e4a6927b75a192687969dd
- 74a9b4e9f83d62df5487d2a69555e4163a6cfd76ea0bd87bf03c9626cfecd0f1
- 081b7b2ea3955232e74fe728cb0edcdbadff87b3e2a60d1f666a920b38d8f86b
- 6e20232239a2f4f367a057416cd7b7668fb9f5ed68cf2d91991b013d4d43b3db
- 64de29839f0b03c2c6d4a827367d03c7f3b3d252cb0b4cec23d5cc79843aee51
- 8e923e377f3a7eb5b6c73b247e55d5d5f227f77a812df0d4239b2cd16ce1c6f9
- 21edd3197bc8ef640049492dc0c58a408f6c6c78658faad462d5f628fe425121
- c64957e980fa4d1c85bf2fe84fdafee38f7e5c91fcae327caacfe55b2440948d
- ad5ce6abab9f0795641ccf866150dc5d46eda415b4f2379d94e30b0513bd8908
Domains
- activation-v2.sls.microsoft.com
- google.com
- fe3cr.delivery.mp.microsoft.com
- crl.microsoft.com
- client.wns.windows.com
- self.events.data.microsoft.com
- www.microsoft.com
- oneocsp.microsoft.com
- slscr.update.microsoft.com
- login.live.com
- ocsp.digicert.com
- nexusrules.officeapps.live.com
- ecs.office.com
- www.bing.com
- settings-win.data.microsoft.com
- th.bing.com
- fundingchoicesmessages.google.com
- pagead2.googlesyndication.com
- copilot.microsoft.com
- t.me
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f20%2f2026%2c%209%3a32%3a37%20am
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://www.bing.com/th?id=odswg.0244f9c2-b57d-4a85-8145-d090983cbcef&pid=dsb
- https://www.bing.com/th?id=odswg.37113cbd-6db2-4d96-abb2-70f97776821f&pid=dsb
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
Last seen at
What is INC Ransomware?
INC Ransomware is a ransomware-as-a-service (RaaS) operated by the INC Ransom group that emerged in 2023. In mid-2024, its source code leaked to dark web and became a foundation of Lynx ransomware, the latter often referred to as “rebranding” or a variant of the former. Both employ double extortion, encrypting victims' data and threatening to leak it unless ransoms are paid.
INC Ransomware uses multiple vectors to infiltrate networks, leveraging both technical exploits and social engineering. These include phishing emails with malicious attachments or links to compromised websites, network access credentials acquired from IABs, malvertising and drive-by downloads, software vulnerabilities. INC Ransomware is used in supply chain attacks targeting third-party vendors or service providers to infiltrate larger networks (SolarWinds attack).
Once in the network, it performs privilege escalation using tools like WinPEAS and starts lateral movement using Cobalt Strike, PsExec, Mimikatz, and the like. It exfiltrates data before encrypting it with a strong algorithm (likely AES + RSA) and leaves a ransom note with payment instructions.
INC Ransom’s evasion techniques include: fileless execution, custom packers and obfuscation, delayed execution. Its living-off-the-land tactic implies the use of legitimate tools like PowerShell, WMI, and PsExec to blend in. The malware exploits SystemSettingsAdminFlows.exe to modify registry keys and disable Windows Defender.
INC Ransom’s Prominent Features
INC Ransomware possesses significant risks since it:
- Targets Critical Infrastructure: healthcare, finance, and retail, where disruptions can endanger lives, financial stability, or supply chains. Attacks on vendors (e.g., Toppan Next Tech affecting DBS and Bank of China) amplify impact across multiple organizations.
- Demands Large Ransom Sums: they often reach millions with INC, Lynx escalating them further.
- Abuses Legacy Systems: INC exploits unpatched or unsupported software, common in healthcare and industrial sectors.
- Uses Double Extortion: combining encryption with data leaks increases pressure on victims to pay. Leaked data can lead to regulatory fines (e.g., GDPR, HIPAA) and reputational damage.
- Acts fast: critical files are encrypted quickly, disrupting operations.
INC Ransom’s Execution Process and Technical Details
Let us follow the execution chain of INC by detonating it in the safe environment of ANY.RUN’s Interactive Sandbox and view the processes and artifacts it inducts.
View the analysis of an INC Ransomware sample.
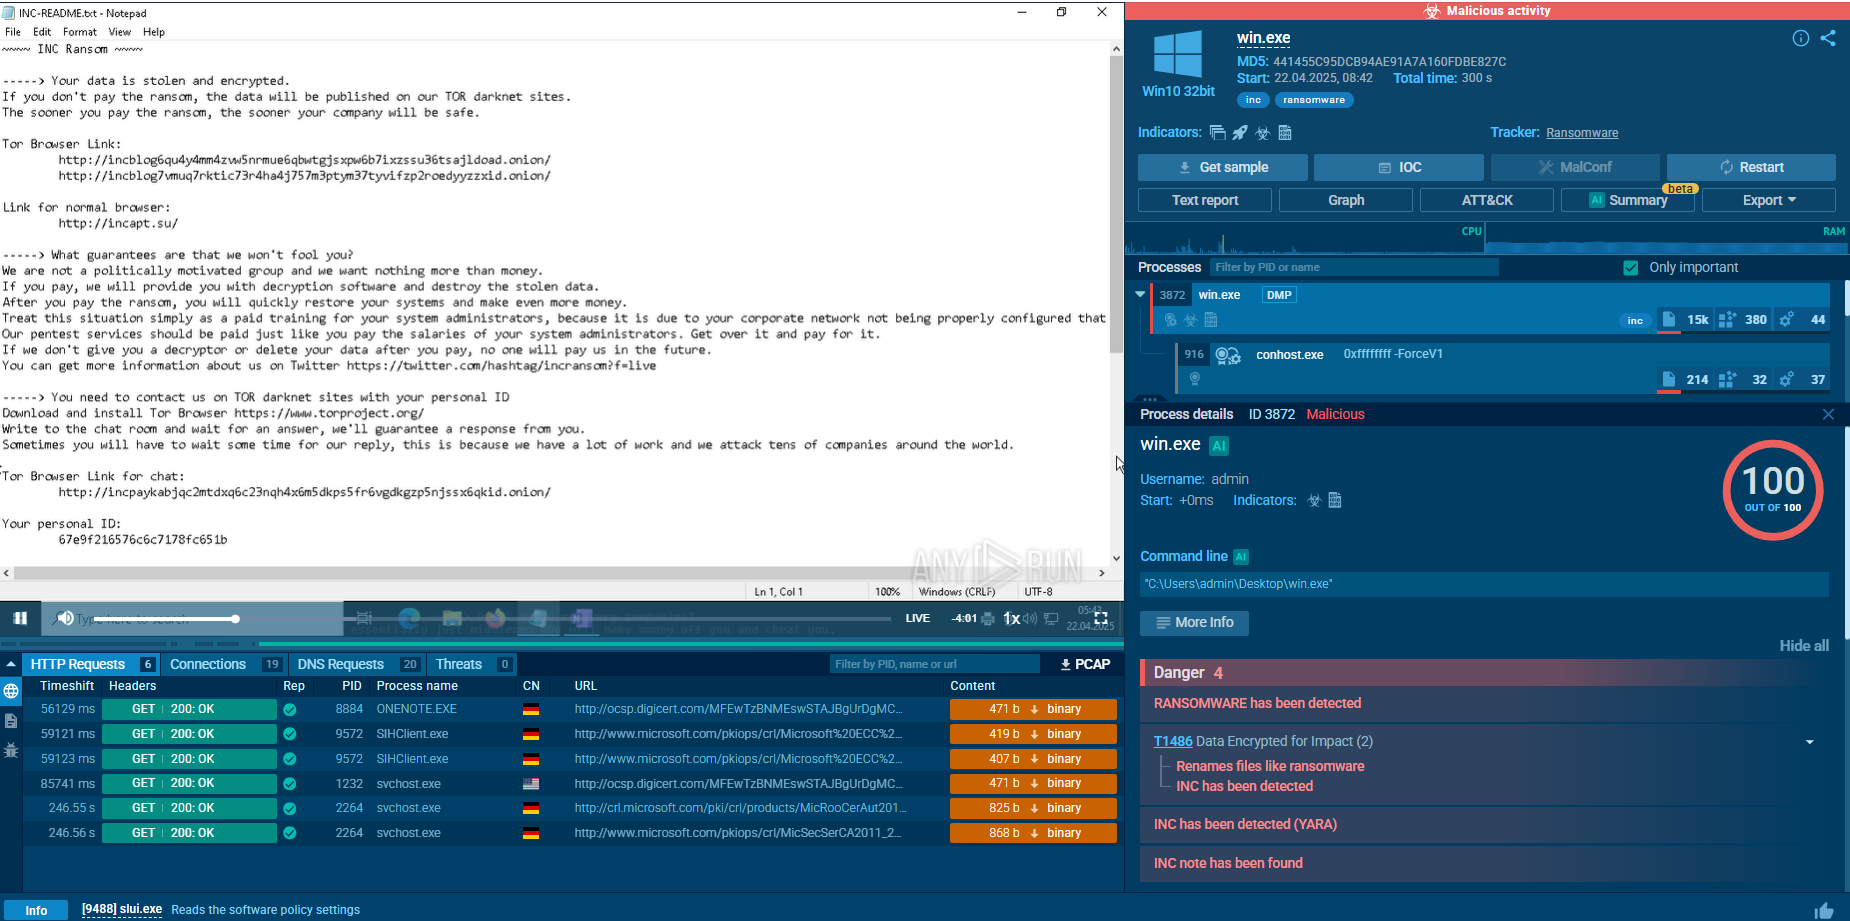
INC ransomware typically gains its initial foothold through phishing, exploitation of unpatched vulnerabilities, or credentials bought from Initial Access Brokers. Once inside, the operators run reconnaissance with commercial red-team tools and built-in Windows utilities to map the network and collect additional credentials.
They pivot laterally using living-off-the-land binaries — such as Notepad, WordPad, and others — to review files while blending in with normal activity. Next, they disable or terminate security software, backup agents, and database services via Service Control Manager APIs and custom “security-killer” tools.
Before encryption, INC tests write access by creating and truncating dummy data on target files; if files are locked, it kills the owning processes or escalates privileges to force access. Operators may also archive data with 7-Zip and exfiltrate it to cloud storage, setting the stage for double extortion. The malware then encrypts all local, mounted, and hidden volumes with AES, offering multiple modes that trade speed for thoroughness.
Finally, it drops ransom notes in .txt and .xps formats and replaces the desktop wallpaper with payment instructions and threats to leak stolen data if the ransom is ignored.
What are the best-known INC attacks?
- British Library (October 2023). One of the first major cultural institutions attacks by INC Ransom. Massive data breach (~500 GB of data leaked, including employee passports, financial records), encryption disrupted online services for weeks.
- Yakult Australia (December 2023). About a million dollars in Bitcoin were demanded from a major beverage company for stolen corporate data (financial records, employee details).
- A city government in Germany (March 2024). Citizen services paralyzed (tax, permits, public records); sensitive documents leaked (court cases, personal IDs). Ransom payment refusal led to prolonged recovery.
- A major oil & gas company in Brazil (April 2024). Operational disruption (delayed shipments, refinery issues); stolen blueprints and contracts leaked. Ransom demand exceeded $5 million.
Gathering Threat Intelligence on INC Ransom
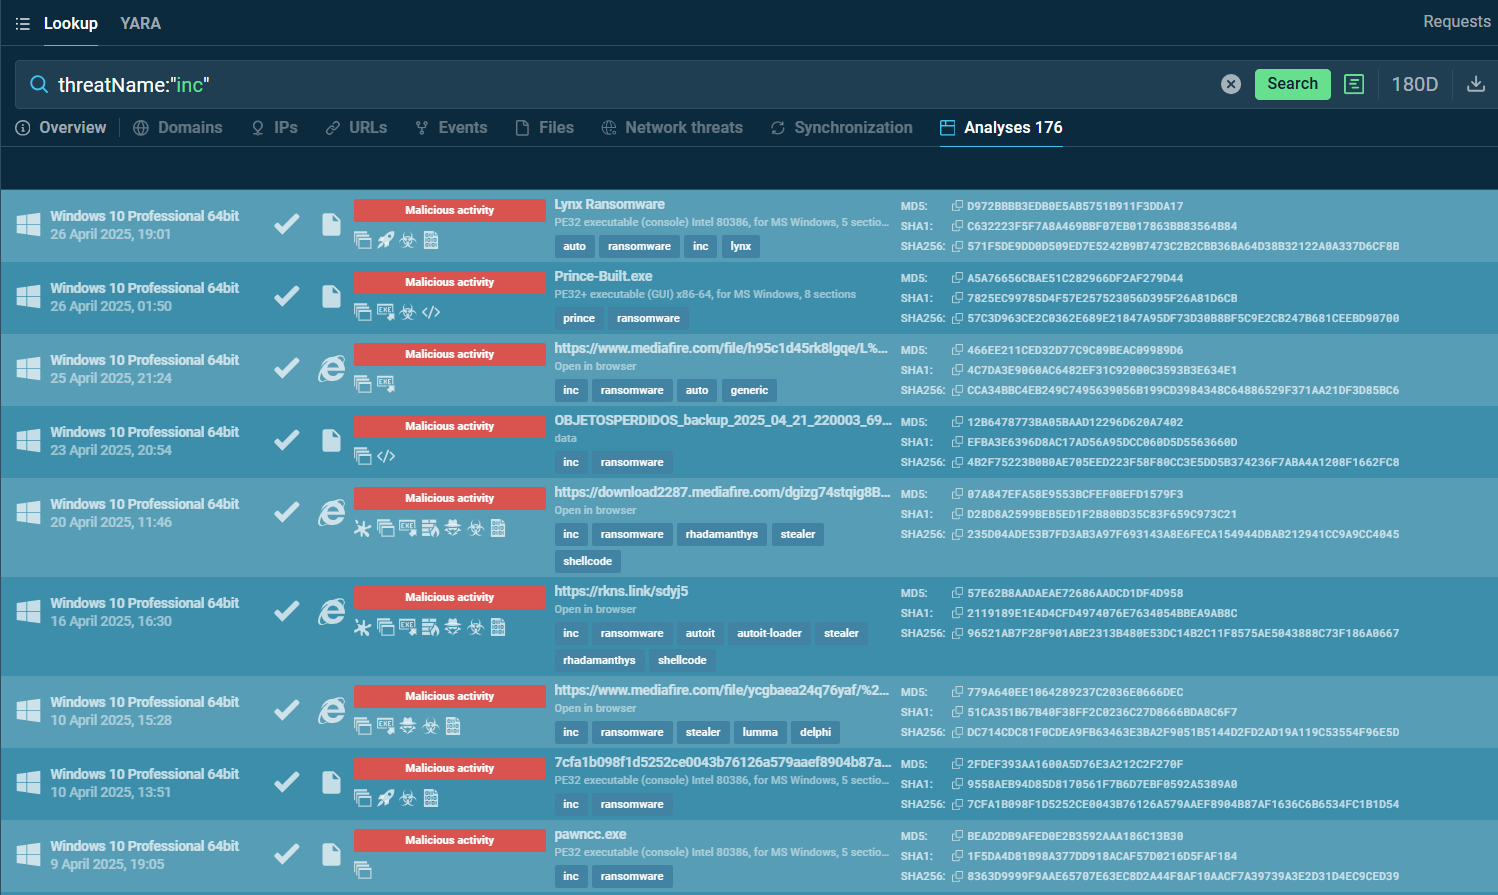
Even when two strains are as closely related as are INC Ransomware and Lynx, you can gather actionable intelligence on them separately using ANY.RUN’s services and analyze their differences and similarities to get a better understanding of malware evolution and to ensure the protection of your own system.
Start with searching by malware’s name via ANY.RUN’s Threat Intelligence Lookup to research more public sample analyses and gather IOCs for tuning your security systems.
Conclusion
INC Ransomware is a dangerous RaaS using phishing, exploits, and LOTL techniques to infiltrate networks, evade detection, and turn to double extortion. It’s particularly threatening to healthcare, finance, and retail due to its disruptive potential and high ransom demands. Detection relies on EDR, behavioral analysis, and TI-driven IOCs, while countermeasures include zero-trust, backups, and patching.
Threat intelligence is critical for tracking its evolving TTPs and predicting variants like Lynx. Organizations should prioritize proactive defenses and TI integration to stay ahead of this adaptable threat.
Start with 50 requests in TI Lookup to collect IOCs on INC Ransom
Other malware & phishing threats
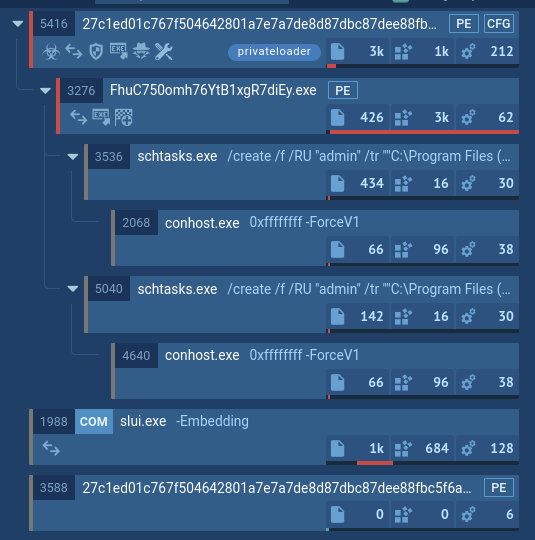 PrivateLoaderPrivateLoader is a malware family that is specifically created to infect computer systems and drop additional malicious programs. It operates using a pay-per-install business model, which means that the individuals behind it are paid for each instance of successful deployment of different types of harmful programs, including trojans, stealers, and other ransomware.
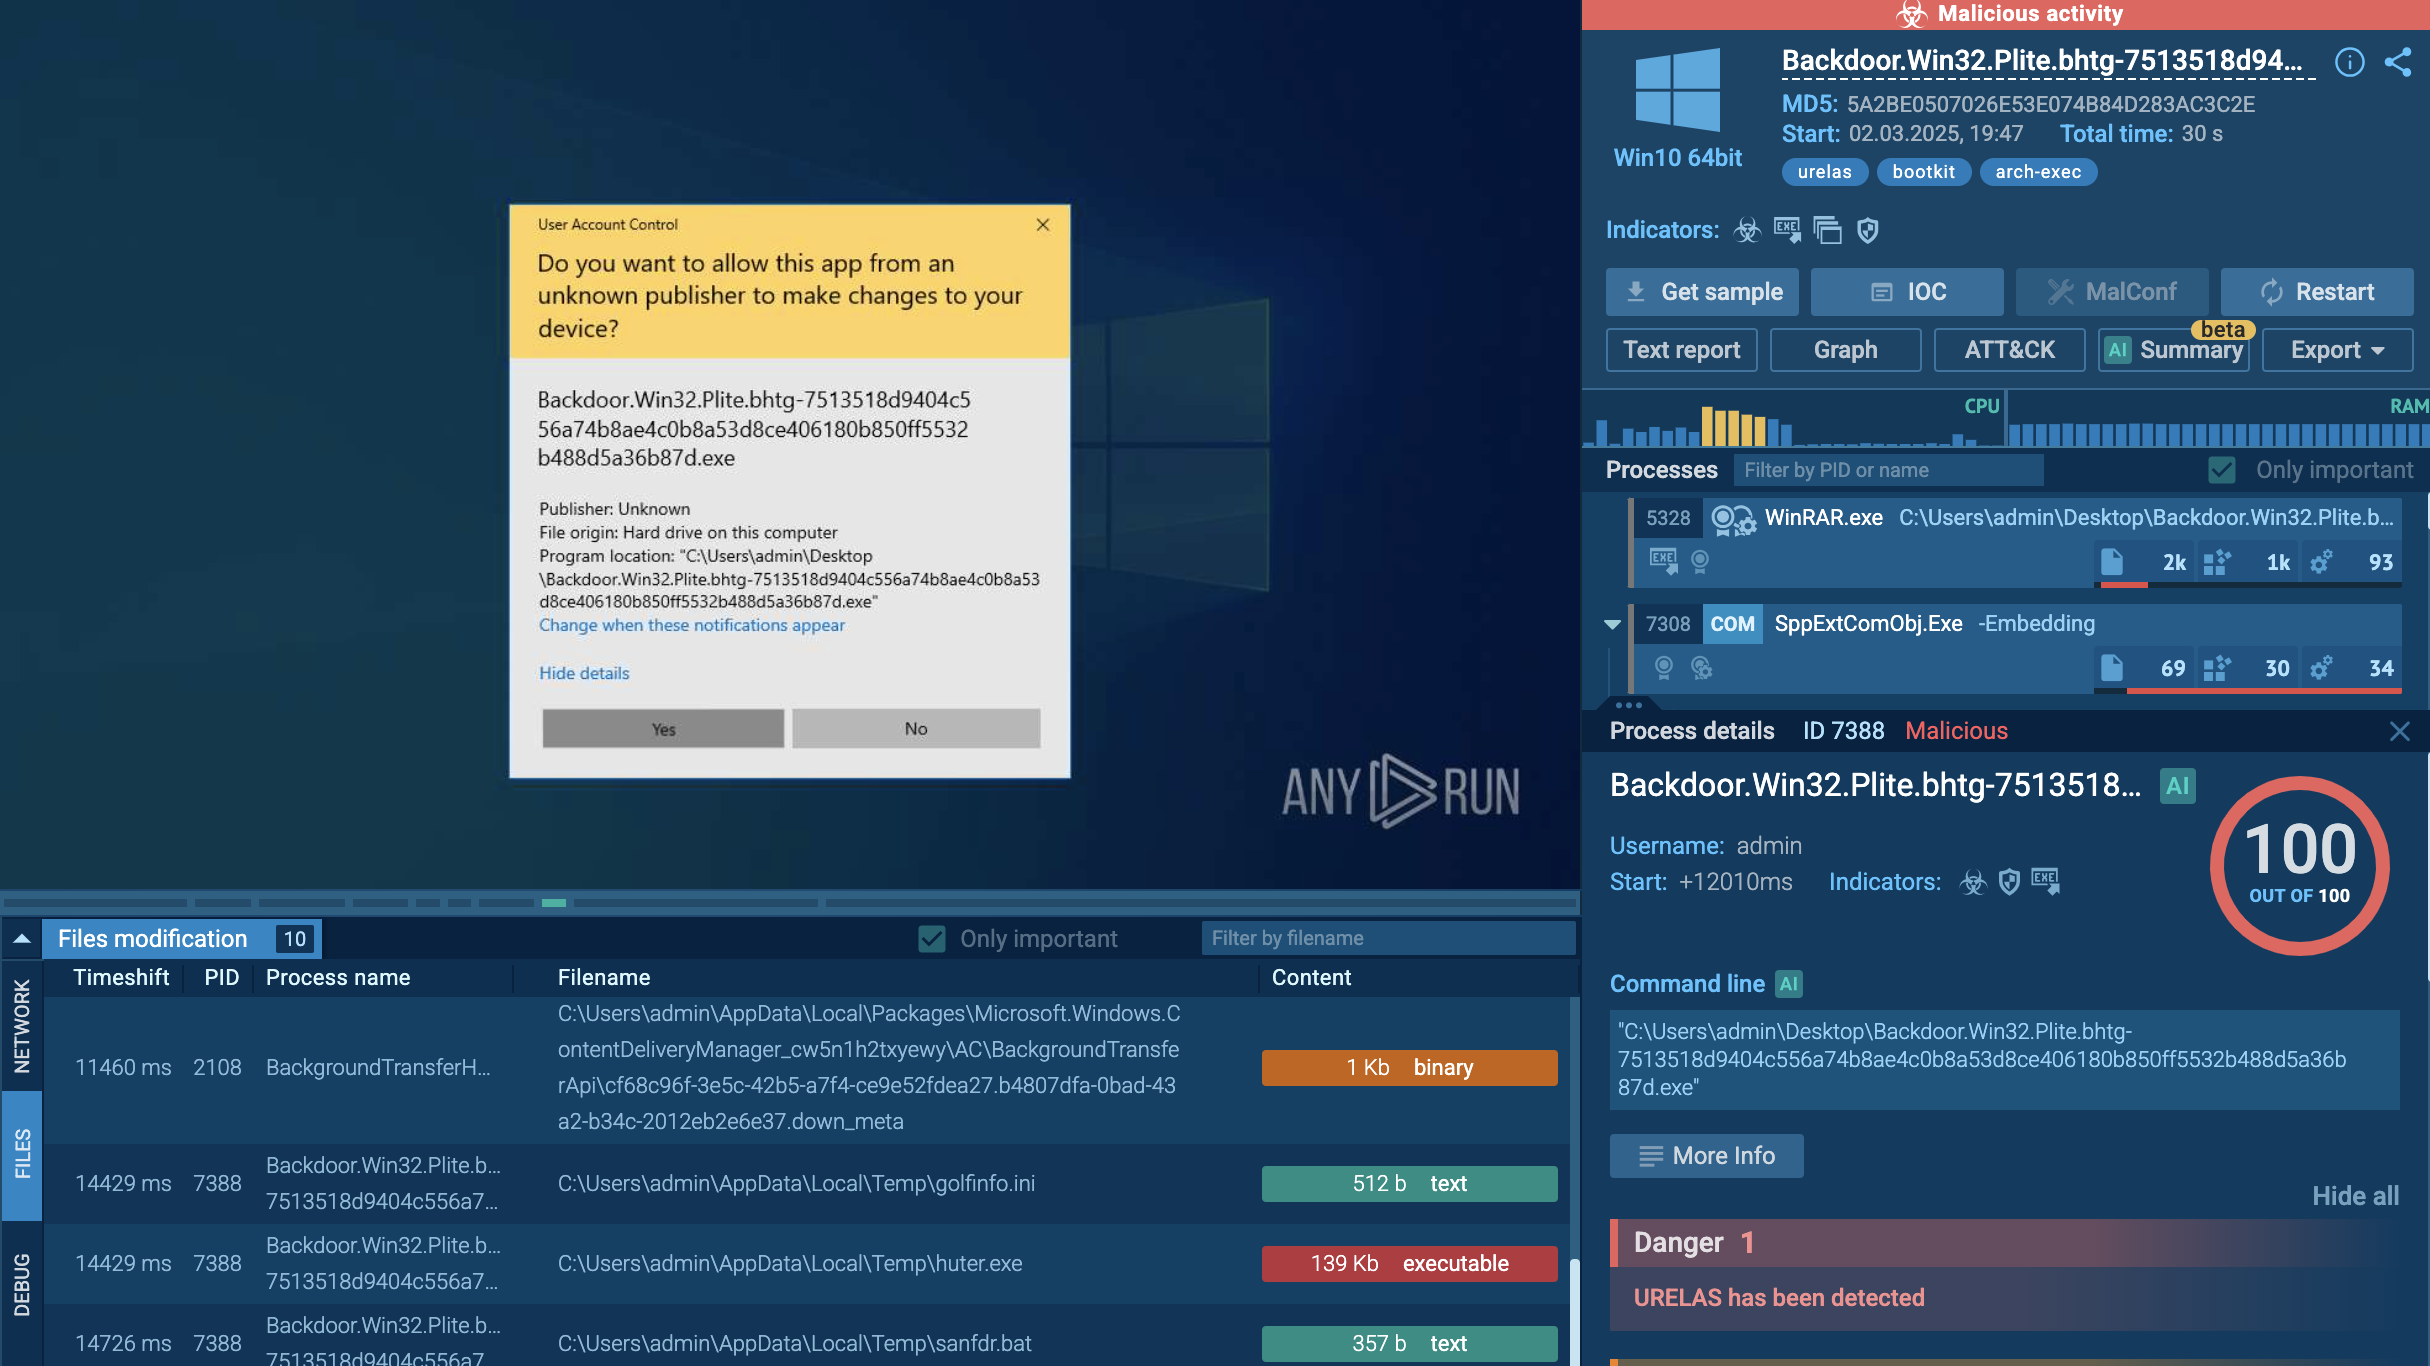 RootkitA rootkit is a type of malicious software designed to provide unauthorized administrative-level access to a computer or network while concealing its presence. Rootkits are tools used by cybercriminals to hide their activities, including keyloggers, spyware, and other malware, often enabling long-term system exploitation.
 Caminho LoaderCaminho Loader is a Brazilian-origin Loader-as-a-Service operation that uses steganography to conceal .NET payloads within image files hosted on legitimate platforms. Active since March 2025, it has delivered a variety of malware and infostealers to victims within multiple industries across South America, Africa, and Eastern Europe.
 FormbookFormBook is a data stealer that is being distributed as a MaaS. FormBook differs from a lot of competing malware by its extreme ease of use that allows even the unexperienced
threat actors to use FormBook virus.
 Salvador StealerSalvador Stealer is a powerful, information-stealing Android malware designed to silently infiltrate systems, extract sensitive data, and exfiltrate it to cybercriminals. Often sold on underground forums, it is part of the growing ecosystem of “stealers-as-a-service” (SaaS) tools that target individuals and organizations alike.
 KratosKratos is a mature Phishing-as-a-Service (PhaaS) platform that evolved from the Sneaky2FA kit to specialize in stealing Microsoft 365 credentials through sophisticated Adversary-in-the-Middle (AiTM) techniques. The service provides low-skilled affiliates with a turnkey solution featuring an advanced administrative dashboard, integrated anti-bot defenses, and real-time data exfiltration via the Telegram Bot API. Although an international law enforcement action known as Operation Olympus Blade disrupted its central infrastructure in July 2026, the kit remains a primary example of the industrialization of modern cybercrime.